
Microsoft AZ-500 Practice Exams
Last updated on Nov 16,2026- Exam Code: AZ-500
- Exam Name: Microsoft Azure Security Technologies
- Certification Provider: Microsoft
- Latest update: Nov 16,2026
SIMULATION
Lab Task
Task 1
You need to ensure that connections from the Internet to VNET1subnet0 are allowed only over TCP port 7777. The solution must use only currently deployed resources.
You have an Azure subscription named Sub1.
In Azure Security Center, you have a workflow automation named WF1. WF1 is configured to send an email message to a user named User1.
You need to modify WF1 to send email messages to a distribution group named Alerts.
What should you use to modify WF1?
- A . Azure Application Insights
- B . Azure Monitor
- C . Azure Logic Apps Designer
- D . Azure DevOps
HOTSPOT
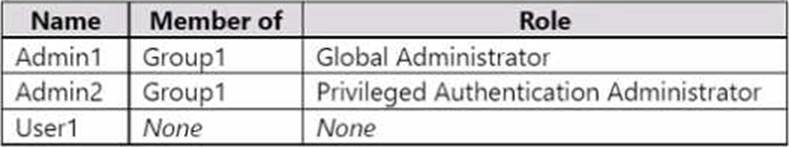
You have a Microsoft Entra tenant that contains the users shown in the following table.
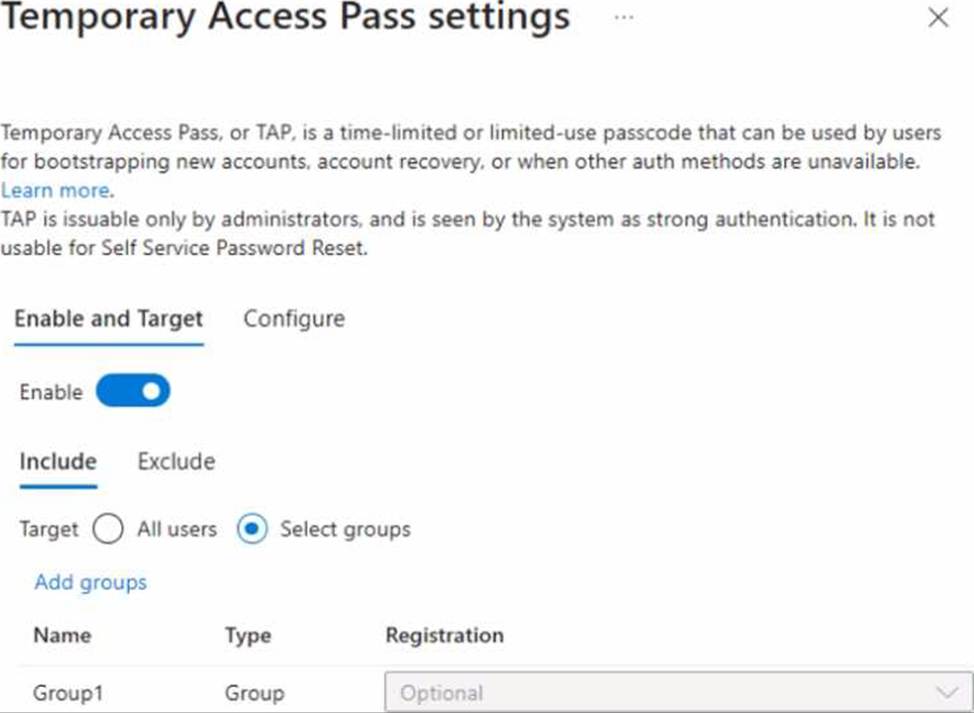
You configure the Temporary Access Pass settings as shown in the following exhibit.
You add the Temporary Access Pass authentication method to Admin2.
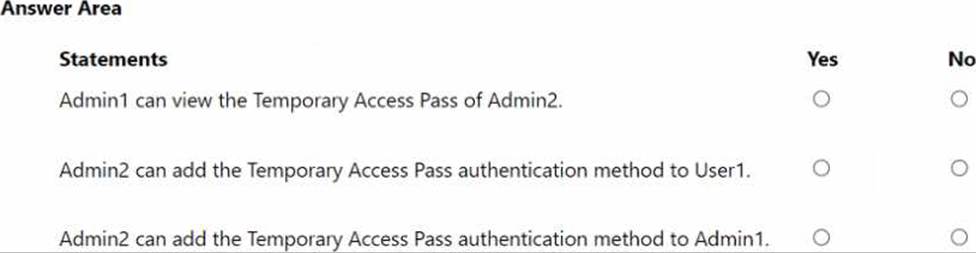
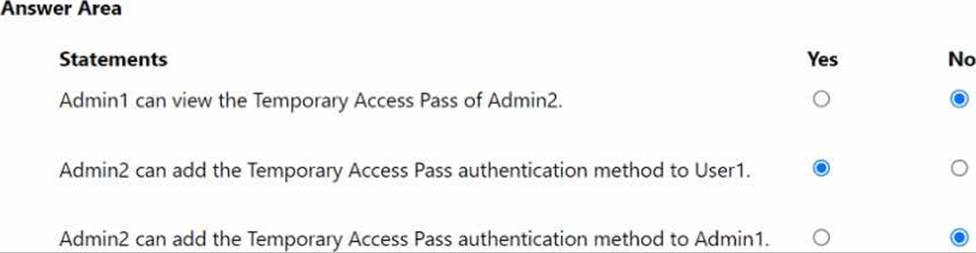
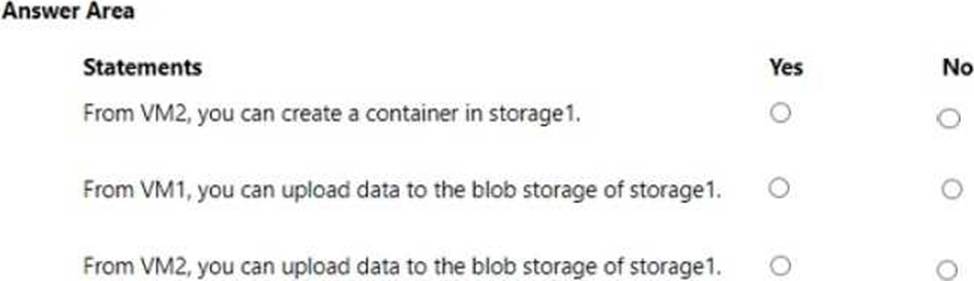
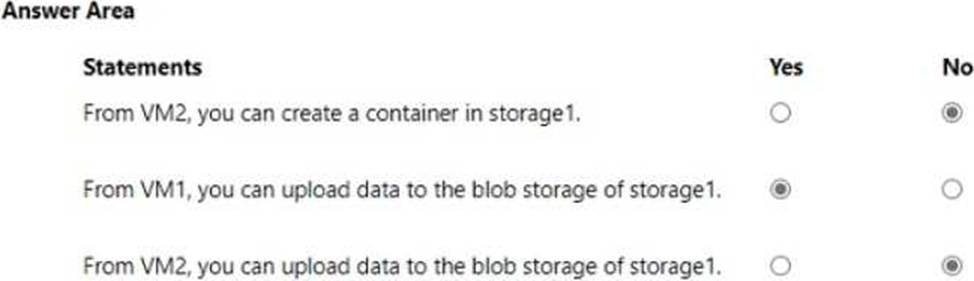
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
HOTSPOT
You have an Azure subscription that contains the virtual machines shown in the following table.
Subnet1 and Subnet2 have a network security group {NSG).
The NSG has an outbound rule that has the following configurations:
• Port; Any
• Source: Any
• Priority: 100
• Action: Deny
• Protocol: Any
• Destination: Storage
The subscription contains a storage account named storage1.
You create a private endpoint named Private1 that has the following settings:
• Resource type: Microsoft.Storage/storageAccounts
• Resource: storage1
• Target sub-resource: blob
• Virtual network: VNet1
• Subnet: Subnet1
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
You have an Azure Kubernetes Service (AKS) cluster that will connect to an Azure Container Registry.
You need to use automatically generated service principal for the AKS cluster to authenticate to the Azure Container Registry.
What should you create?
- A . a secret in Azure Key Vault
- B . a role assignment
- C . an Azure Active Directory (Azure AD) user
- D . an Azure Active Directory (Azure AD) group
Lab Task
Task 3
You need to ensure that a user named Danny-31330471 can sign in to any SQL database on a Microsoft SQL server named web31330471 by using SQL Server Management Studio (SSMS) and Azure AD credentials.
HOTSPOT
You have an Azure subscription that contains the resources shown in the following table.
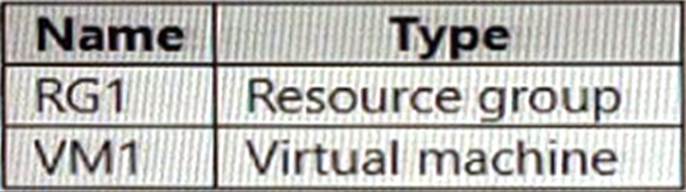
You perform the following tasks:
– Create a managed identity named Managed1.
– Create a Microsoft 365 group named Group1.
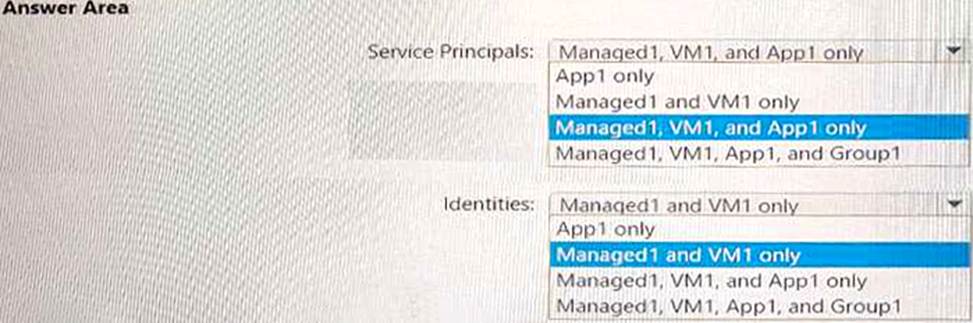
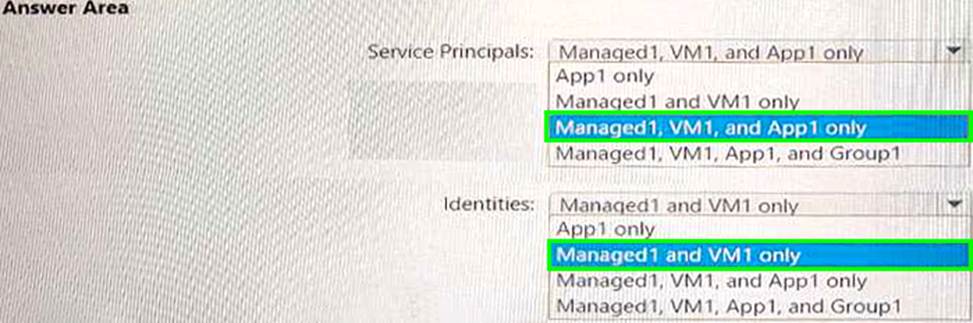
You need to identify which service principals were created and which identities can be assigned the Reader role for RG1.
What should you identify? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
Your network contains an Active Directory forest named contoso.com. You have an Azure Directory (Azure AD) tenant named contoso.com.
You plan to configure synchronization by using the Express Settings installation option in Azure AD Connect.
You need to identify which roles and groups are required to perform the planned configurations. The solution must use the principle of least privilege.
Which two roles and groups should you identify? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A . the Domain Admins group in Active Directory
- B . the Security administrator role in Azure AD
- C . the Global administrator role in Azure AD
- D . the User administrator role in Azure AD
- E . the Enterprise Admins group in Active Directory
SIMULATION
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: User1 [email protected]
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 7
You need to collect all the audit failure data from the security log of a virtual machine named VM1 to an Azure Storage account. To complete this task, sign in to the Azure portal.
You have an Azure subscription that contains a managed identity named Identity1 and the Azure key vaults shown in the following table.
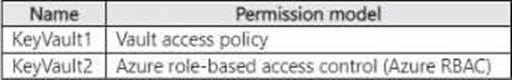
Key Vault1 contains an access policy that grants Identity1 the following key permissions:
• Get
• List
• Wrap
• Unwrap
You need to provide Identity1 with the same permissions for KeyVault2. The solution must use the principle of least privilege.
Which role should you assign to Identity1?
- A . Key Vault Crypto Service Encryption User
- B . Key Vault Crypto User
- C . Key Vault Reader
- D . Key Vault Crypto Officer