
Juniper JN0-231 Practice Exams
Last updated on Oct 22,2026- Exam Code: JN0-231
- Exam Name: Security - Associate (JNCIA-SEC)
- Certification Provider: Juniper
- Latest update: Oct 22,2026
What must be enabled on an SRX Series device for the reporting engine to create reports?
- A . packet capture
- B . security logging
- C . system logging
- D . SNMP
Click the Exhibit button.
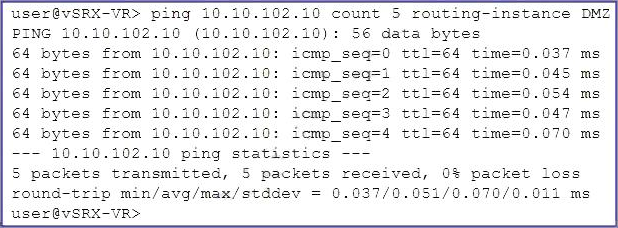
Referring to the exhibit, which two statements are correct about the ping command? (Choose two.)
- A . The DMZ routing-instance is the source.
- B . The 10.10.102.10 IP address is the source.
- C . The 10.10.102.10 IP address is the destination.
- D . The DMZ routing-instance is the destination.
You want to provide remote access to an internal development environment for 10 remote developers.
Which two components are required to implement Juniper Secure Connect to satisfy this requirement? (Choose two.)
- A . an additional license for an SRX Series device
- B . Juniper Secure Connect client software
- C . an SRX Series device with an SPC3 services card
- D . Marvis virtual network assistant
What is the default timeout value for TCP sessions on an SRX Series device?
- A . 30 seconds
- B . 60 minutes
- C . 60 seconds
- D . 30 minutes
D
Explanation:
By default, TCP has a 30-minute idle timeout, and UDP has a 60-second idle timeout. Additionally, known IP protocols have a 30-minute timeout, whereas unknown ones have a 60-second timeout. Setting the inactivity timeout is very useful, particularly if you are concerned about applications either timing out or remaining idle for too long and filling up the session table. According to the Juniper SRX Series Services Guide, this can be configured using the ‘timeout inactive’ statement for the security policy.
Which two addresses are valid address book entries? (Choose two.)
- A . 173.145.5.21/255.255.255.0
- B . 153.146.0.145/255.255.0.255
- C . 203.150.108.10/24
- D . 191.168.203.0/24
A,C
Explanation:
The correct address book entries are:
✑ 173.145.5.21/255.255.255.0
✑ 203.150.108.10/24
Both of these entries represent a valid IP address and subnet mask combination, which can be used as an address book entry in a Juniper device.
What are two functions of Juniper ATP Cloud? (Choose two.)
- A . malware inspection
- B . Web content filtering
- C . DDoS protection
- D . Geo IP feeds
A,D
Explanation:
Juniper Advanced Threat Prevention (ATP) Cloud is a security service that helps organizations protect against advanced threats by providing real-time threat intelligence and automated response capabilities. It combines a cloud-based threat intelligence platform with the security capabilities of Juniper Networks security devices to provide comprehensive protection against advanced threats. The two functions of Juniper ATP Cloud include malware inspection and Geo IP feeds. The malware inspection component provides real-time protection against known and unknown threats by analyzing suspicious files and determining if they are malicious. The Geo IP feeds provide a global view of IP addresses and their associated countries, allowing organizations to identify and block traffic from known malicious countries.
Which statement is correct about global security policies on SRX Series devices?
- A . The to-zone any command configures a global policy.
- B . The from-zone any command configures a global policy.
- C . Global policies are always evaluated first.
- D . Global policies can include zone context.
When c onfiguring antispam, where do you apply any local lists that are configured?
- A . custom objects
- B . advanced security policy
- C . antispam feature-profile
- D . antispam UTM policy
You are configuring an SRX Series device. You have a set of servers inside your private network that need one-to-one mappings to public IP addresses.
Which NAT configuration is appropriate in this scenario?
- A . source NAT with PAT
- B . destination NAT
- C . NAT-T
- D . static NAT
Which two statements are correct about IPsec security associations? (Choose two.)
- A . IPsec security associations are bidirectional.
- B . IPsec security associations are unidirectional.
- C . IPsec security associations are established during IKE Phase 1 negotiations.
- D . IPsec security associations are established during IKE Phase 2 negotiations.
A,D
Explanation:
The two statements that are correct about IPsec security associations are that they are bidirectional and that they are established during IKE Phase 2 negotiations. IPsec security associations are bidirectional, meaning that they provide security for both incoming and outgoing traffic. IPsec security associations are established during IKE Phase 2 negotiations, which negotiates the security parameters and establishes the security association between the two peers. For more information, please refer to the Juniper Networks IPsec VPN Configuration Guide, which can be found on Juniper’s website.