
Google Professional Cloud Developer Practice Exams
Last updated on Oct 24,2026- Exam Code: Professional Cloud Developer
- Exam Name: Professional Cloud Developer
- Certification Provider: Google
- Latest update: Oct 24,2026
You are developing an application using different microservices that should remain internal to the cluster. You want to be able to configure each microservice with a specific number of replicas. You also want to be able to address a specific microservice from any other microservice in a uniform way, regardless of the number of replicas the microservice scales to. You need to implement this solution on Google Kubernetes Engine.
What should you do?
- A . Deploy each microservice as a Deployment. Expose the Deployment in the cluster using a Service, and use the Service DNS name to address it from other microservices within the cluster.
- B . Deploy each microservice as a Deployment. Expose the Deployment in the cluster using an Ingress, and use the Ingress IP address to address the Deployment from other microservices within the cluster.
- C . Deploy each microservice as a Pod. Expose the Pod in the cluster using a Service, and use the Service DNS name to address the microservice from other microservices within the cluster.
- D . Deploy each microservice as a Pod. Expose the Pod in the cluster using an Ingress, and use the
Ingress IP address name to address the Pod from other microservices within the cluster.
You are developing an internal application that will allow employees to organize community events within your company. You deployed your application on a single Compute Engine instance. Your company uses Google Workspace (formerly G Suite), and you need to ensure that the company employees can authenticate to the application from anywhere.
What should you do?
- A . Add a public IP address to your instance, and restrict access to the instance using firewall rules.
Allow your company’s proxy as the only source IP address. - B . Add an HTTP(S) load balancer in front of the instance, and set up Identity-Aware Proxy (IAP).
Configure the IAP settings to allow your company domain to access the website. - C . Set up a VPN tunnel between your company network and your instance’s VPC location on Google Cloud. Configure the required firewall rules and routing information to both the on-premises and Google Cloud networks.
- D . Add a public IP address to your instance, and allow traffic from the internet. Generate a random hash, and create a subdomain that includes this hash and points to your instance. Distribute this DNS address to your company’s employees.
B
Explanation:
https://cloud.google.com/blog/topics/developers-practitioners/control-access-your-web-sites-identity-aware-proxy
Your company’s development teams want to use Cloud Build in their projects to build and push Docker images to Container Registry. The operations team requires all Docker images to be published to a centralized, securely managed Docker registry that the operations team manages.
What should you do?
- A . Use Container Registry to create a registry in each development team’s project. Configure the Cloud Build build to push the Docker image to the project’s registry. Grant the operations team access to each development team’s registry.
- B . Create a separate project for the operations team that has Container Registry configured. Assign appropriate permissions to the Cloud Build service account in each developer team’s project to allow access to the operation team’s registry.
- C . Create a separate project for the operations team that has Container Registry configured. Create a Service Account for each development team and assign the appropriate permissions to allow it access to the operations team’s registry. Store the service account key file in the source code repository and use it to authenticate against the operations team’s registry.
- D . Create a separate project for the operations team that has the open source Docker Registry deployed on a Compute Engine virtual machine instance. Create a username and password for each development team. Store the username and password in the source code repository and use it to authenticate against the operations team’s Docker registry.
A
Explanation:
Reference: https://cloud.google.com/container-registry/
You have an application deployed in production. When a new version is deployed, some issues don’t arise until the application receives traffic from users in production. You want to reduce both the impact and the number of users affected.
Which deployment strategy should you use?
- A . Blue/green deployment
- B . Canary deployment
- C . Rolling deployment
- D . Recreate deployment
A
Explanation:
Reference: https://thenewstack.io/deployment-strategies/
For this question, refer to the HipLocal case study.
How should HipLocal redesign their architecture to ensure that the application scales to support a large increase in users?
- A . Use Google Kubernetes Engine (GKE) to run the application as a microservice. Run the MySQL database on a dedicated GKE node.
- B . Use multiple Compute Engine instances to run MySQL to store state information. Use a Google Cloud-managed load balancer to distribute the load between instances. Use managed instance groups for scaling.
- C . Use Memorystore to store session information and CloudSQL to store state information. Use a Google Cloud-managed load balancer to distribute the load between instances. Use managed instance groups for scaling.
- D . Use a Cloud Storage bucket to serve the application as a static website, and use another Cloud Storage bucket to store user state information.
You are designing a resource-sharing policy for applications used by different teams in a Google Kubernetes Engine cluster. You need to ensure that all applications can access the resources needed to run.
What should you do? (Choose two.)
- A . Specify the resource limits and requests in the object specifications.
- B . Create a namespace for each team, and attach resource quotas to each namespace.
- C . Create a LimitRange to specify the default compute resource requirements for each namespace.
- D . Create a Kubernetes service account (KSA) for each application, and assign each KSA to the namespace.
- E . Use the Anthos Policy Controller to enforce label annotations on all namespaces. Use taints and tolerations to allow resource sharing for namespaces.
BC
Explanation:
https://kubernetes.io/docs/concepts/policy/resource-quotas/
https://kubernetes.io/docs/concepts/policy/limit-range/
https://cloud.google.com/blog/products/containers-kubernetes/kubernetes-best-practices-resource-requests-and-limits
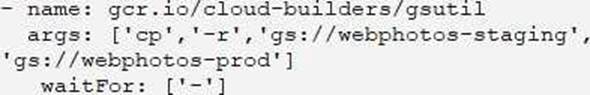
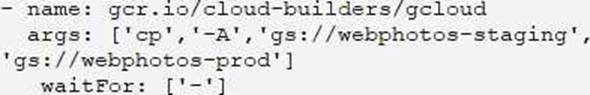
Your development team is using Cloud Build to promote a Node.js application built on App Engine from your staging environment to production. The application relies on several directories of photos stored in a Cloud Storage bucket named webphotos-staging in the staging environment. After the promotion, these photos must be available in a Cloud Storage bucket named webphotos-prod in the production environment. You want to automate the process where possible.
What should you do?
A) Manually copy the photos to webphotos-prod.
B) Add a startup script in the application’s app.yami file to move the photos from webphotos-staging to
webphotos-prod.
C) Add a build step in the cloudbuild.yaml file before the promotion step with the arguments:
D) Add a build step in the cloudbuild.yaml file before the promotion step with the arguments:
- A . Option A
- B . Option B
- C . Option C
- D . Option D
C
Explanation:
https://cloud.google.com/storage/docs/gsutil/commands/cp
You are developing an HTTP API hosted on a Compute Engine virtual machine instance that needs to be invoked by multiple clients within the same Virtual Private Cloud (VPC). You want clients to be able to get the IP address of the service.
What should you do?
- A . Reserve a static external IP address and assign it to an HTTP(S) load balancing service’s forwarding rule. Clients should use this IP address to connect to the service.
- B . Reserve a static external IP address and assign it to an HTTP(S) load balancing service’s forwarding rule. Then, define an A record in Cloud DNS. Clients should use the name of the A record to connect to the service.
- C . Ensure that clients use Compute Engine internal DNS by connecting to the instance name with the url https://[INSTANCE_NAME].[ZONE].c.[PROJECT_ID].internal/.
- D . Ensure that clients use Compute Engine internal DNS by connecting to the instance name with the url https://[API_NAME]/[API_VERSION]/.