
Fortinet NSE7_OTS-7.2.0 Practice Exams
Last updated on Oct 22,2026- Exam Code: NSE7_OTS-7.2.0
- Exam Name: Fortinet NSE 7 - OT Security 7.2.0
- Certification Provider: Fortinet
- Latest update: Oct 22,2026
Which three Fortinet products can be used for device identification in an OT industrial control system (ICS)? (Choose three.)
- A . FortiNAC
- B . FortiManager
- C . FortiAnalyzer
- D . FortiSIEM
- E . FortiGate
ADE
Explanation:
A) FortiNAC – FortiNAC is a network access control solution that provides visibility and control over network devices. It can identify devices, enforce access policies, and automate threat response.
D) FortiSIEM – FortiSIEM is a security information and event management solution that can collect and analyze data from multiple sources, including network devices and servers. It can help identify potential security threats, as well as monitor compliance with security policies and regulations.
E) FortiAnalyzer – FortiAnalyzer is a central logging and reporting solution that collects and analyzes data from multiple sources, including FortiNAC and FortiSIEM. It can provide insights into network activity and help identify anomalies or security threats.
Reference: Fortinet NSE 7 – OT Security 6.4 Study Guide, Chapter 4: OT Security Devices, page 4-20.
Refer to the exhibit.
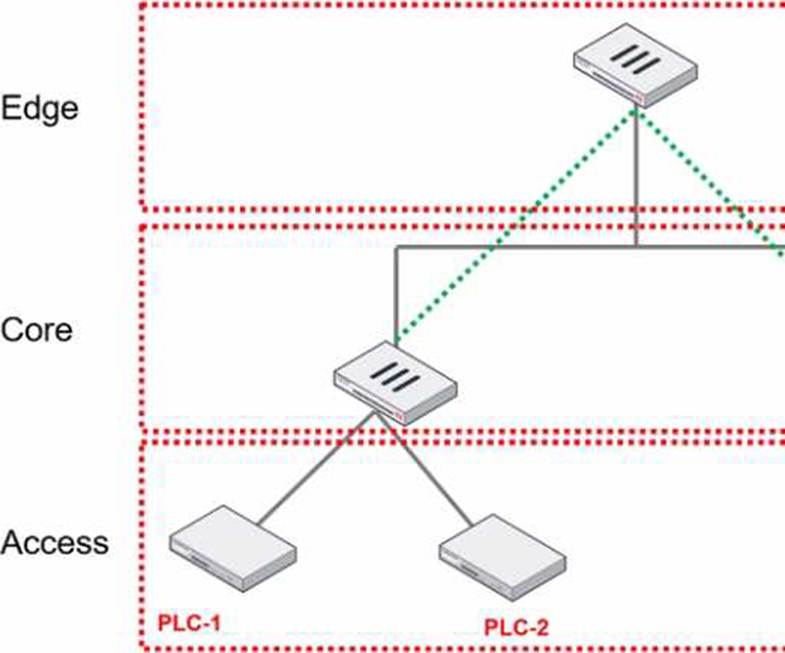
You are assigned to implement a remote authentication server in the OT network.
Which part of the hierarchy should the authentication server be part of?
- A . Edge
- B . Cloud
- C . Core
- D . Access
Refer to the exhibit
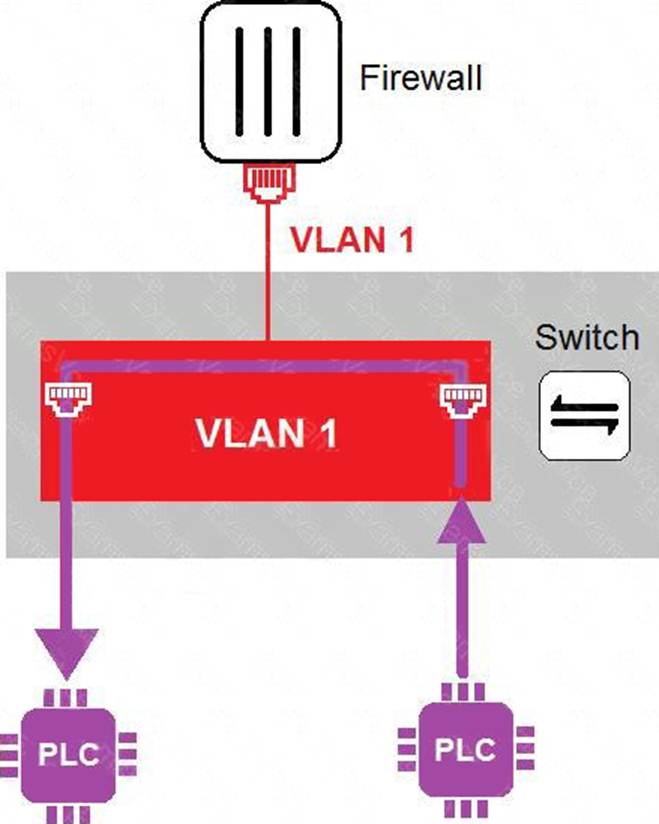
In the topology shown in the exhibit, both PLCs can communicate directly with each other, without going through the firewall.
Which statement about the topology is true?
- A . PLCs use IEEE802.1Q protocol to communicate each other.
- B . An administrator can create firewall policies in the switch to secure between PLCs.
- C . This integration solution expands VLAN capabilities from Layer 2 to Layer 3.
- D . There is no micro-segmentation in this topology.
Refer to the exhibit.
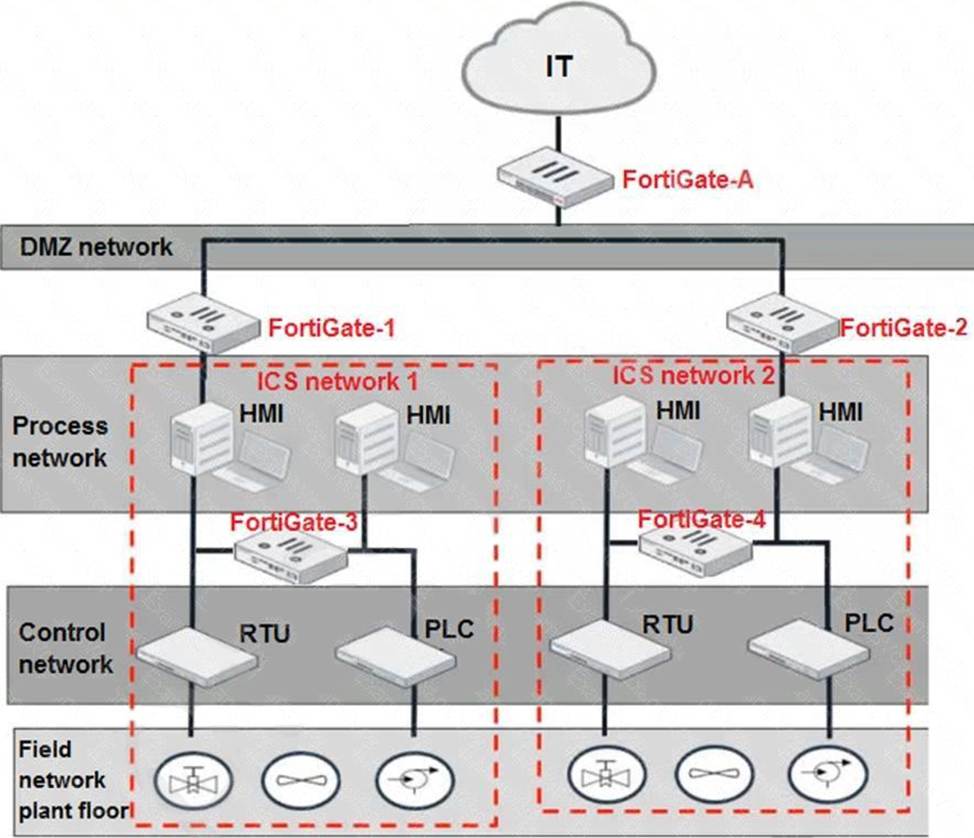
Based on the topology designed by the OT architect, which two statements about implementing OT security are true? (Choose two.)
- A . Firewall policies should be configured on FortiGate-3 and FortiGate-4 with industrial protocol sensors.
- B . Micro-segmentation can be achieved only by replacing FortiGate-3 and FortiGate-4 with a pair of FortiSwitch devices.
- C . IT and OT networks are separated by segmentation.
- D . FortiGate-3 and FortiGate-4 devices must be in a transparent mode.
The OT network analyst runs different level of reports to quickly explore threats that exploit the network. Such reports can be run on all routers, switches, and firewalls.
Which FortiSIEM reporting method helps to identify these type of exploits of image firmware files?
- A . CMDB reports
- B . Threat hunting reports
- C . Compliance reports
- D . OT/loT reports
An OT architect has deployed a Layer 2 switch in the OT network at Level 1 the Purdue model-process control. The purpose of the Layer 2 switch is to segment traffic between PLC1 and PLC2 with two VLANs. All the traffic between PLC1 and PLC2 must first flow through the Layer 2 switch and then through the FortiGate device in the Level 2 supervisory control network.
What statement about the traffic between PLC1 and PLC2 is true?
- A . The Layer 2 switch rewrites VLAN tags before sending traffic to the FortiGate device.
- B . The Layer 2 switches routes any traffic to the FortiGate device through an Ethernet link.
- C . PLC1 and PLC2 traffic must flow through the Layer-2 switch trunk link to the FortiGate device.
- D . In order to communicate, PLC1 must be in the same VLAN as PLC2.
C
Explanation:
The statement that is true about the traffic between PLC1 and PLC2 is that PLC1 and PLC2 traffic must flow through the Layer-2 switch trunk link to the FortiGate device.
Refer to the exhibit.
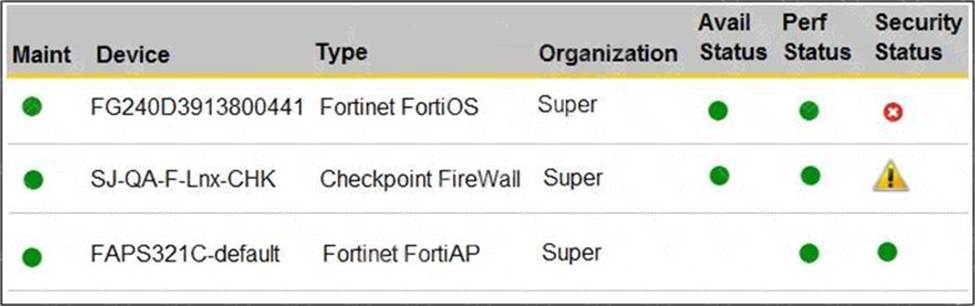
You are navigating through FortiSIEM in an OT network.
How do you view information presented in the exhibit and what does the FortiGate device security status tell you?
- A . In the PCI logging dashboard and there are one or more high-severity security incidents for the FortiGate device.
- B . In the summary dashboard and there are one or more high-severity security incidents for the FortiGate device.
- C . In the widget dashboard and there are one or more high-severity incidents for the FortiGate device.
- D . In the business service dashboard and there are one or more high-severity security incidents for the FortiGate device.
What are two benefits of a Nozomi integration with FortiNAC? (Choose two.)
- A . Enhanced point of connection details
- B . Direct VLAN assignment
- C . Adapter consolidation for multi-adapter hosts
- D . Importation and classification of hosts
C, D
Explanation:
The two benefits of a Nozomi integration with FortiNAC are enhanced point of connection details and importation and classification of hosts. Enhanced point of connection details allows for the identification and separation of traffic from multiple points of connection, such as Wi-Fi, wired, cellular, and VPN. Importation and classification of hosts allows for the automated importing and classification of host and device information into FortiNAC. This allows for better visibility and control of the network.
Refer to the exhibits.
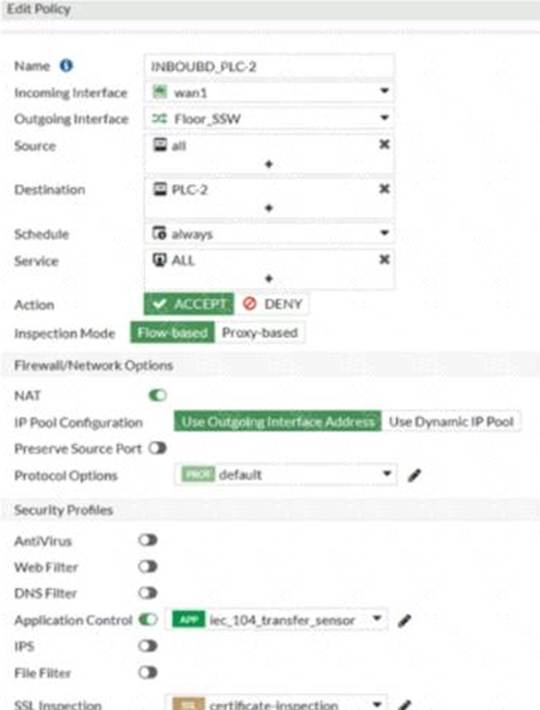
Which statement is true about the traffic passing through to PLC-2?
- A . IPS must be enabled to inspect application signatures.
- B . The application filter overrides the default action of some IEC 104 signatures.
- C . IEC 104 signatures are all allowed except the C.BO.NA 1 signature.
- D . SSL Inspection must be set to deep-inspection to correctly apply application control.
What triggers Layer 2 polling of infrastructure devices connected in the network?
- A . A failed Layer 3 poll
- B . A matched security policy
- C . A matched profiling rule
- D . A linkup or linkdown trap