
Fortinet FCSS_NST_SE-7.4 Practice Exams
Last updated on Oct 21,2026- Exam Code: FCSS_NST_SE-7.4
- Exam Name: FCSS - Network Security 7.4 Support Engineer
- Certification Provider: Fortinet
- Latest update: Oct 21,2026
Refer to the exhibit, which shows the output of a policy route table entry.

Which type of policy route does the output show?
- A . An ISDB route
- B . A regular policy route
- C . A regular policy route, which is associated with an active static route in the FIB
- D . An SD-WAN rule
Refer to the exhibits.
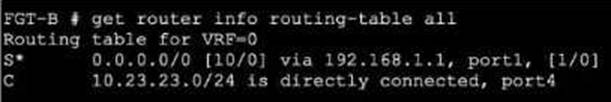
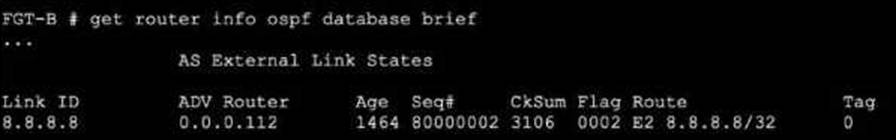
An administrator Is expecting to receive advertised route 8.8.8.8/32 from FGT-A. On FGT-B, they confirm that the route is being advertised and received, however, the route is not being injected into the routing table.
What is the most likely cause of this issue?
- A . A batter route to the 8.8.8.8/32 network exists in the routing table.
- B . FGT-B is configured with a prefix list denying the 8.8.8.8/32 network to be injected into the routing table.
- C . The administrator has misconfigured redistribution of routes on FGT-A.
- D . FGT-8 is configured with a distribution list denying the 8.8.8.8/32 network to be injected into the routing table.
Exhibit.
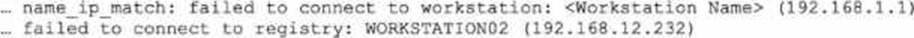
Refer to the exhibit, which shows two entries that were generated in the FSSO collector agent logs.
What three conclusions can you draw from these log entries? {Choose three.)
- A . Remote registry is not running on the workstation.
- B . The user’s status shows as "not verified" in the collector agent.
- C . DNS resolution is unable to resolve the workstation name.
- D . The FortiGate firmware version is not compatible with that of the collector agent.
- E . A firewall is blocking traffic to port 139 and 445.
Refer to the exhibit, which shows the omitted output of a session table entry.
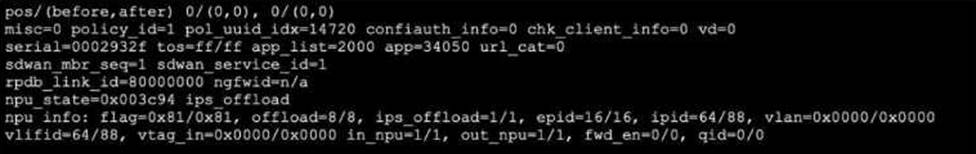
Which two statements are true? (Choose two.)
- A . The traffic has been tagged for VLAN 0000.
- B . NP7 is handling offloading of this session.
- C . The traffic matches Policy ID 1.
- D . The session has been offloaded.
What are two reasons you might see iprope_in_check() check failed, drop when using the debug flow? (Choose two.)
- A . Packet was dropped because of policy route misconfiguration.
- B . Packet was dropped because of traffic shaping.
- C . Trusted host list misconfiguration.
- D . VIP or IP pool misconfiguration.
Refer to the exhibit.
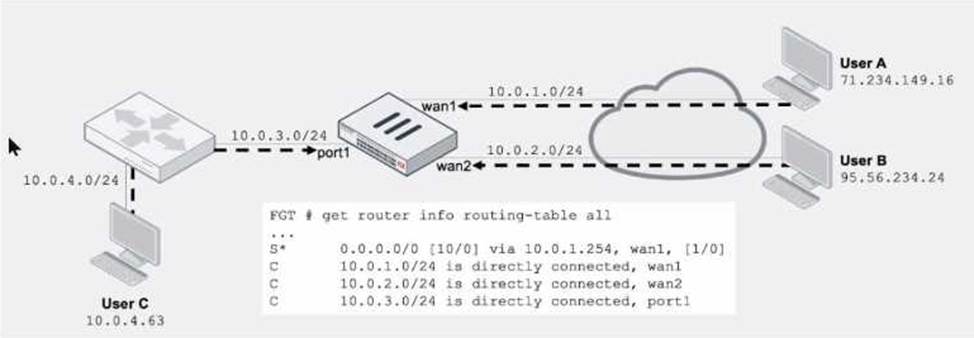
Assuming a default configuration, which three statements are true? (Choose three.)
- A . Strict RPF is enabled by default.
- B . User B: Fail. There is no route to 95.56.234.24 using wan2 in the routing table.
- C . User A: Pass. The default static route through wan1 passes the RPF check regardless of the source IP address.
- D . User B: Pass. FortiGate will use asymmetric routing using wan1 to reply to traffic for 95.56.234.24.
- E . User C: Fail. There is no route to 10.0.4.63 using port1 in the touting table.
Exhibit.
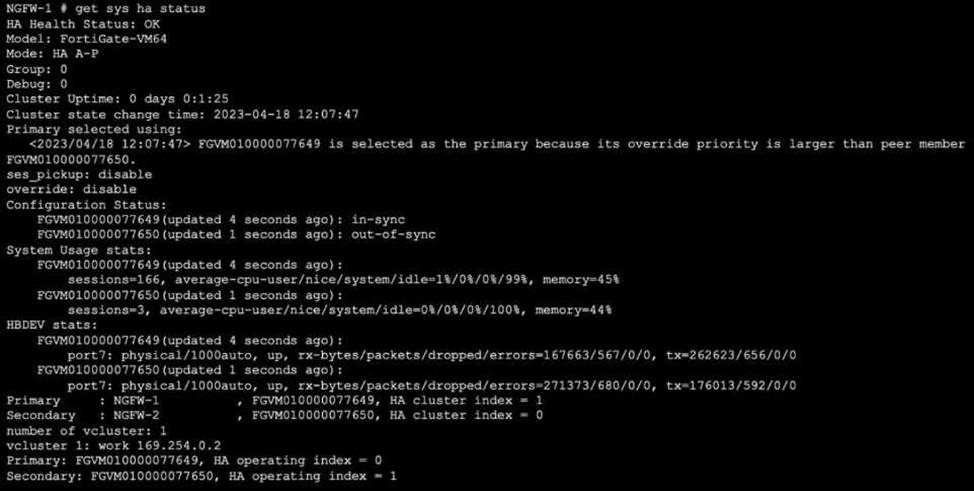
Refer to the exhibit, which shows the output of get system ha status.
NGFW-1 and NGFW-2 have been up for a week.
Which two statements about the output are true? (Choose two.)
- A . If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.
- B . If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.
- C . If FGVM…649 is rebooted. FGVM…650 will become the primary and retain that role, even after FGVM…649 rejoins the cluster.
- D . If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.
Which two statements about Security Fabric communications are true? (Choose two.)
- A . FortiTelemetry and Neighbor Discovery both operate using TCP.
- B . The default port for Neighbor Discovery can be modified.
- C . FortiTelemetry must be manually enabled on the FortiGate interface.
- D . By default, the downstream FortiGate establishes a connection with the upstream FortiGate using TCP port 8013.
Exhibit.
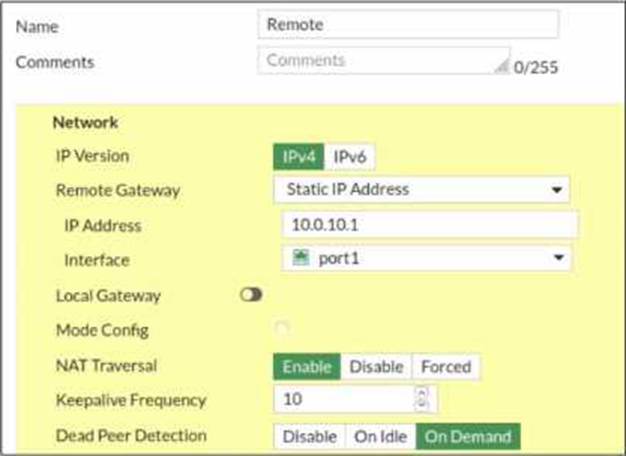
Refer to the exhibit, which contains a screenshot of some phase 1 settings.
The VPN is not up. To diagnose the issue, the administrator enters the following CLI commands on an SSH session on FortiGate:

However, the IKE real-time debug does not show any output.
Why?
- A . The administrator must also run the command diagnose debug enable.
- B . The debug shows only error messages. If there is no output, then the phase 1 and phase 2 configurations match.
- C . The log-filter setting is incorrect. The VPN traffic does not match this filter.
- D . Replace diagnose debug application ike -1 with diagnose debug application ipsec -1.
Refer to the exhibit, which shows the output of get router info ospf neighbor.
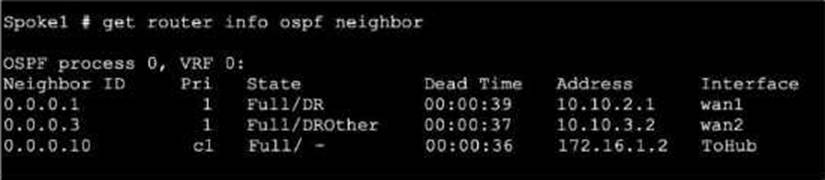
What can you conclude from the command output?
- A . The network type connecting the local Fortigate and OSPF neighbor 0.0.0.10 is point-to-point.
- B . All neighbors are in area 0.0.0.0.
- C . The local FortiGate is the BDR.
- D . The local FortiGate is not a DROther.