
Fortinet FCSS_EFW_AD-7.4 Practice Exams
Last updated on Oct 22,2026- Exam Code: FCSS_EFW_AD-7.4
- Exam Name: FCSS - Enterprise Firewall 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Oct 22,2026
An administrator has been assigned the task of creating a set of firewall policies which must be evaluated before any custom policies defined within the policy packages of managed FortiGate devices, across all 25 ADOMSs in FortiManager.
How should the administrator accomplish this task?
- A . Create a footer policy in the Global ADOM containing the firewall policies that must be evaluated first, and then assign this footer policy to all other ADOMs.
- B . Create a header policy in the Global ADOM containing the firewall policies that must be evaluated first, and then assign this header policy to all other ADOMs.
- C . Move the FortiGate devices into a single globally scoped ADOM, and merge policy packages, inserting the new firewall policies at the top.
- D . Use a CLI script from the root ADOM on FortiManager to push these new policies to all FortiGate devices, through the FGFM tunnel.
Examine the IPsec configuration shown in the exhibit; then answer the question below.
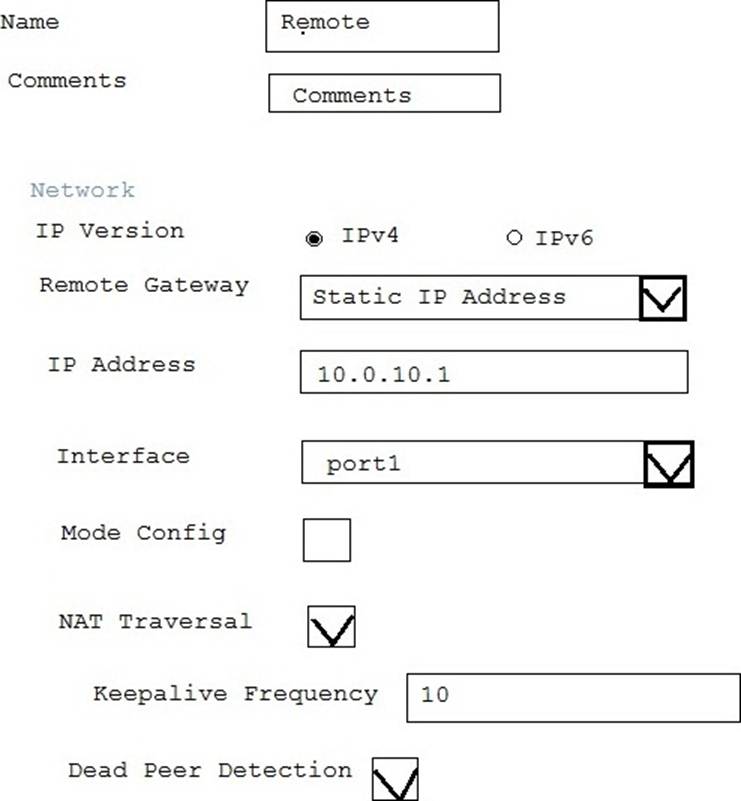
An administrator wants to monitor the VPN by enable the IKE real time debug using these commands:
diagnose vpn ike log-filter src-addr4 10.0.10.1
diagnose debug application ike -1
diagnose debug enable
The VPN is currently up, there is no traffic crossing the tunnel and DPD packets are being interchanged between both Ipsec gateways. However, the IKE rea time debug does NOT show any output.
Why isn’t there any output?
- A . The IKE real time debug shows the phases 1 and 2 negotiations only. It does not show any more output once the tunnel is up.
- B . The log-filter setting is set incorrectly. The VPN’s traffic does not match this filter.
- C . The IKF real time debug shows the phase 1 negotiation only. For information after that, the administrator must use the IPsec real time debug instead: diagnose debug application ipsec -1.
- D . The IKE real time debug shows error messages only. If it does not provide any output, it indicates that the tunnel is operating normally.
Which real time debug should an administrator enable to troubleshoot RADIUS authentication problems?
- A . Diagnose debug application radius -1.
- B . Diagnose debug application fnbamd -1.
- C . Diagnose authd console Clog enable.
- D . Diagnose radius console Clog enable.
An administrator has enabled HA session synchronization in a HA cluster with two members.
Which flag is added to a primary unit’s session to indicate that it has been synchronized to the secondary unit?
- A . redir.
- B . dirty.
- C . synced
- D . nds.
In which two ways does FortiManager function when it is deployed as a local FDS? (Choose two.)
- A . It provides VM license validation services.
- B . It supports rating requests from non-FortiGate devices.
- C . It caches available firmware updates for unmanaged devices.
- D . It can be configured as an update server, a rating server, or both.
Which statement about IKE and IKE NAT-T is true?
- A . IKE is used to encapsulate ESP traffic in some situations, and IKE NAT-T is used only when the local FortiGate is using NAT on the IPsec interface.
- B . IKE is the standard implementation for IKEv1 and IKE NAT-T is an extension added in IKEv2.
- C . They both use UDP as their transport protocol and the port number is configurable.
- D . They each use their own IP protocol number.
An administrator has configured two FortiGate devices for an HA cluster. While testing HA failover, the administrator notices that some of the switches in the network continue to send traffic to the former primary device.
What can the administrator do to fix this problem?
- A . Configure remote link monitoring to detect an issue in the forwarding path.
- B . Configure set send-garp-on-failover enable under config system ha on both cluster members.
- C . Verify that the speed and duplex settings match between the FortiGate interfaces and the connected switch ports.
- D . Configure set link-failed-signal enable under config system ha on both cluster members.
Which two statements about application layer test commands are true? (Choose two.)
- A . They are used to filter real-time debugs.
- B . They display real-time application debugs.
- C . Some of them can be used to restart an application.
- D . Some of them display statistics and configuration information about a feature or process.
Refer to the exhibit, which shows the output of a debug command.
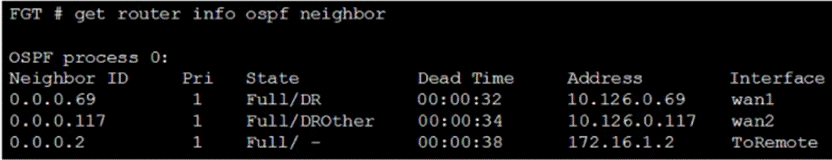
What can be concluded from the debug command output?
- A . The OSPF router with the ID 0.0.0.69 has its OSPF priority set to 0.
- B . The local FortiGate has a different MTU value from the OSPF router with ID 0.0.0.2, based on the state information.
- C . There are more than two OSPF routers on the wan2 network.
- D . The interface ToRemote is a broadcast OSPF network.
View the exhibit, which contains the output of a diagnose command, and then answer the question below.
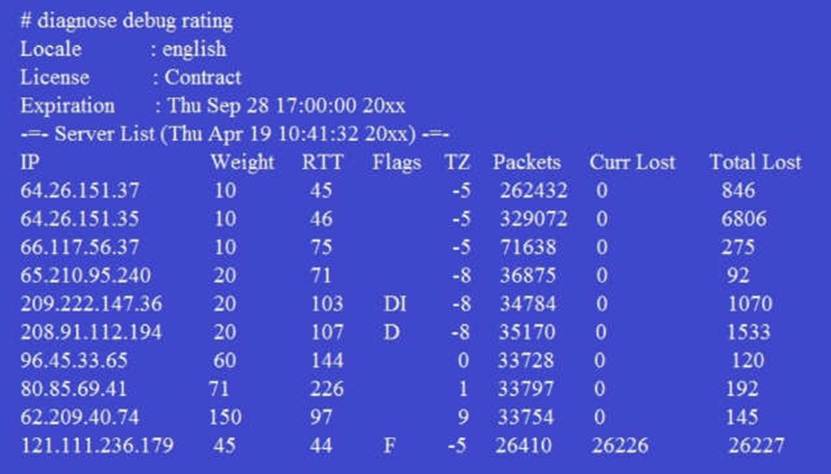
Which statements are true regarding the output in the exhibit? (Choose two.)
- A . FortiGate will probe 121.111.236.179 every fifteen minutes for a response.
- B . Servers with the D flag are considered to be down.
- C . Servers with a negative TZ value are experiencing a service outage.
- D . FortiGate used 209.222.147.36 as the initial server to validate its contract.