
Fortinet FCP_FGT_AD-7.4 Practice Exams
Last updated on Oct 22,2026- Exam Code: FCP_FGT_AD-7.4
- Exam Name: FCP - FortiGate 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Oct 22,2026
Which two VDOMs are the default VDOMs created when FortiGate is set up in split VDOM mode? (Choose two.)
- A . FG-traffic
- B . Mgmt
- C . FG-Mgmt
- D . Root
Which type of logs on FortiGate record information about traffic directly to and from the FortiGate management IP addresses?
- A . Local traffic logs
- B . Forward traffic logs
- C . System event logs
- D . Security logs
An administrator needs to inspect all web traffic (including Internet web traffic) coming from users connecting to the SSL-VPN.
How can this be achieved?
- A . Assigning public IP addresses to SSL-VPN users
- B . Configuring web bookmarks
- C . Disabling split tunneling
- D . Using web-only mode
Which statement best describes the role of a DC agent in an FSSO DC agent mode solution?
- A . It captures the login and logoff events and forwards them to the collector agent.
- B . It captures the login events and forwards them to the collector agent.
- C . It captures the login events and forwards them to FortiGate.
- D . It captures the user IP address and workstation name and forwards them to FortiGate.
Refer to the exhibit to view the application control profile.
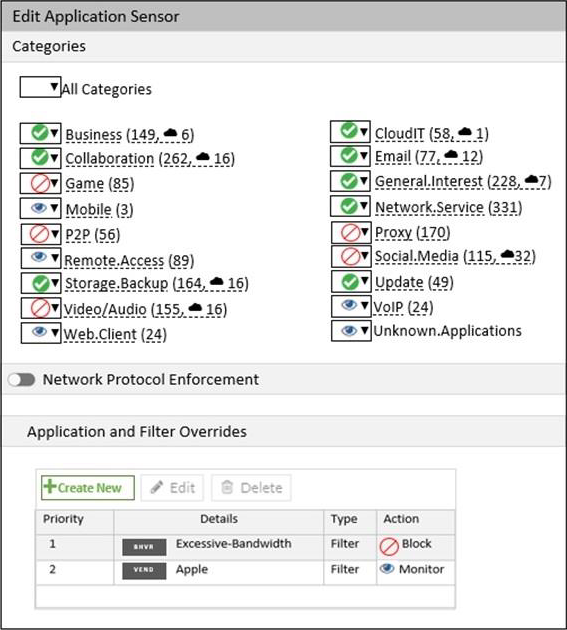
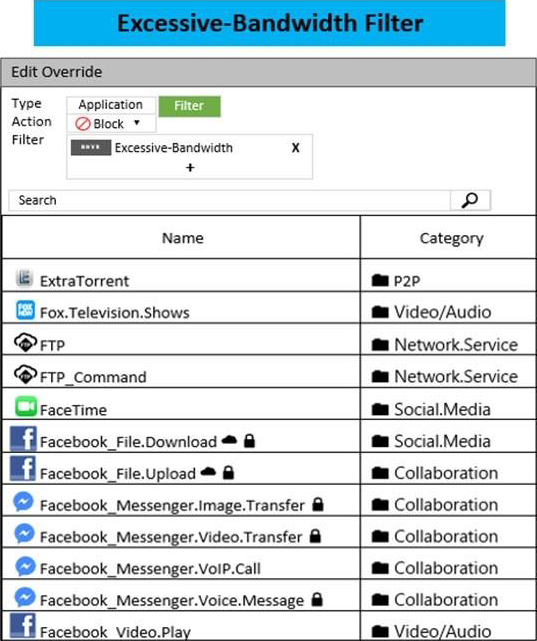
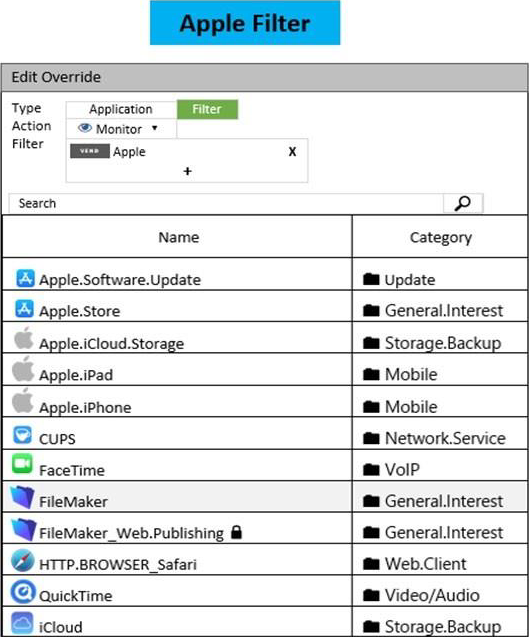
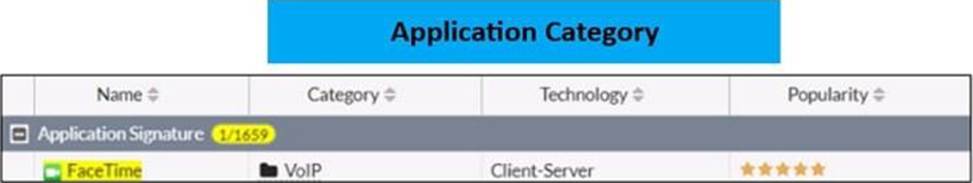
Based on the configuration, what will happen to Apple FaceTime?
- A . Apple FaceTime will be allowed, based on the Apple filter configuration.
- B . Apple FaceTime will be allowed, based on the Categories configuration.
- C . Apple FaceTime will be blocked, based on the Excessive-Bandwidth filter configuration.
- D . Apple FaceTime will be allowed only if the filter in Application and Filter Overrides is set to Learn.
FortiGate is configured as a policy-based next-generation firewall (NGFW) and is applying web filtering and application control directly on the security policy.
Which two other security profiles can you apply to the security policy? (Choose two.)
- A . Antivirus scanning
- B . File filter
- C . DNS filter
- D . Intrusion prevention
What is the limitation of using a URL list and application control on the same firewall policy, in NGFW policy-based mode?
- A . It limits the scanning of application traffic to the browser-based technology category only.
- B . It limits the scanning of application traffic to the DNS protocol only.
- C . It limits the scanning of application traffic to use parent signatures only.
- D . It limits the scanning of application traffic to the application category only.
View the exhibit.
date=2022-06-14 time=14:45:16 logid=0317013312 type=utm subtype=webfilter eventtype=ftgd_allow level=notice vd="root" policyid=2 identidx=1 sessionid=31232959 user="anonymous" group="ldap_users" srcip=192.168.1.24 srcport=63355 srcintf="port2" dstip=66.171.121.44 dstport=80 dstintf="port1" service="http" hostname="www.fortinet.com" profiletype="Webfilter_Profile" profile="default" status="passthrough" reqtype="direct" url="/" sentbyte=304 rcvdbyte=60135 msg="URL belongs to an allowed category in policy" method=domain class=0 cat=140 catdesc="custom1"
What two things does this raw log indicate? (Choose two.)
- A . FortiGate allowed the traffic to pass.
- B . 192.168.1.24 is the IP address for www.fortinet.com.
- C . The traffic matches the webfilter profile on firewall policy ID 2.
- D . The traffic originated from 66.171.121.44.
An administrator has configured a strict RPF check on FortiGate.
How does strict RPF check work?
- A . Strict RPF allows packets back to sources with all active routes.
- B . Strict RPF checks the best route back to the source using the incoming interface.
- C . Strict RPF checks only for the existence of at least one active route back to the source using the incoming interface.
- D . Strict RPF check is run on the first sent and reply packet of any new session.
Which two statements about antivirus scanning in a firewall policy set to proxy-based inspection mode, are true? (Choose two.)
- A . A file does not need to be buffered completely before it is moved to the antivirus engine for scanning.
- B . The client must wait for the antivirus scan to finish scanning before it receives the file.
- C . FortiGate sends a reset packet to the client if antivirus reports the file as infected.
- D . If a virus is detected, a block replacement message is displayed immediately.