
Fortinet FCP_FAZ_AD-7.4 Practice Exams
Last updated on Oct 22,2026- Exam Code: FCP_FAZ_AD-7.4
- Exam Name: FCP - FortiAnalyzer 7.4 Administrator
- Certification Provider: Fortinet
- Latest update: Oct 22,2026
Refer to the exhibit.
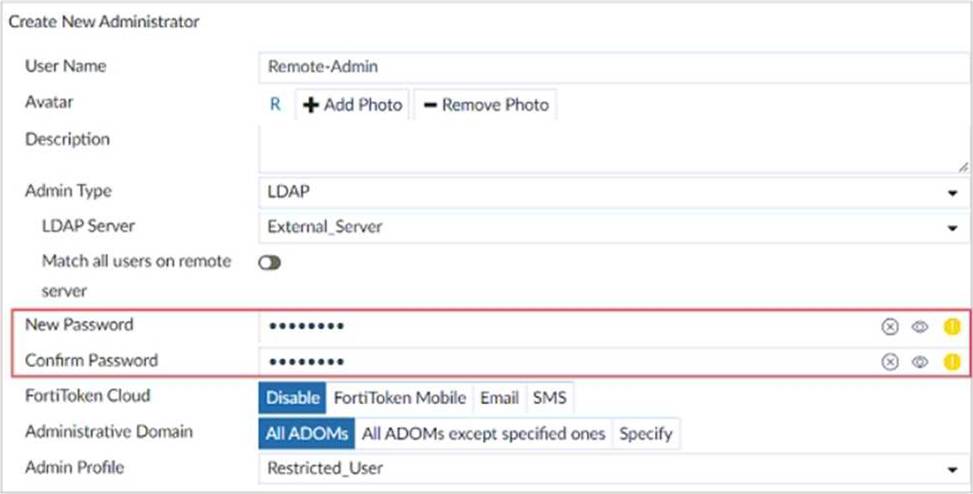
The exhibit shows the creation of a new administrator on FortiAnalyzer. The new account uses the credentials stored on an LDAP server.
Why would an administrator configure a password for this account?
- A . This password is used if the authentication server becomes unreachable.
- B . This password authenticates FortiAnalyzer aqainst the LDAP server.
- C . This password is set to comply with FortiAnalvzer password policy
- D . This password is required because this is a restricted user.
Which process is responsible for enforcing the log file size?
- A . oftpd
- B . miglogd
- C . sqlplugind
- D . logfiled
An administrator has configured the following settings:
config system global
set log-checksum md5-auth
end
What is the significance of executing this command?
- A . This command records the log file MD5 hash value.
- B . This command records passwords in log files and encrypts them.
- C . This command encrypts log transfer between FortiAnalyzer and other devices.
- D . This command records the log file MD5 hash value and authentication code.
After you have moved a registered logging device out of one ADOM and into a new ADOM, what is the purpose of running the following CLI command?
execute sql-local rebuild-adom <new-ADOM-name>
- A . To reset the disk quota enforcement to default
- B . To remove the analytics logs of the device from the old database
- C . To migrate the archive logs to the new ADOM
- D . To populate the new ADOM with analytical logs for the moved device, so you can run reports

View the exhibit:
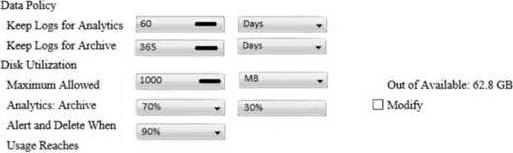
What does the 1000MB maximum for disk utilization refer to?
- A . The disk quota for the FortiAnalyzer model
- B . The disk quota for all devices in the ADOM
- C . The disk quota for each device in the ADOM
- D . The disk quota for the ADOM type
FortiAnalyzer reports are dropping analytical data from 15 days ago, even though the data policy setting for analytics logs is 60 days.
What is the most likely problem?
- A . Quota enforcement is acting on analytical data before a report is complete
- B . Logs are rolling before the report is run
- C . CPU resources are too high
- D . Disk utilization for archive logs is set for 15 days
You finished registering a FortiGate device. After traffic starts to flow through FortiGate, you notice that only some of the logs expected are being received on FortiAnalyzer.
What could be the reason for the logs not arriving on FortiAnalyzer?
- A . FortiGate was added to the wrong ADOM type.
- B . This FortiGate model is not fully supported.
- C . FortiGate does not have logging configured correctly.
- D . This FortiGate is part of an HA cluster but it is the secondary device.