
EC-Council 312-50v13 Practice Exams
Last updated on Oct 23,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 23,2026
Which of the following tactics uses malicious code to redirect users’ web traffic?
- A . Spimming
- B . Pharming
- C . Phishing
- D . Spear-phishing
what is the port to block first in case you are suspicious that an loT device has been compromised?
- A . 22
- B . 443
- C . 48101
- D . 80
what is the port to block first in case you are suspicious that an loT device has been compromised?
- A . 22
- B . 443
- C . 48101
- D . 80
While performing a security audit of a web application, an ethical hacker discovers a potential vulnerability.
The application responds to logically incorrect queries with detailed error messages that divulge the underlying database’s structure. The ethical hacker decides to exploit this vulnerability further.
Which type of SQL Injection attack is the ethical hacker likely to use?
- A . UNION SQL Injection
- B . Blind/inferential SQL Injection
- C . In-band SQL Injection
- D . Error-based SOL Injection
Which type of sniffing technique is generally referred as MiTM attack?
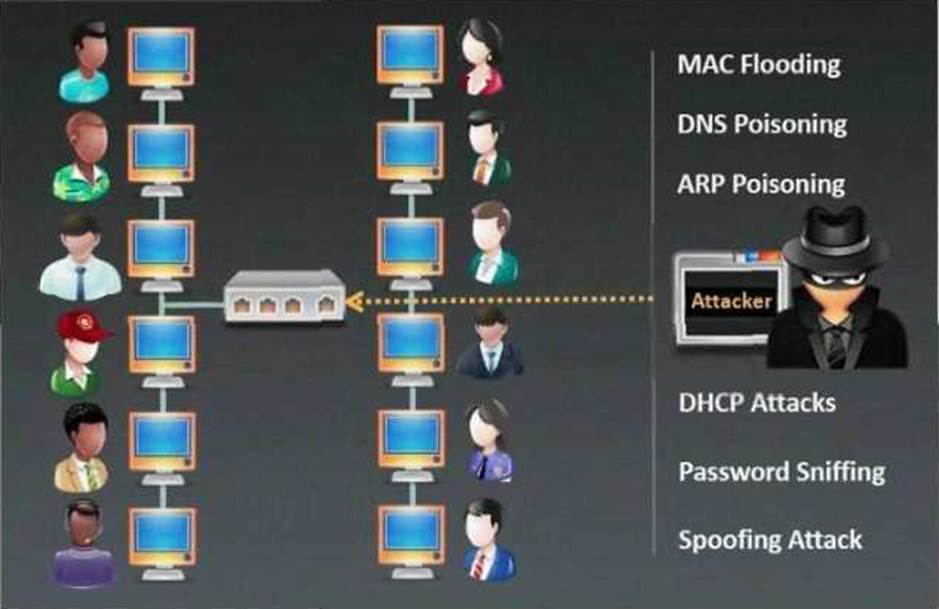
- A . Password Sniffing
- B . ARP Poisoning
- C . Mac Flooding
- D . DHCP Sniffing
A cyber attacker has initiated a series of activities against a high-profile organization following the Cyber Kill Chain Methodology. The attacker is presently in the “Delivery” stage. As an Ethical Hacker, you are trying to anticipate the adversary’s next move.
What is the most probable subsequent action from the attacker based on the Cyber Kill Chain Methodology?
- A . The attacker will attempt to escalate privileges to gain complete control of the compromised system.
- B . The attacker will exploit the malicious payload delivered to the target organization and establish a foothold.
- C . The attacker will initiate an active connection to the target system to gather more data.
- D . The attacker will start reconnaissance to gather as much information as possible about the target.
A DDOS attack is performed at layer 7 to take down web infrastructure. Partial HTTP requests are sent to the web infrastructure or applications. Upon receiving a partial request, the target servers opens multiple connections and keeps waiting for the requests to complete.
Which attack is being described here?
- A . Desynchronization
- B . Slowloris attack
- C . Session splicing
- D . Phlashing
To create a botnet. the attacker can use several techniques to scan vulnerable machines. The attacker first collects Information about a large number of vulnerable machines to create a list. Subsequently, they infect the machines. The list Is divided by assigning half of the list to the newly compromised machines. The scanning process runs simultaneously. This technique ensures the spreading and installation of malicious code in little time.
Which technique is discussed here?
- A . Hit-list-scanning technique
- B . Topological scanning technique
- C . Subnet scanning technique
- D . Permutation scanning technique
Peter, a system administrator working at a reputed IT firm, decided to work from his home and login remotely. Later, he anticipated that the remote connection could be exposed to session hijacking. To curb this possibility, he implemented a technique that creates a safe and encrypted tunnel over a public network to securely send and receive sensitive information and prevent hackers from decrypting the data flow between the endpoints.
What is the technique followed by Peter to send files securely through a remote connection?
- A . DMZ
- B . SMB signing
- C . VPN
- D . Switch network