
EC-Council 312-50v13 Practice Exams
Last updated on Oct 22,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 22,2026
Miley, a professional hacker, decided to attack a target organization’s network. To perform the attack, she used a tool to send fake ARP messages over the target network to link her MAC address with the target system’s IP address. By performing this, Miley received messages directed to the victim’s MAC address and further used the tool to intercept, steal, modify, and block sensitive communication to the target system.
What is the tool employed by Miley to perform the above attack?
- A . Gobbler
- B . KDerpNSpoof
- C . BetterCAP
- D . Wireshark
SQL injection (SQLi) attacks attempt to inject SQL syntax into web requests, which may Bypass authentication and allow attackers to access and/or modify data attached to a web application.
Which of the following SQLI types leverages a database server’s ability to make DNS requests to pass data to an attacker?
- A . Union-based SQLI
- B . Out-of-band SQLI
- C . ln-band SQLI
- D . Time-based blind SQLI
A large e-commerce organization is planning to implement a vulnerability assessment solution to enhance its security posture. They require a solution that imitates the outside view of attackers, performs well-organized inference-based testing, scans automatically against continuously updated databases, and supports multiple networks.
Given these requirements, which type of vulnerability assessment solution would be most appropriate?
- A . Inference-based assessment solution
- B . Service-based solution offered by an auditing firm
- C . Tree-based assessment approach
- D . Product-based solution installed on a private network
_________ is a type of phishing that targets high-profile executives such as CEOs, CFOs, politicians, and celebrities who have access to confidential and highly valuable information.
- A . Spear phishing
- B . Whaling
- C . Vishing
- D . Phishing
After an audit, the auditors Inform you that there is a critical finding that you must tackle Immediately. You read the audit report, and the problem is the service running on port 389.
Which service Is this and how can you tackle the problem?
- A . The service is LDAP. and you must change it to 636. which is LDPAPS.
- B . The service is NTP. and you have to change It from UDP to TCP in order to encrypt it
- C . The findings do not require immediate actions and are only suggestions.
- D . The service is SMTP, and you must change it to SMIME. which is an encrypted way to send emails.
A computer science student needs to fill some information into a secured Adobe PDF job application that was received from a prospective employer. Instead of requesting a new document that allowed the forms to be completed, the student decides to write a script that pulls passwords from a list of commonly used passwords to try against the secured PDF until the correct password is found or the list is exhausted.
Which cryptography attack is the student attempting?
- A . Man-in-the-middle attack
- B . Brute-force attack
- C . Dictionary attack
- D . Session hijacking
Mason, a professional hacker, targets an organization and spreads Emotet malware through malicious script. After infecting the victim’s device. Mason further used Emotet to spread the infection across local networks and beyond to compromise as many machines as possible. In this process, he used a tool, which is a self-extracting RAR file, to retrieve information related to network resources such as writable share drives.
What is the tool employed by Mason in the above scenario?
- A . NetPass.exe
- B . Outlook scraper
- C . WebBrowserPassView
- D . Credential enumerator
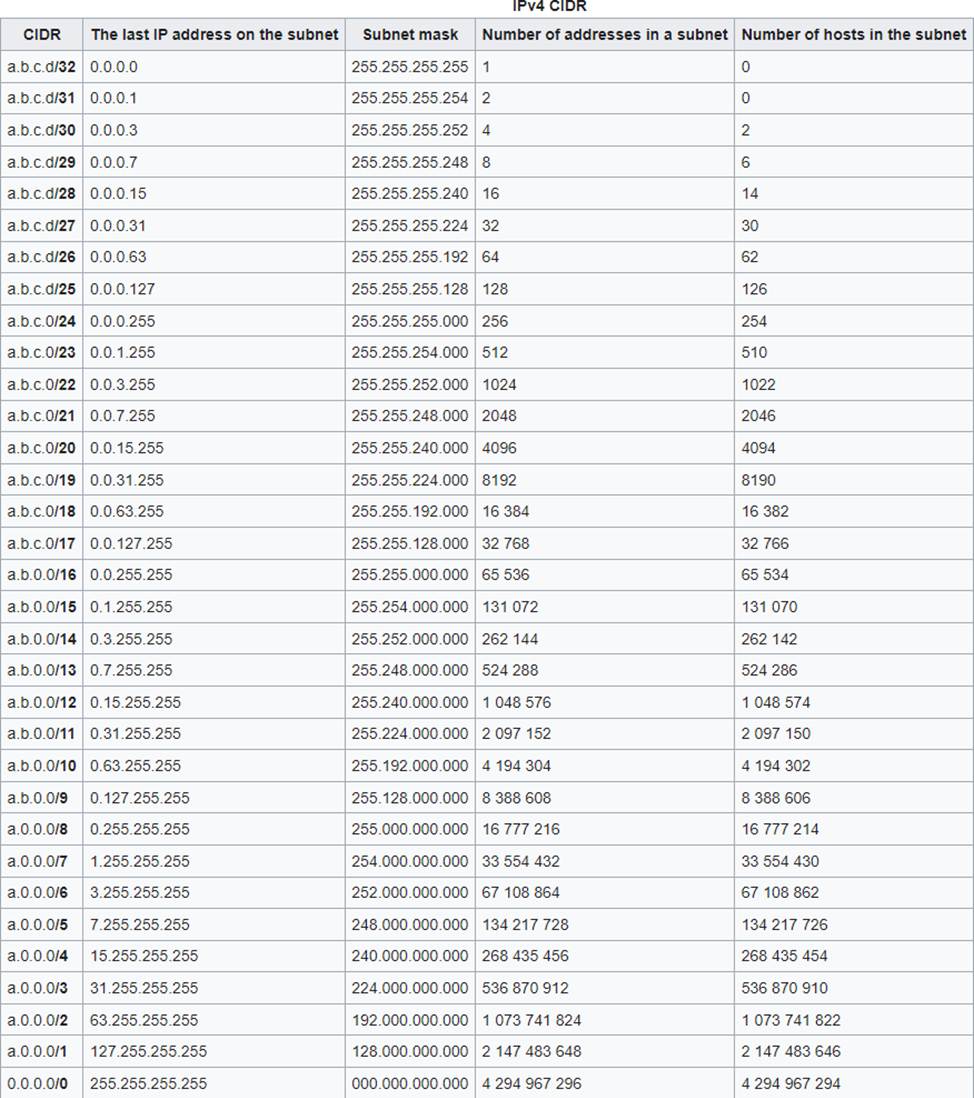
The network in ABC company is using the network address 192.168.1.64 with mask 255.255.255.192. In the network the servers are in the addresses 192.168.1.122, 192.168.1.123 and 192.168.1.124. An attacker is trying to find those servers but he cannot see them in his scanning. The command he is using is: nmap 192.168.1.64/28.
Why he cannot see the servers?
- A . He needs to add the command ““ip address”” just before the IP address
- B . He needs to change the address to 192.168.1.0 with the same mask
- C . He is scanning from 192.168.1.64 to 192.168.1.78 because of the mask /28 and the servers are not in that range
- D . The network must be dawn and the nmap command and IP address are ok
Sophia is a shopping enthusiast who spends significant time searching for trendy outfits online. Clark, an attacker, noticed her activities several times and sent a fake email containing a deceptive page link to her social media page displaying all-new and trendy outfits. In excitement, Sophia clicked on the malicious link and logged in to that page using her valid credentials.
Which of the following tools is employed by Clark to create the spoofed email?
- A . PyLoris
- B . Slowloris
- C . Evilginx
- D . PLCinject
which of the following protocols can be used to secure an LDAP service against anonymous queries?
- A . SSO
- B . RADIUS
- C . WPA
- D . NTLM