EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
When you are testing a web application, it is very useful to employ a proxy tool to save every request and response. You can manually test every request and analyze the response to find vulnerabilities. You can test parameter and headers manually to get more precise results than if using web vulnerability scanners.
What proxy tool will help you find web vulnerabilities?
- A . Maskgen
- B . Dimitry
- C . Burpsuite
- D . Proxychains
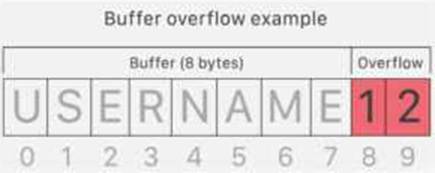
John is investigating web-application firewall logs and observers that someone is attempting to inject the following:
char buff[10];
buff[>o] – ‘a’:
What type of attack is this?
- A . CSRF
- B . XSS
- C . Buffer overflow
- D . SQL injection
During a black-box pen test you attempt to pass IRC traffic over port 80/TCP from a compromised web enabled host. The traffic gets blocked; however, outbound HTTP traffic is unimpeded.
What type of firewall is inspecting outbound traffic?
- A . Circuit
- B . Stateful
- C . Application
- D . Packet Filtering
What is one of the advantages of using both symmetric and asymmetric cryptography in SSL/TLS?
- A . Supporting both types of algorithms allows less-powerful devices such as mobile phones to use symmetric encryption instead.
- B . Symmetric algorithms such as AES provide a failsafe when asymmetric methods fail.
- C . Symmetric encryption allows the server to security transmit the session keys out-of-band.
- D . Asymmetric cryptography is computationally expensive in comparison. However, it is well-suited to securely negotiate keys for use with symmetric cryptography.
Which of the following is the BEST way to defend against network sniffing?
- A . Using encryption protocols to secure network communications
- B . Register all machines MAC Address in a Centralized Database
- C . Use Static IP Address
- D . Restrict Physical Access to Server Rooms hosting Critical Servers
Bob, your senior colleague, has sent you a mail regarding a deal with one of the clients. You are requested to accept the offer and you oblige. After 2 days. Bob denies that he had ever sent a mail.
What do you want to ""know"" to prove yourself that it was Bob who had send a mail?
- A . Authentication
- B . Confidentiality
- C . Integrity
- D . Non-Repudiation
You went to great lengths to install all the necessary technologies to prevent hacking attacks, such as expensive firewalls, antivirus software, anti-spam systems and intrusion detection/prevention tools in your company’s network. You have configured the most secure policies and tightened every device on your network. You are confident that hackers will never be able to gain access to your network with complex security system in place.
Your peer, Peter Smith who works at the same department disagrees with you.
He says even the best network security technologies cannot prevent hackers gaining access to the network because of presence of "weakest link" in the security chain.
What is Peter Smith talking about?
- A . Untrained staff or ignorant computer users who inadvertently become the weakest link in your security chain
- B . "zero-day" exploits are the weakest link in the security chain since the IDS will not be able to detect these attacks
- C . "Polymorphic viruses" are the weakest link in the security chain since the Anti-Virus scanners will not be able to detect these attacks
- D . Continuous Spam e-mails cannot be blocked by your security system since spammers use different techniques to bypass the filters in your gateway
A Certified Ethical Hacker (CEH) is given the task to perform an LDAP enumeration on a target system. The system is secured and accepts connections only on secure LDAP. The CEH uses Python for the enumeration process. After successfully installing LDAP and establishing a connection with the target, he attempts to fetch details like the domain name and naming context but is unable to receive the expected response.
Considering the circumstances, which of the following is the most plausible reason for this situation?
- A . The Python version installed on the CEH’s machine is incompatible with the Idap3 library
- B . The secure LDAP connection was not properly initialized due to a lack of ‘use_ssl = True’ in the server object creation
- C . The enumeration process was blocked by the target system’s intrusion detection system
- D . The system failed to establish a connection due to an incorrect port number
Robin, an attacker, is attempting to bypass the firewalls of an organization through the DNS tunneling method in order to exfiltrate data. He is using the NSTX tool for bypassing the firewalls.
On which of the following ports should Robin run the NSTX tool?
- A . Port 53
- B . Port 23
- C . Port 50
- D . Port 80