
EC-Council 312-50v13 Practice Exams
Last updated on Oct 24,2026- Exam Code: 312-50v13
- Exam Name: Certified Ethical Hacker Exam (CEHv13)
- Certification Provider: EC-Council
- Latest update: Oct 24,2026
During a penetration testing assignment, a Certified Ethical Hacker (CEH) used a set of scanning tools to create a profile of the target organization. The CEH wanted to scan for live hosts, open ports, and services on a target network. He used Nmap for network inventory and Hping3 for network security auditing. However, he wanted to spoof IP addresses for anonymity during probing.
Which command should the CEH use to perform this task?
- A . Hping3 -110.0.0.25 –ICMP
- B . Nmap -sS -Pn -n -vw –packet-trace -p- –script discovery -T4
- C . Hping3 -S 192.168.1.1 -a 192.168.1.254 -p 22 -flood
- D . Hping3-210.0.0.25-p 80
You need to deploy a new web-based software package for your organization. The package requires three separate servers and needs to be available on the Internet.
What is the recommended architecture in terms of server placement?
- A . All three servers need to be placed internally
- B . A web server facing the Internet, an application server on the internal network, a database server on the internal network
- C . A web server and the database server facing the Internet, an application server on the internal network
- D . All three servers need to face the Internet so that they can communicate between themselves
You are the lead cybersecurity analyst at a multinational corporation that uses a hybrid encryption system to secure inter-departmental communications. The system uses RSA encryption for key exchange and AES for data encryption, taking advantage of the strengths of both asymmetric and symmetric encryption. Each RSA
key pair has a size of ‘n’ bits, with larger keys providing more security at the cost of slower performance. The time complexity of generating an RSA key pair is O(n*2), and AES encryption has a time complexity of O(n). An attacker has developed a quantum algorithm with time complexity O((log n)*2) to crack RSA encryption.
Given *n=4000′ and variable ‘AES key size’, which scenario is likely to provide the best balance of security and performance?
- A . AES key size=128 bits: This configuration provides less security than option A, but RSA key generation and AES encryption will be faster.
- B . AES key size=256 bits: This configuration provides a high level of security, but RSA key generation may be slow.
- C . AES key size=192 bits: This configuration is a balance between options A and B, providing moderate security and performance.
- D . AES key size=512 bits: This configuration provides the highest level of security but at a significant performance cost due to the large AES key size.
Daniel Is a professional hacker who Is attempting to perform an SQL injection attack on a target website. www.movlescope.com. During this process, he encountered an IDS that detects SQL Injection attempts based on predefined signatures. To evade any comparison statement, he attempted placing characters such as ‘’or ‘1’=’1" In any bask injection statement such as "or 1=1." Identify the evasion technique used by Daniel in the above scenario.
- A . Null byte
- B . IP fragmentation
- C . Char encoding
- D . Variation
in an attempt to increase the security of your network, you Implement a solution that will help keep your wireless network undiscoverable and accessible only to those that know It.
How do you accomplish this?
- A . Delete the wireless network
- B . Remove all passwords
- C . Lock all users
- D . Disable SSID broadcasting
An ethical hacker is testing the security of a website’s database system against SQL Injection attacks. They discover that the IDS has a strong signature detection mechanism to detect typical SQL injection patterns.
Which evasion technique can be most effectively used to bypass the IDS signature detection while performing a SQL Injection attack?
- A . Implement case variation by altering the case of SQL statements
- B . Employ IP fragmentation to obscure the attack payload
- C . Use Hex encoding to represent the SQL query string
- D . Leverage string concatenation to break identifiable keywords
Heather’s company has decided to use a new customer relationship management tool. After performing the appropriate research, they decided to purchase a subscription to a cloud-hosted solution. The only administrative task that Heather will need to perform is the management of user accounts. The provider will take care of the hardware, operating system, and software administration including patching and monitoring.
Which of the following is this type of solution?
- A . SaaS
- B . IaaS
- C . CaaS
- D . PasS
Which of the following incident handling process phases is responsible for defining rules, collaborating human workforce, creating a back-up plan, and testing the plans for an organization?
- A . Preparation phase
- B . Containment phase
- C . Identification phase
- D . Recovery phase
An attacker with access to the inside network of a small company launches a successful STP manipulation attack.
What will he do next?
- A . He will create a SPAN entry on the spoofed root bridge and redirect traffic to his computer.
- B . He will activate OSPF on the spoofed root bridge.
- C . He will repeat this action so that it escalates to a DoS attack.
- D . He will repeat the same attack against all L2 switches of the network.
ViruXine.W32 virus hides their presence by changing the underlying executable code.
This Virus code mutates while keeping the original algorithm intact, the code changes itself each time it runs, but the function of the code (its semantics) will not change at all.
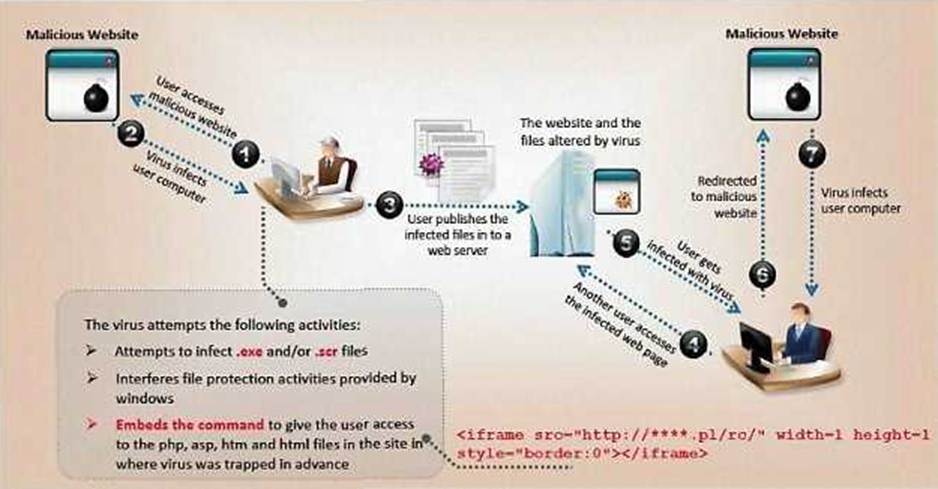
Here is a section of the Virus code:
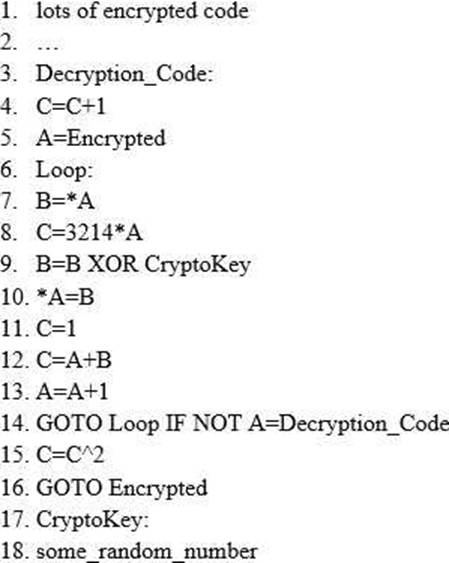
What is this technique called?
- A . Polymorphic Virus
- B . Metamorphic Virus
- C . Dravidic Virus
- D . Stealth Virus