
CyberArk CPC-SEN Practice Exams
Last updated on Oct 22,2026- Exam Code: CPC-SEN
- Exam Name: CyberArk Sentry - Privilege Cloud
- Certification Provider: CyberArk
- Latest update: Oct 22,2026
You are implementing LDAPS Integration for a standard Privilege Cloud environment.
Which information must be provided to the CyberArk Privilege Cloud support team through a Service Request? (Choose 2.)
- A . LDAPS certificate chain for all domain controllers to be integrated
- B . LDAP bind username and password used to authenticate to the directory to be integrated
C Domain Base Context used to locate the users and groups in the Active Directory to be integrated - C . Fully Qualified Domain Name and IP Address of the domain controllers to be integrated
- D . remote port set during secure tunnel configuration for each domain controller to be integrated
Following the installation of the PSM for SSH server, which additional tasks should be performed? (Choose 2.)
- A . Delete the user.cred file used during installation.
- B . Delete the vault.ini you used during installation.
- C . Delete the psmpparms file you used during installation.
- D . Package all installation log files for upload to CyberArk.
In the directory lookup order, which directory service is always looked up first for the CyberArk Privilege Cloud solution?
- A . Active Directory
- B . LDAP
- C . Federated Directory
- D . CyberArk Cloud Directory
In the directory lookup order, which directory service is always looked up first for the CyberArk Privilege Cloud solution?
- A . Active Directory
- B . LDAP
- C . Federated Directory
- D . CyberArk Cloud Directory
Which statement best describes a PSM server’s network requirements?
- A . It must reach the target system using its native protocols.
- B . It requires limited outbound connectivity to Ports 1858 and 443 only.
- C . It requires direct access to the internet.
- D . It requires broad inbound firewall rules and outbound traffic should be limited to Port 1858.
After correctly configuring reconciliation parameters in the Prod-AIX-Root-Accounts Platform, this error message appears in the CPM log: CACPM410E Ending password policy Prod-AIX-Root-Accounts since the reconciliation task is active but the AllowedSafes parameter was not updated.
What caused this situation?
- A . The reconciliation account defined in the Platform is in a locked state and is not accessible.
- B . The CPM is currently configured to use to an unsigned engine.
- C . The AllowedSafes parameter does not include the safe containing the reconciliation account defined in the Platform.
- D . A second CPM is incorrectly configured to manage the reconciliation account’s safe which is causing a deadlock situation between the two CPMs.
To disable the PSM default Support for Browser Sessions, which option should be set to ‘No* before running Hardening?
- A . SupportWebApplications
- B . SupportBrowsers
- C . SupportWebBrowsers
- D . SupportHTML5Content
What is the recommended method to enable load balancing and failover of the CyberArk Identity Connector?
- A . Setup IIS based Application Request Routing on two or more CyberArk Identity Connector servers.
- B . Set up a network load balancer between two or more CyberArk Identity Connector servers.
- C . Set up two or more CyberArk Identity Connector servers only.
- D . Set up a Microsoft Failover Cluster on two or more CyberArk Identity Connector servers.
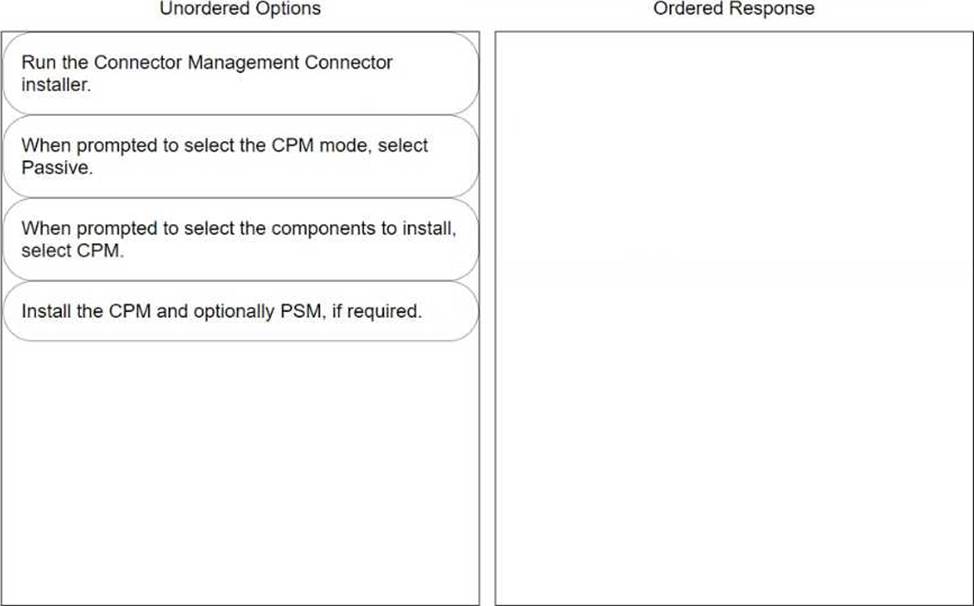
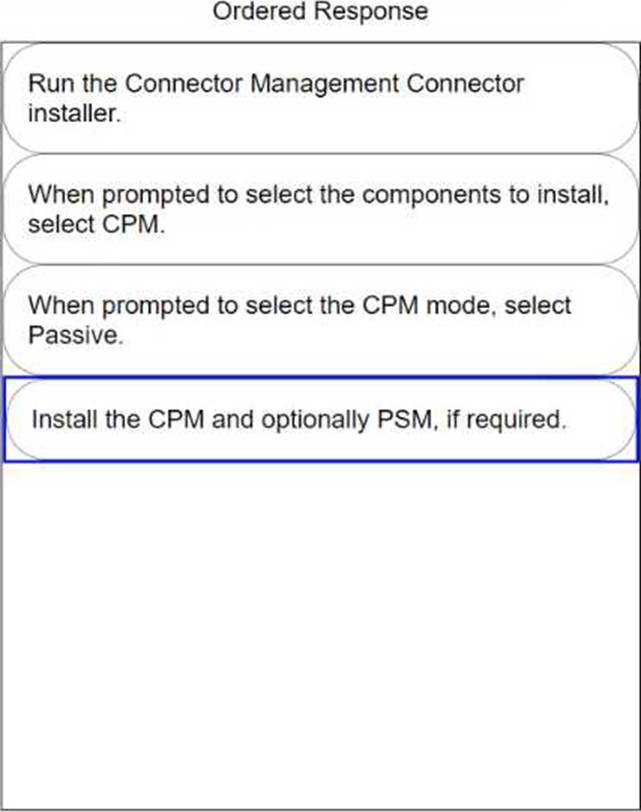
DRAG DROP
Arrange the steps to install passive CPM using Connector Management in the correct sequence
Which statement is correct about using the AllowedSafes platform parameter?
- A . It allows users to access accounts in specific safes.
- B . It prevents the CPM from scanning all safes, restricting it to scan only safes that match the AllowedSafes configuration.
- C . It allows the CPM to access PSM safes to monitor platform configuration and connection component changes.
- D . It prevents the CPM from processing pending items in the Discovery safes enforcing manual intervention to complete the onboarding process.