
CompTIA SY0-701 Practice Exams
Last updated on Oct 22,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Oct 22,2026
An organization wants a third-party vendor to do a penetration test that targets a specific device. The organization has provided basic information about the device.
Which of the following best describes this kind of penetration test?
- A . Partially known environment
- B . Unknown environment
- C . Integrated
- D . Known environment
An administrator is reviewing a single server’s security logs and discovers the following;
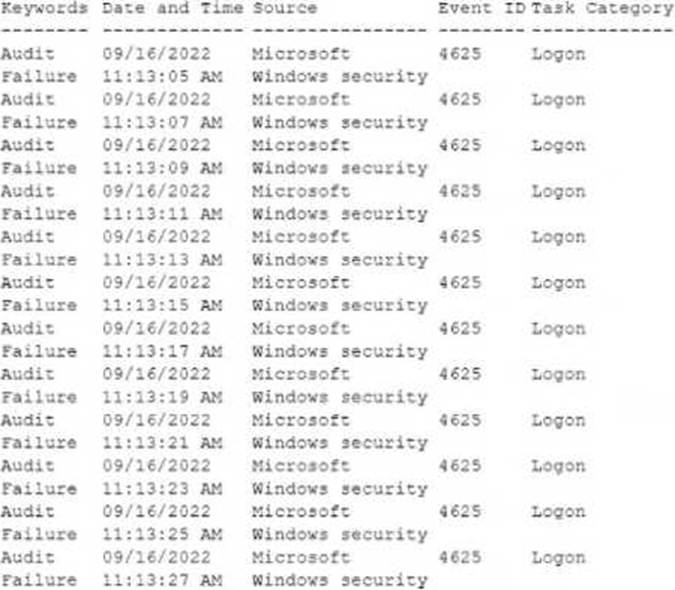
Which of the following best describes the action captured in this log file?
- A . Brute-force attack
- B . Privilege escalation
- C . Failed password audit
- D . Forgotten password by the user
The marketing department set up its own project management software without telling the appropriate departments.
Which of the following describes this scenario?
- A . Shadow IT
- B . Insider threat
- C . Data exfiltration
- D . Service disruption
A U.S.-based cloud-hosting provider wants to expand its data centers to new international locations.
Which of the following should the hosting provider consider first?
- A . Local data protection regulations
- B . Risks from hackers residing in other countries
- C . Impacts to existing contractual obligations
- D . Time zone differences in log correlation
A security professional discovers a folder containing an employee’s personal information on the enterprise’s shared drive.
Which of the following best describes the data type the security professional should use to identify organizational policies and standards concerning the storage of employees’ personal information?
- A . Legal
- B . Financial
- C . Privacy
- D . Intellectual property
An administrator has identified and fingerprinted specific files that will generate an alert if an attempt is made to email these files outside of the organization.
Which of the following best describes the tool the administrator is using?
- A . DLP
- B . SNMP traps
- C . SCAP
- D . IPS
A security analyst reviews domain activity logs and notices the following:
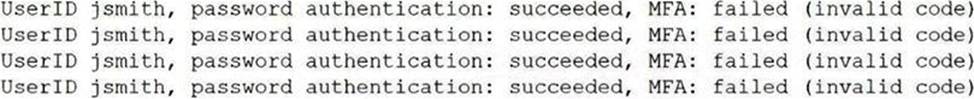
Which of the following is the best explanation for what the security analyst has discovered?
- A . The user jsmith’s account has been locked out.
- B . A keylogger is installed on [smith’s workstation
- C . An attacker is attempting to brute force ismith’s account.
- D . Ransomware has been deployed in the domain.
Which of the following would be the best way to test resiliency in the event of a primary power failure?
- A . Parallel processing
- B . Tabletop exercise
- C . Simulation testing
- D . Production failover
Which of the following is the primary purpose of a service that tracks log-ins and time spent using the service?
- A . Availability
- B . Accounting
- C . Authentication
- D . Authorization
A security engineer is installing an IPS to block signature-based attacks in the environment.
Which of the following modes will best accomplish this task?
- A . Monitor
- B . Sensor
- C . Audit
- D . Active