
CompTIA SY0-701 Practice Exams
Last updated on Oct 22,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Oct 22,2026
Which of the following phases of an incident response involves generating reports?
- A . Recovery
- B . Preparation
- C . Lessons learned
- D . Containment
Which of the following would help ensure a security analyst is able to accurately measure the overall risk to an organization when a new vulnerability is disclosed?
- A . A full inventory of all hardware and software
- B . Documentation of system classifications
- C . A list of system owners and their departments
- D . Third-party risk assessment documentation
Which of the following vulnerabilities is associated with installing software outside of a manufacturer’s approved software repository?
- A . Jailbreaking
- B . Memory injection
- C . Resource reuse
- D . Side loading
Which of the following vulnerabilities is associated with installing software outside of a manufacturer’s approved software repository?
- A . Jailbreaking
- B . Memory injection
- C . Resource reuse
- D . Side loading
A vendor needs to remotely and securely transfer files from one server to another using the command line.
Which of the following protocols should be Implemented to allow for this type of access? (Select two).
- A . SSH
- B . SNMP
- C . RDP
- D . S/MIME
- E . SMTP
- F . SFTP
Which of the following would best explain why a security analyst is running daily vulnerability scans on all corporate endpoints?
- A . To track the status of patching installations
- B . To find shadow IT cloud deployments
- C . To continuously the monitor hardware inventory
- D . To hunt for active attackers in the network
An organization is struggling with scaling issues on its VPN concentrator and internet circuit due to remote work. The organization is looking for a software solution that will allow it to reduce traffic on the VPN and internet circuit, while still providing encrypted tunnel access to the data center and monitoring of remote employee internet traffic.
Which of the following will help achieve these objectives?
- A . Deploying a SASE solution to remote employees
- B . Building a load-balanced VPN solution with redundant internet
- C . Purchasing a low-cost SD-WAN solution for VPN traffic
- D . Using a cloud provider to create additional VPN concentrators
Which of the following best describe why a process would require a two-person integrity security control?
- A . To Increase the chance that the activity will be completed in half of the time the process would take only one user to complete
- B . To permit two users from another department to observe the activity that is being performed by an authorized user
- C . To reduce the risk that the procedures are performed incorrectly or by an unauthorized user
- D . To allow one person to perform the activity while being recorded on the CCTV camera
During a recent company safety stand-down, the cyber-awareness team gave a presentation on the importance of cyber hygiene. One topic the team covered was best practices for printing centers.
Which of the following describes an attack method that relates to printing centers?
- A . Whaling
- B . Credential harvesting
- C . Prepending
- D . Dumpster diving
A security analyst finds a rogue device during a monthly audit of current endpoint assets that are connected to the network. The corporate network utilizes 002.1X for access control. To be allowed on the network, a device must have a Known hardware address, and a valid user name and password must be entered in a captive portal.
The following is the audit report:
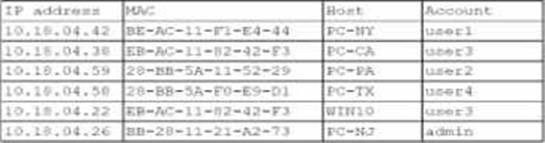
Which of the following is the most likely way a rogue device was allowed to connect?
- A . A user performed a MAC cloning attack with a personal device.
- B . A DMCP failure caused an incorrect IP address to be distributed
- C . An administrator bypassed the security controls for testing.
- D . DNS hijacking let an attacker intercept the captive portal traffic.