
CompTIA SY0-701 Practice Exams
Last updated on Oct 22,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Oct 22,2026
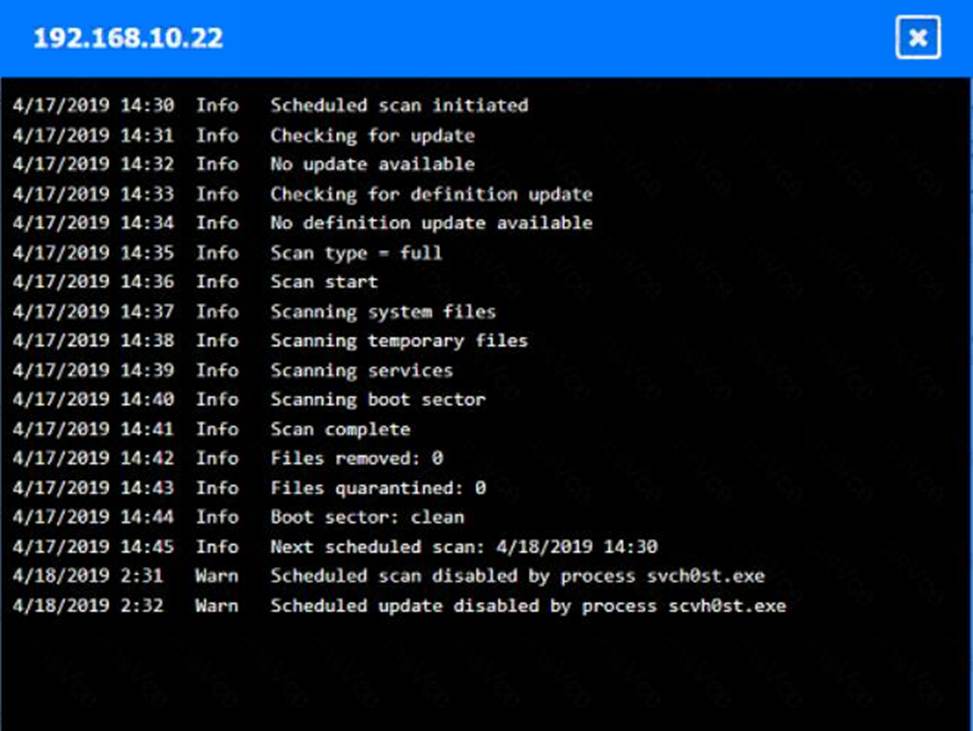
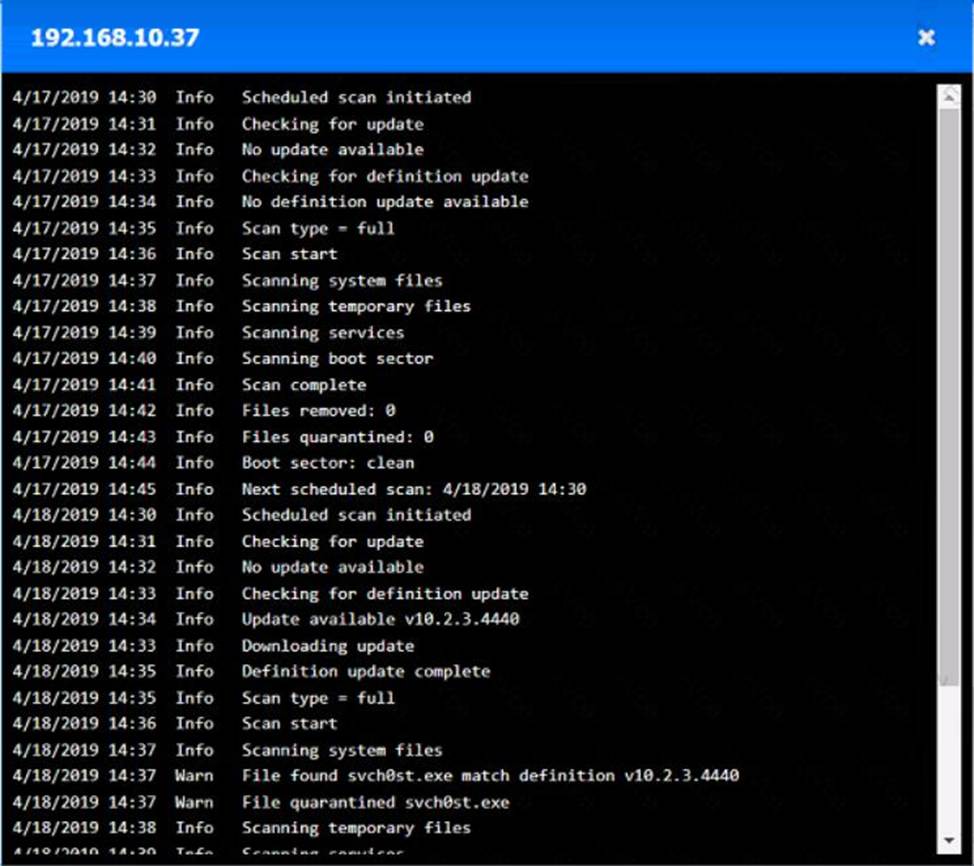
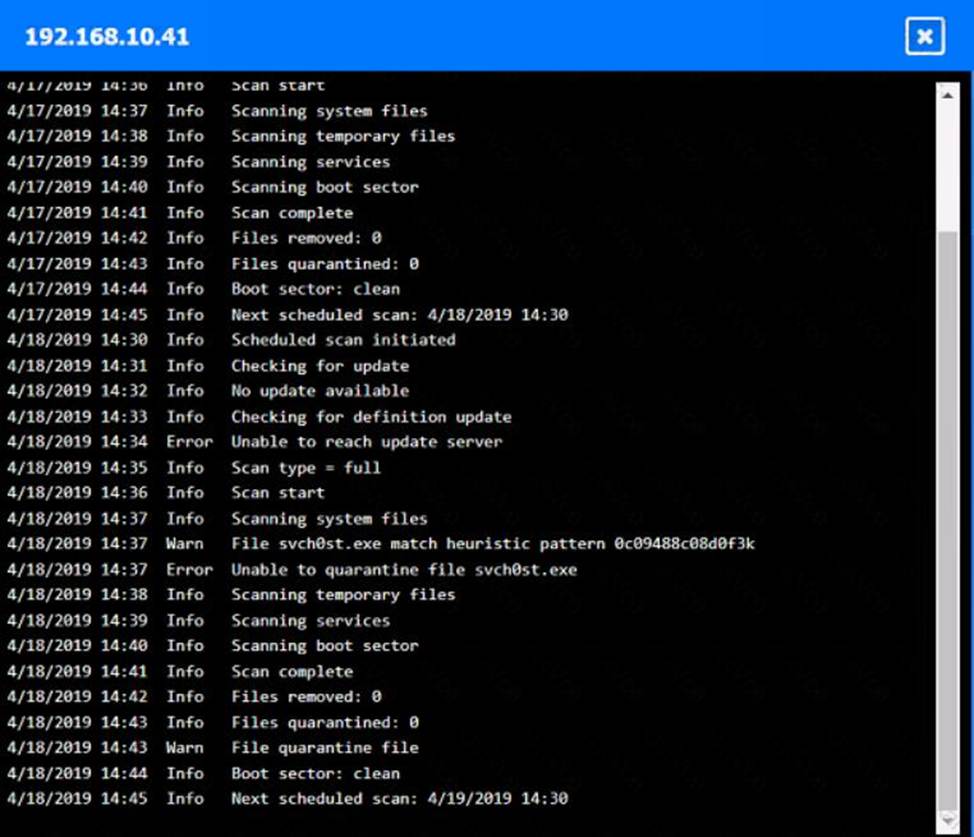
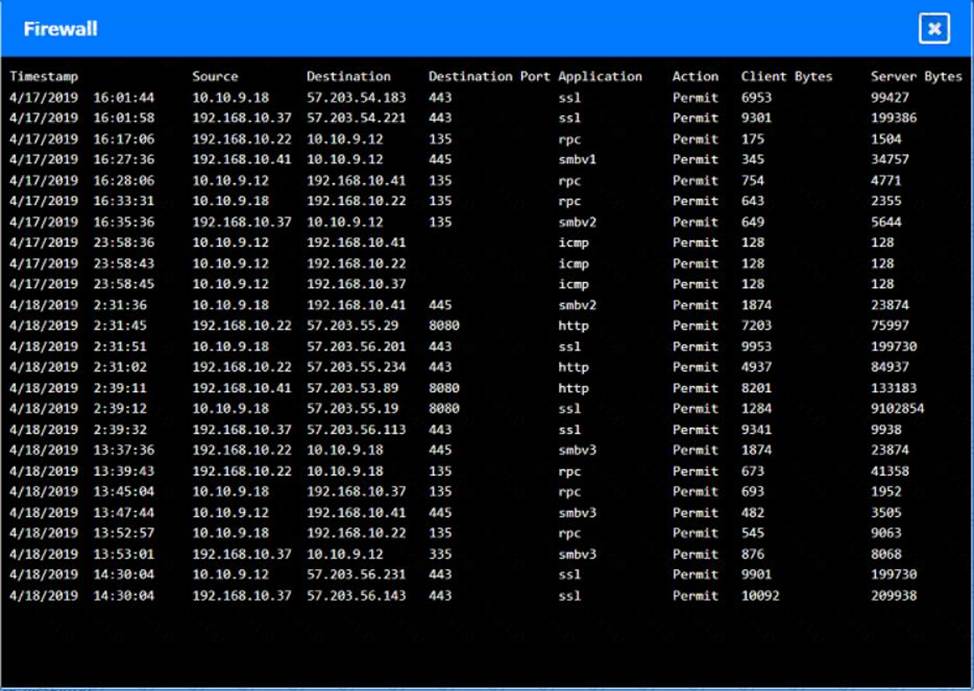
HOTSPOT
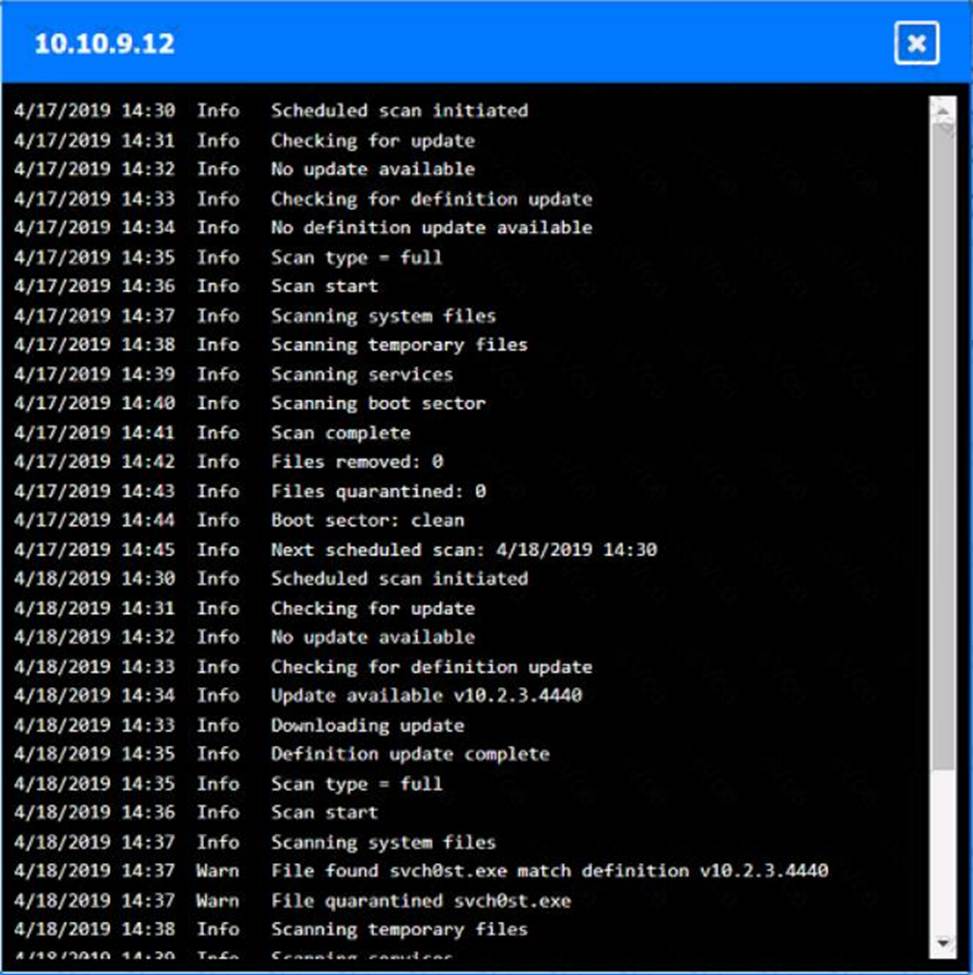
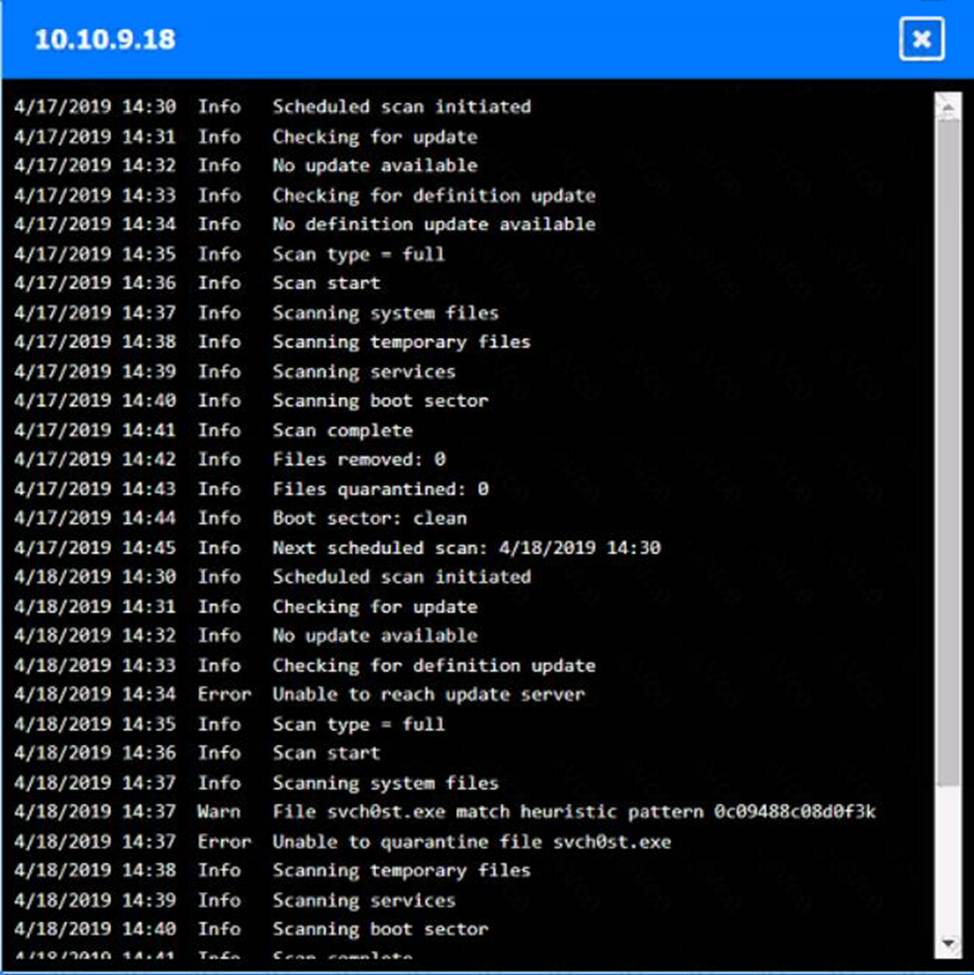
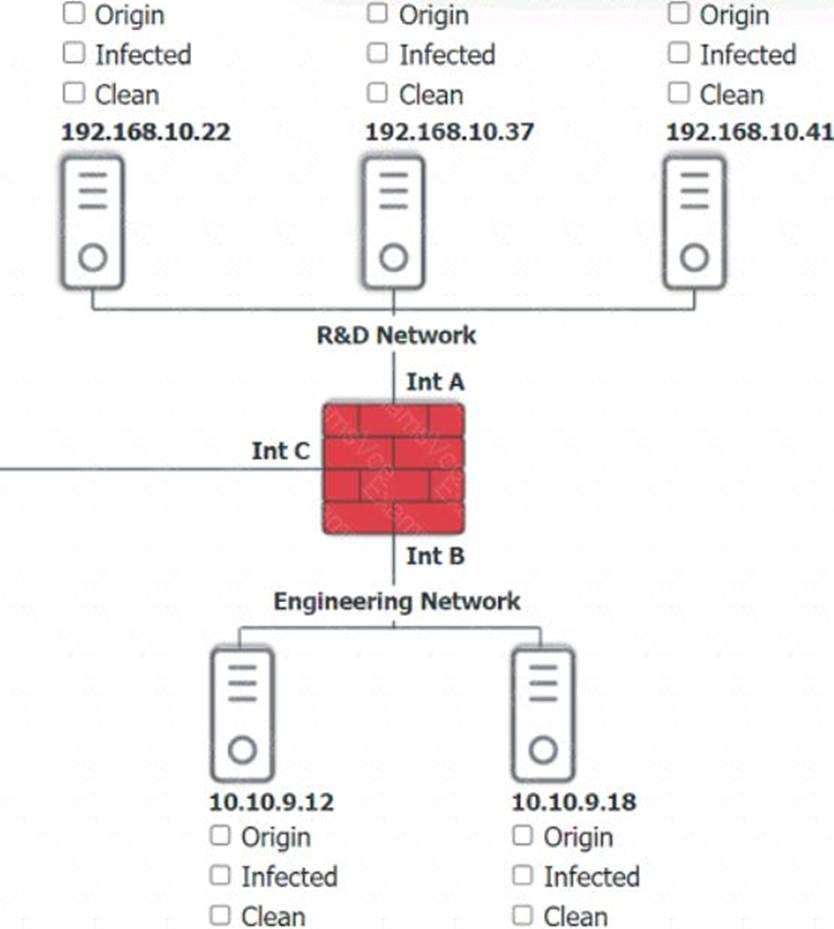
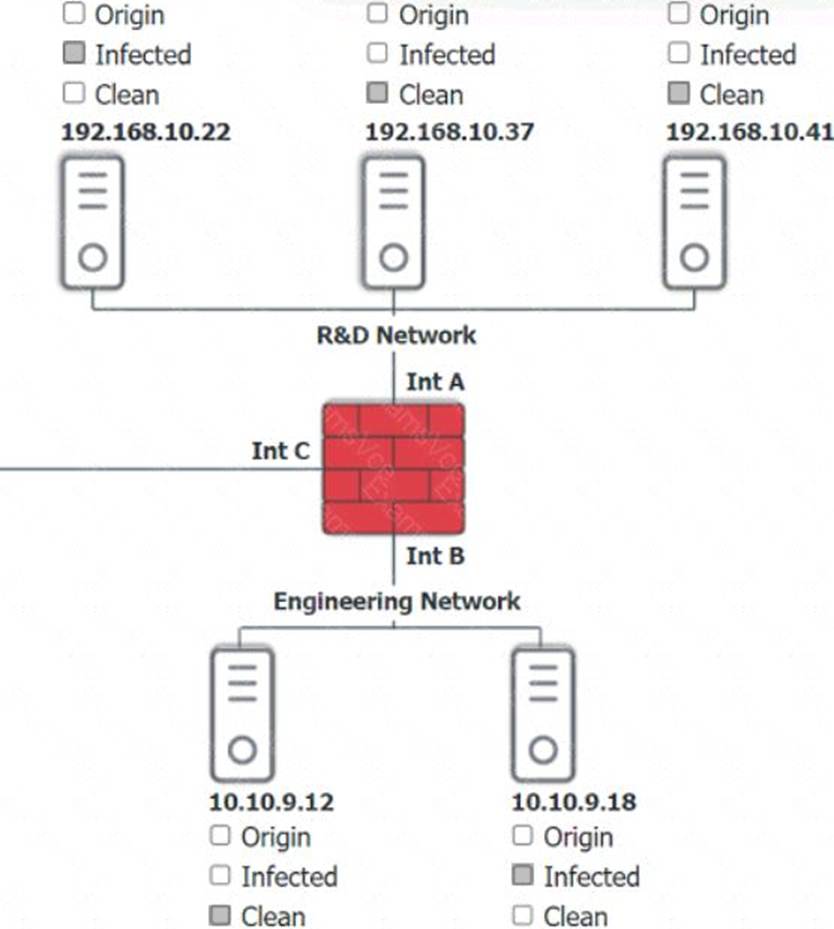
You are security administrator investigating a potential infection on a network.
Click on each host and firewall. Review all logs to determine which host originated the Infecton and then deny each remaining hosts clean or infected.
An organization needs to monitor its users’ activities to prevent insider threats.
Which of the following solutions would help the organization achieve this goal?
- A . Behavioral analytics
- B . Access control lists
- C . Identity and access management
- D . Network intrusion detection system
Employees located off-site must have access to company resources in order to complete their assigned tasks These employees utilize a solution that allows remote access without interception concerns.
Which of the following best describes this solution?
- A . Proxy server
- B . NGFW
- C . VPN
- D . Security zone
Which of the following best represents an application that does not have an on-premises requirement and is accessible from anywhere?
- A . Pass
- B . Hybrid cloud
- C . Private cloud
- D . IaaS
- E . SaaS
A company hired a consultant to perform an offensive security assessment covering penetration testing and social engineering.
Which of the following teams will conduct this assessment activity?
- A . White
- B . Purple
- C . Blue
- D . Red
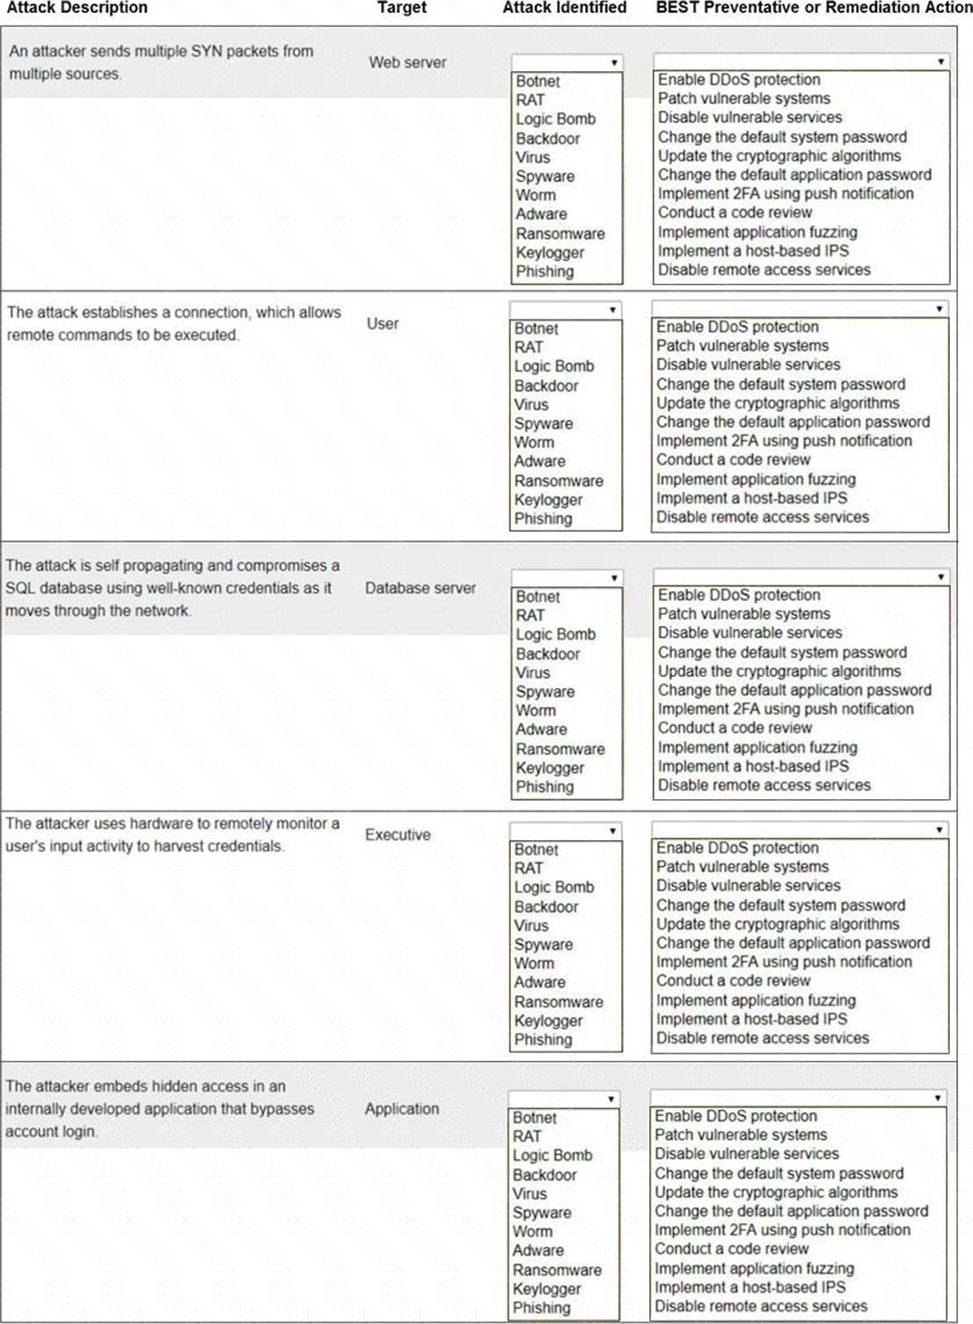
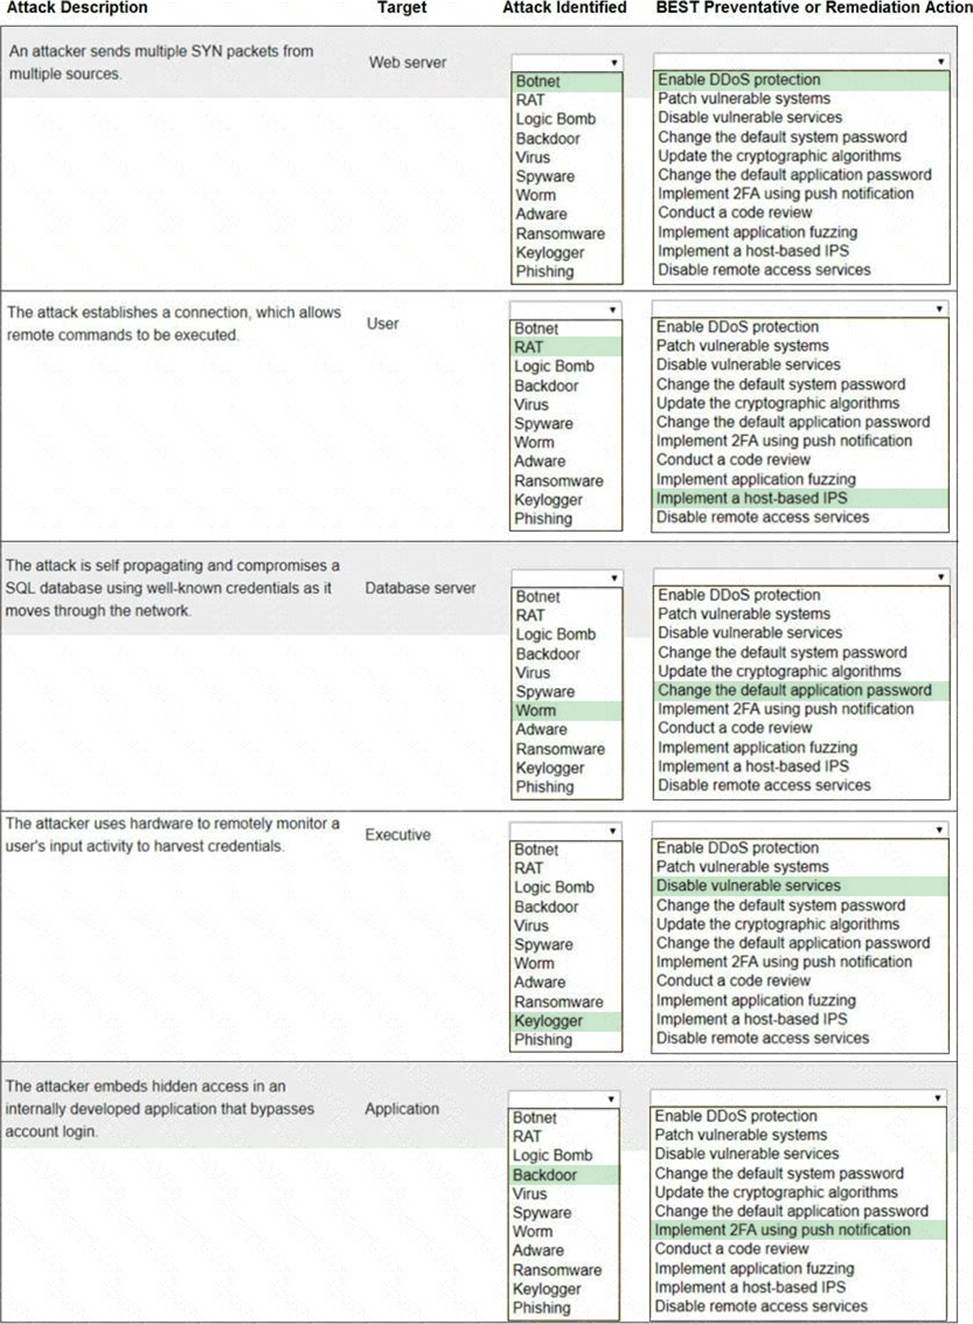
HOTSPOT
Select the appropriate attack and remediation from each drop-down list to label the corresponding attack with its remediation.
INSTRUCTIONS
Not all attacks and remediation actions will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
A vendor needs to remotely and securely transfer files from one server to another using the command line.
Which of the following protocols should be Implemented to allow for this type of access? (Select two).
- A . SSH
- B . SNMP
- C . RDP
- D . S/MIME
- E . SMTP
- F . SFTP
Which of the following describes the procedures a penetration tester must follow while conducting a test?
- A . Rules of engagement
- B . Rules of acceptance
- C . Rules of understanding
- D . Rules of execution
A company is developing a business continuity strategy and needs to determine how many staff members would be required to sustain the business in the case of a disruption.
Which of the following best describes this step?
- A . Capacity planning
- B . Redundancy
- C . Geographic dispersion
- D . Tablet exercise
A business uses Wi-Fi with content filleting enabled. An employee noticed a coworker accessed a blocked sue from a work computer and repotted the issue. While Investigating the issue, a security administrator found another device providing internet access to certain employees.
Which of the following best describes the security risk?
- A . The host-based security agent Is not running on all computers.
- B . A rogue access point Is allowing users to bypass controls.
- C . Employees who have certain credentials are using a hidden SSID.
- D . A valid access point is being jammed to limit availability.