
CompTIA SY0-701 Practice Exams
Last updated on Oct 22,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Oct 22,2026
A security analyst receives an alert from a corporate endpoint used by employees to issue visitor badges.
The alert contains the following details:
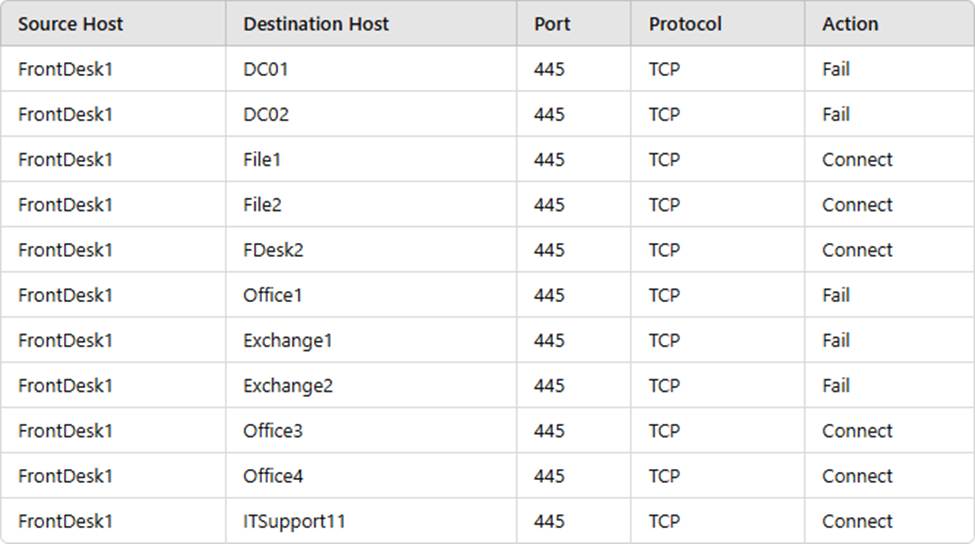
Which of the following best describes the indicator that triggered the alert?
- A . Blocked content
- B . Brute-force attack
- C . Concurrent session usage
- D . Account lockout
Which of the following is a reason why a forensic specialist would create a plan to preserve data after an modem and prioritize the sequence for performing forensic analysis?
- A . Order of volatility
- B . Preservation of event logs
- C . Chain of custody
- D . Compliance with legal hold
A systems administrator is creating a script that would save time and prevent human error when performing account creation for a large number of end users.
Which of the following would be a good use case for this task?
- A . Off-the-shelf software
- B . Orchestration
- C . Baseline
- D . Policy enforcement
A company is utilizing an offshore team to help support the finance department. The company wants to keep the data secure by keeping it on a company device but does not want to provide equipment to the offshore team.
Which of the following should the company implement to meet this requirement?
- A . VDI
- B . MDM
- C . VPN
- D . VPC
An organization implemented cloud-managed IP cameras to monitor building entry points and sensitive areas. The service provider enables direct TCP/IP connection to stream live video footage from each camera. The organization wants to ensure this stream is encrypted and authenticated.
Which of the following protocols should be implemented to best meet this objective?
- A . SSH
- B . SRTP
- C . S/MIME
- D . PPTP
A business uses Wi-Fi with content filleting enabled. An employee noticed a coworker accessed a blocked sue from a work computer and repotted the issue. While Investigating the issue, a security administrator found another device providing internet access to certain employees.
Which of the following best describes the security risk?
- A . The host-based security agent Is not running on all computers.
- B . A rogue access point Is allowing users to bypass controls.
- C . Employees who have certain credentials are using a hidden SSID.
- D . A valid access point is being jammed to limit availability.
A company is planning to set up a SIEM system and assign an analyst to review the logs on a weekly basis.
Which of the following types of controls is the company setting up?
- A . Corrective
- B . Preventive
- C . Detective
- D . Deterrent
Which of the following best describes why me SMS DIP authentication method is more risky to implement than the TOTP method?
- A . The SMS OTP method requires an end user to have an active mobile telephone service and SIM card.
- B . Generally. SMS OTP codes are valid for up to 15 minutes while the TOTP time frame is 30 to 60 seconds
- C . The SMS OTP is more likely to be intercepted and lead to unauthorized disclosure of the code than the TOTP method.
- D . The algorithm used to generate on SMS OTP code is weaker than the one used to generate a TOTP code
A security analyst is reviewing alerts in the SIEM related to potential malicious network traffic coming from an employee’s corporate laptop. The security analyst has determined that additional data about the executable running on the machine is necessary to continue the investigation.
Which of the following logs should the analyst use as a data source?
- A . Application
- B . IPS/IDS
- C . Network
- D . Endpoint
The application development teams have been asked to answer the following questions:
• Does this application receive patches from an external source?
• Does this application contain open-source code?
• is this application accessible by external users?
• Does this application meet the corporate password standard?
Which of the following are these questions port of?
- A . Risk control self-assessment
- B . Risk management strategy
- C . Risk acceptance
- D . Risk matrix