
CompTIA SY0-701 Practice Exams
Last updated on Nov 16,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A business uses Wi-Fi with content filleting enabled. An employee noticed a coworker accessed a blocked sue from a work computer and repotted the issue. While Investigating the issue, a security administrator found another device providing internet access to certain employees.
Which of the following best describes the security risk?
- A . The host-based security agent Is not running on all computers.
- B . A rogue access point Is allowing users to bypass controls.
- C . Employees who have certain credentials are using a hidden SSID.
- D . A valid access point is being jammed to limit availability.
B
Explanation:
The presence of another device providing internet access that bypasses the content filtering system indicates the existence of a rogue access point. Rogue access points are unauthorized devices that can create a backdoor into the network, allowing users to bypass security controls like content filtering. This presents a significant security risk as it can expose the network to unauthorized access and potential data breaches.
Reference =
CompTIA Security+ SY0-701 Course Content: Rogue access points are highlighted as a major security risk, allowing unauthorized access to the network and bypassing security measures.
An IT administrator needs to ensure data retention standards are implemented on an enterprise application.
Which of the Mowing describes the administrator’s role?
- A . Processor
- B . Custodian
- C . Privacy officer
- D . Owner
Which of the following activities uses OSINT?
- A . Social engineering testing
- B . Data analysis of logs
- C . Collecting evidence of malicious activity
- D . Producing IOC for malicious artifacts
The security operations center is researching an event concerning a suspicious IP address A security analyst looks at the following event logs and discovers that a significant portion of the user accounts have experienced faded log-In attempts when authenticating from the same IP address:
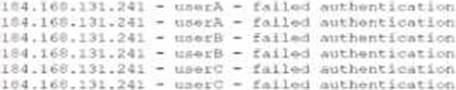
Which of the following most likely describes attack that took place?
- A . Spraying
- B . Brute-force
- C . Dictionary
- D . Rainbow table
An attacker submits a request containing unexpected characters in an attempt to gain unauthorized access to information within the underlying systems.
Which of the following best describes this attack?
- A . Side loading
- B . Target of evaluation
- C . Resource reuse
- D . SQL injection
Which of the following is the best way to improve the confidentiality of remote connections to an enterprise’s infrastructure?
- A . Firewalls
- B . Virtual private networks
- C . Extensive logging
- D . Intrusion detection systems
B
Explanation:
A Virtual Private Network (VPN) (B) encrypts all data transmitted between remote users and the enterprise infrastructure, ensuring confidentiality. VPNs are essential in protecting sensitive data from interception over untrusted networks.
This is covered under Domain 3.3: Secure network designs, where VPNs are listed as a key control for ensuring confidentiality of remote connections.
Reference: CompTIA Security+ SY0-701 Objectives, Domain 3.3 C “Remote access security: VPN (ensures confidentiality).”
An organization maintains intellectual property that it wants to protect.
Which of the following concepts would be most beneficial to add to the company’s security awareness training program?
- A . Insider threat detection
- B . Simulated threats
- C . Phishing awareness
- D . Business continuity planning
Which of the following activities is included in the post-incident review phase?
- A . Determining the root cause of the incident
- B . Developing steps to mitigate the risks of the incident
- C . Validating the accuracy of the evidence collected during the investigation
- D . Reestablishing the compromised system’s configuration and settings
Which of the following threat actors would most likely deface the website of a high-profile music group?
- A . Unskilled attacker
- B . Organized crime
- C . Nation-state
- D . Insider threat
A
Explanation:
Detailed An unskilled attacker, often referred to as a script kiddie, is likely to engage in website defacement. This type of attack typically requires minimal expertise and is often conducted for notoriety.
Reference: CompTIA Security+ SY0-701 Study Guide, Domain 2: Threats, Section: "Threat Actors and Motivations".
A Chief Information Security Officer (CISO) wants to explicitly raise awareness about the increase of
ransomware-as-a-service in a report to the management team.
Which of the following best describes the threat actor in the CISO’s report?
- A . Insider threat
- B . Hacktivist
- C . Nation-state
- D . Organized crime
D
Explanation:
Ransomware-as-a-service is a type of cybercrime where hackers sell or rent ransomware tools or services to other criminals who use them to launch attacks and extort money from victims. This is a typical example of organized crime, which is a group of criminals who work together to conduct illegal activities for profit. Organized crime is different from other types of threat actors, such as insider threats, hacktivists, or nation-states, who may have different motives, methods, or targets.
Reference: CompTIA Security+ Study Guide: Exam SY0-701, 9th Edition, page 17 1