
CompTIA SY0-701 Practice Exams
Last updated on Nov 16,2026- Exam Code: SY0-701
- Exam Name: CompTIA Security+
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
An analyst is evaluating the implementation of Zero Trust principles within the data plane.
Which of the following would be most relevant for the analyst to evaluate?
- A . Secured zones
- B . Subject role
- C . Adaptive identity
- D . Threat scope reduction
D
Explanation:
The data plane, also known as the forwarding plane, is the part of the network that carries user traffic and data. It is responsible for moving packets from one device to another based on the routing and switching decisions made by the control plane. The data plane is a critical component of the Zero Trust architecture, as it is where most of the attacks and breaches occur. Therefore, implementing Zero Trust principles within the data plane can help to improve the security and resilience of the network.
One of the key principles of Zero Trust is to assume breach and minimize the blast radius and segment access. This means that the network should be divided into smaller and isolated segments or zones, each with its own security policies and controls. This way, if one segment is compromised, the attacker cannot easily move laterally to other segments and access more resources or data. This principle is also known as threat scope reduction, as it reduces the scope and impact of a potential threat.
The other options are not as relevant for the data plane as threat scope reduction. Secured zones are a concept related to the control plane, which is the part of the network that makes routing and switching decisions. Subject role is a concept related to the identity plane, which is the part of the network that authenticates and authorizes users and devices. Adaptive identity is a concept related to the policy plane, which is the part of the network that defines and enforces the security policies and rules.
Reference = https://bing.com/search?q=Zero+Trust+data+plane
https://learn.microsoft.com/en-us/security/zero-trust/deploy/data
A security analyst is reviewing logs and discovers the following:
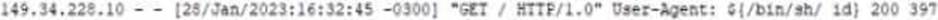
Which of the following should be used lo best mitigate this type of attack?
- A . Input sanitization
- B . Secure cookies
- C . Static code analysis
- D . Sandboxing
A company evaluates several options that would allow employees to have remote access to the network. The security team wants to ensure the solution includes AAA to comply with internal security policies.
Which of the following should the security team recommend?
- A . IPSec with RADIUS
- B . RDP connection with LDAPS
- C . Web proxy for all remote traffic
- D . Jump server with 802.1X
A company’s website is www. Company. com Attackers purchased the domain wwww.company.com
Which of the following types of attacks describes this example?
- A . Typosquatting
- B . Brand Impersonation
- C . On-path
- D . Watering-hole
A
Explanation:
"Typosquatting, also known as URL hijacking, is a form of cybersquatting where attackers register domain names that are intentionally similar to legitimate ones, often differing by a single character or a common typographical error. For example, an attacker might register ‘wwww.company.com’ to mimic ‘www.company.com,’ tricking users who mistype the URL into visiting a malicious site. This attack exploits human error and can be used to steal credentials, distribute malware, or impersonate the legitimate entity."
Reference: CompTIA Security+ SY0-701 Study Guide, Domain 1.0: General Security Concepts, Section: "Social Engineering Attacks and Threats" (Typosquatting is typically covered under threats related to domain misuse).
In this scenario, the attackers registered "wwww.company.com," which is a subtle variation of "www.company.com," relying on users mistyping or not noticing the extra "w." This fits the definition of typosquatting perfectly. Brand impersonation (B) is related but broader and doesn’t specifically tie to typographical errors. On-path (C) involves intercepting communication, and watering-hole (D) targets users via compromised legitimate sites―neither applies here.
The private key for a website was stolen, and a new certificate has been issued.
Which of the following needs to be updated next?
- A . SCEP
- B . CRL
- C . OCSP
- D . CSR
Sine© a recent upgrade (o a WLAN infrastructure, several mobile users have been unable to access the internet from the lobby. The networking team performs a heat map survey of the building and finds several WAPs in the area. The WAPs are using similar frequencies with high power settings.
Which of the following installation considerations should the security team evaluate next?
- A . Channel overlap
- B . Encryption type
- C . New WLAN deployment
- D . WAP placement
A
Explanation:
When multiple Wireless Access Points (WAPs) are using similar frequencies with high power settings,
it can cause channel overlap, leading to interference and connectivity issues. This is likely the reason why mobile users are unable to access the internet in the lobby. Evaluating and adjusting the channel settings on the WAPs to avoid overlap is crucial to resolving the connectivity problems.
Reference = CompTIA Security+ SY0-701 study materials, particularly the domain on Wireless and Mobile Security, which covers WLAN deployment considerations.
A company processes and stores sensitive data on its own systems.
Which of the following steps should the company take first to ensure compliance with privacy regulations?
- A . Implement access controls and encryption.
- B . Develop and provide training on data protection policies.
- C . Create incident response and disaster recovery plans.
- D . Purchase and install security software.
Which of the following tasks is typically included in the BIA process?
- A . Estimating the recovery time of systems
- B . Identifying the communication strategy
- C . Evaluating the risk management plan
- D . Establishing the backup and recovery procedures
- E . Developing the incident response plan
A spoofed identity was detected for a digital certificate.
Which of the following are the type of unidentified key and the certificate mat could be in use on the company domain?
- A . Private key and root certificate
- B . Public key and expired certificate
- C . Private key and self-signed certificate
- D . Public key and wildcard certificate
C
Explanation:
A self-signed certificate is a certificate that is signed by its own private key rather than by a trusted certificate authority (CA). This means that the authenticity of the certificate relies solely on the issuer’s own authority. If a spoofed identity was detected, it could indicate that a private key associated with a self-signed certificate was compromised. Self-signed certificates are often used internally within organizations, but they carry higher risks since they are not validated by a third-party CA, making them more susceptible to spoofing.
Reference = CompTIA Security+ SY0-701 study materials, particularly the domains discussing Public Key Infrastructure (PKI) and certificate management.
Which of the following allows an exploit to go undetected by the operating system?
- A . Firmware vulnerabilities
- B . Side loading
- C . Memory injection
- D . Encrypted payloads