
CompTIA PT0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: PT0-003
- Exam Name: CompTIA PenTest+ Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
In a file stored in an unprotected source code repository, a penetration tester discovers the following line of code:
sshpass -p donotchange ssh [email protected]
Which of the following should the tester attempt to do next to take advantage of this information? (Select two).
- A . Use Nmap to identify all the SSH systems active on the network.
- B . Take a screen capture of the source code repository for documentation purposes.
- C . Investigate to find whether other files containing embedded passwords are in the code repository.
- D . Confirm whether the server 192.168.6.14 is up by sending ICMP probes.
- E . Run a password-spraying attack with Hydra against all the SSH servers.
- F . Use an external exploit through Metasploit to compromise host 192.168.6.14.
A penetration tester needs to test a very large number of URLs for public access. Given the following code snippet:
1 import requests
2 import pathlib
3
4 for url in pathlib.Path("urls.txt").read_text().split("n"):
5 response = requests.get(url)
6 if response.status == 401:
7 print("URL accessible")
Which of the following changes is required?
- A . The condition on line 6
- B . The method on line 5
- C . The import on line 1
- D . The delimiter in line 3
SIMULATION
A previous penetration test report identified a host with vulnerabilities that was successfully exploited. Management has requested that an internal member of the security team reassess the host to determine if the vulnerability still exists.
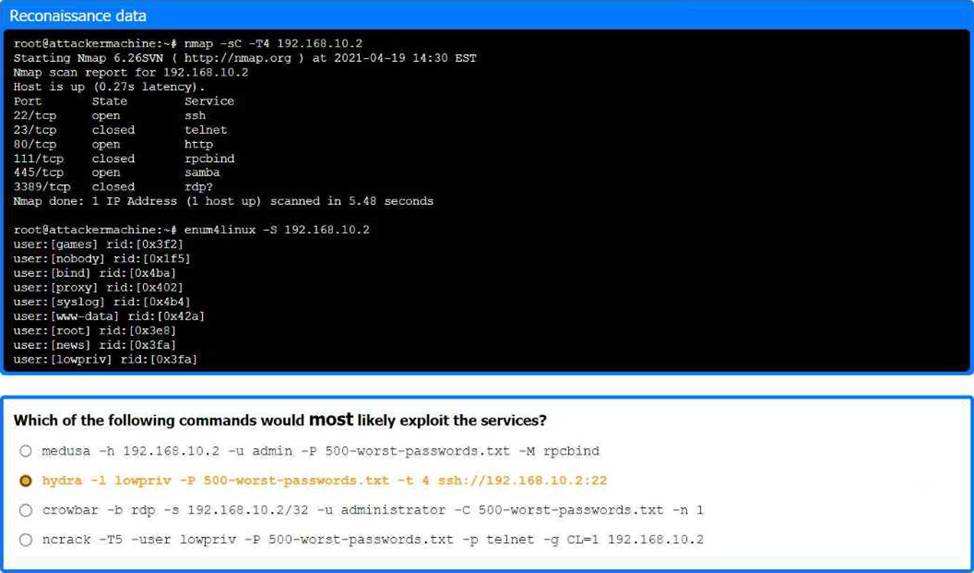
Part 1:
. Analyze the output and select the command to exploit the vulnerable service.
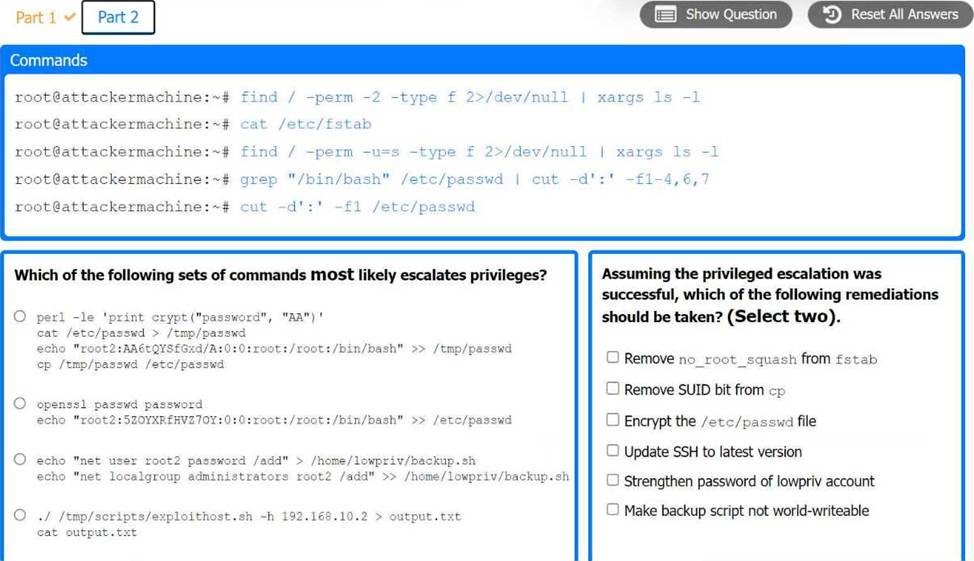
Part 2:
. Analyze the output from each command.
・ Select the appropriate set of commands to escalate privileges.
・ Identify which remediation steps should be taken.
A tester is performing an external phishing assessment on the top executives at a company. Two-factor authentication is enabled on the executives’ accounts that are in the scope of work.
Which of the following should the tester do to get access to these accounts?
- A . Configure an external domain using a typosquatting technique. Configure Evilginx to bypass two-factor authentication using a phishlet that simulates the mail portal for the company.
- B . Configure Gophish to use an external domain. Clone the email portal web page from the company and get the two-factor authentication code using a brute-force attack method.
- C . Configure an external domain using a typosquatting technique. Configure SET to bypass two-factor authentication using a phishlet that mimics the mail portal for the company.
- D . Configure Gophish to use an external domain. Clone the email portal web page from the company and get the two-factor authentication code using a vishing method.