
CompTIA PT0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: PT0-003
- Exam Name: CompTIA PenTest+ Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A penetration tester discovers data to stage and exfiltrate. The client has authorized movement to the tester’s attacking hosts only.
Which of the following would be most appropriate to avoid alerting the SOC?
- A . Apply UTF-8 to the data and send over a tunnel to TCP port 25.
- B . Apply Base64 to the data and send over a tunnel to TCP port 80.
- C . Apply 3DES to the data and send over a tunnel UDP port 53.
- D . Apply AES-256 to the data and send over a tunnel to TCP port 443.
A penetration tester discovers data to stage and exfiltrate. The client has authorized movement to the tester’s attacking hosts only.
Which of the following would be most appropriate to avoid alerting the SOC?
- A . Apply UTF-8 to the data and send over a tunnel to TCP port 25.
- B . Apply Base64 to the data and send over a tunnel to TCP port 80.
- C . Apply 3DES to the data and send over a tunnel UDP port 53.
- D . Apply AES-256 to the data and send over a tunnel to TCP port 443.
During a pre-engagement activity with a new customer, a penetration tester looks for assets to test.
Which of the following is an example of a target that can be used for testing?
- A . API
- B . HTTP
- C . IPA
- D . ICMP
During a penetration test, a junior tester uses Hunter.io for an assessment and plans to review the information that will be collected.
Which of the following describes the information the junior tester will receive from the Hunter.io tool?
- A . A collection of email addresses for the target domain that is available on multiple sources on the internet
- B . DNS records for the target domain and subdomains that could be used to increase the external attack surface
- C . Data breach information about the organization that could be used for additional enumeration
- D . Information from the target’s main web page that collects usernames, metadata, and possible data exposures
During an engagement, a penetration tester wants to enumerate users from Linux systems by using finger and rwho commands. However, the tester realizes these commands alone will not achieve the desired result.
Which of the following is the best tool to use for this task?
- A . Nikto
- B . Burp Suite
- C . smbclient
- D . theHarvester
While conducting a peer review for a recent assessment, a penetration tester finds the debugging mode is still enabled for the production system.
Which of the following is most likely responsible for this observation?
- A . Configuration changes were not reverted.
- B . A full backup restoration is required for the server.
- C . The penetration test was not completed on time.
- D . The penetration tester was locked out of the system.
During a penetration testing exercise, a team decides to use a watering hole strategy.
Which of the following is the most effective approach for executing this attack?
- A . Compromise a website frequently visited by the organization’s employees.
- B . Launch a DDoS attack on the organization’s website.
- C . Create fake social media profiles to befriend employees.
- D . Send phishing emails to the organization’s employees.
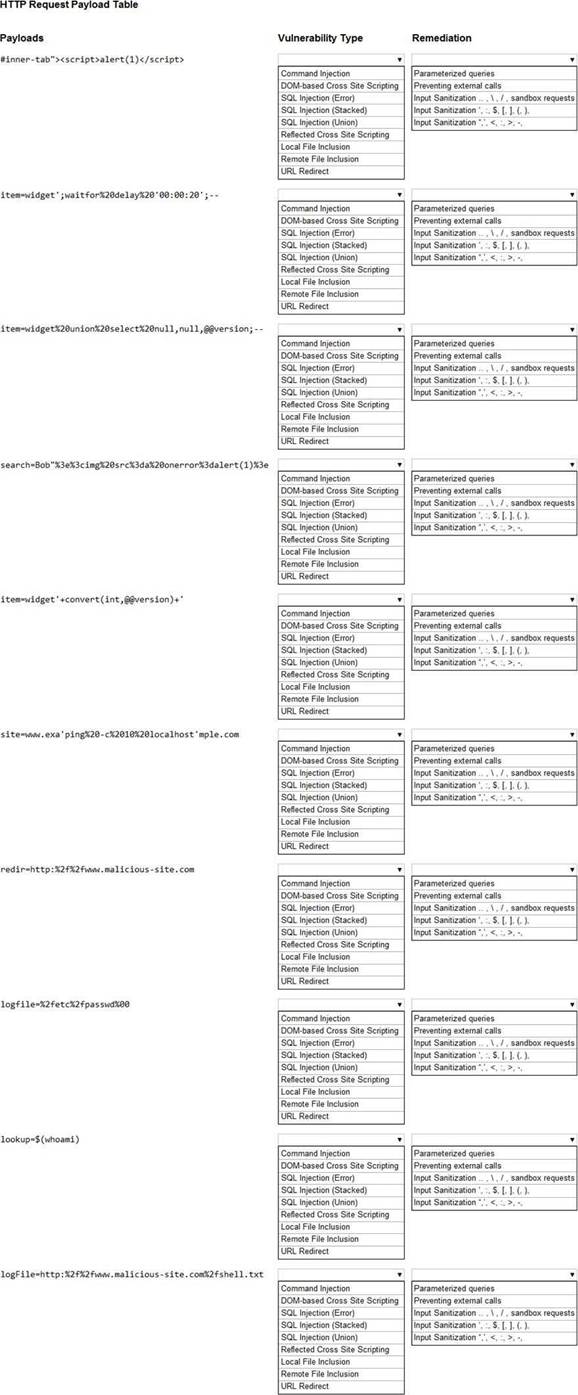
HOTSPOT
You are a security analyst tasked with hardening a web server.
You have been given a list of HTTP payloads that were flagged as malicious.
INSTRUCTIONS
Given the following attack signatures, determine the attack type, and then identify the associated remediation to prevent the attack in the future.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
During an assessment, a penetration tester runs the following command:
setspn.exe -Q /
Which of the following attacks is the penetration tester preparing for?
- A . LDAP injection
- B . Pass-the-hash
- C . Kerberoasting
- D . Dictionary
A penetration tester is authorized to perform a DoS attack against a host on a network.
Given the following input:
ip = IP("192.168.50.2")
tcp = TCP(sport=RandShort(), dport=80, flags="S")
raw = RAW(b"X"*1024)
p = ip/tcp/raw
send(p, loop=1, verbose=0)
Which of the following attack types is most likely being used in the test?
- A . MDK4
- B . Smurf attack
- C . FragAttack
- D . SYN flood