CompTIA PT0-003 Practice Exams
Last updated on Oct 01,2026- Exam Code: PT0-003
- Exam Name: CompTIA PenTest+ Exam
- Certification Provider: CompTIA
- Latest update: Oct 01,2026
While conducting an assessment, a penetration tester identifies the details for several unreleased products announced at a company-wide meeting.
Which of the following attacks did the tester most likely use to discover this information?
- A . Eavesdropping
- B . Bluesnarfing
- C . Credential harvesting
- D . SQL injection attack
Which of the following is a term used to describe a situation in which a penetration tester bypasses physical access controls and gains access to a facility by entering at the same time as an employee?
- A . Badge cloning
- B . Shoulder surfing
- C . Tailgating
- D . Site survey
During an engagement, a penetration tester found some weaknesses that were common across the customer’s entire environment. The weaknesses included the following: Weaker password settings than the company standard
Systems without the company’s endpoint security software installed Operating systems that were not updated by the patch management system
Which of the following recommendations should the penetration tester provide to address the root issue?
- A . Add all systems to the vulnerability management system.
- B . Implement a configuration management system.
- C . Deploy an endpoint detection and response system.
- D . Patch the out-of-date operating systems.
Given the following statements:
Implement a web application firewall.
Upgrade end-of-life operating systems.
Implement a secure software development life cycle.
In which of the following sections of a penetration test report would the above statements be found?
- A . Executive summary
- B . Attack narrative
- C . Detailed findings
- D . Recommendations
A penetration tester assesses an application allow list and has limited command-line access on the Windows system.
Which of the following would give the penetration tester information that could aid in continuing the test?
- A . mmc.exe
- B . icacls.exe
- C . nltest.exe
- D . rundll.exe
A penetration tester assesses an application allow list and has limited command-line access on the Windows system.
Which of the following would give the penetration tester information that could aid in continuing the test?
- A . mmc.exe
- B . icacls.exe
- C . nltest.exe
- D . rundll.exe
A penetration tester is conducting a wireless security assessment for a client with 2.4GHz and 5GHz access points. The tester places a wireless USB dongle in the laptop to start capturing WPA2 handshakes.
Which of the following steps should the tester take next?
- A . Enable monitoring mode using Aircrack-ng.
- B . Use Kismet to automatically place the wireless dongle in monitor mode and collect handshakes.
- C . Run KARMA to break the password.
- D . Research WiGLE.net for potential nearby client access points.
During an assessment, a penetration tester wants to extend the vulnerability search to include the use of dynamic testing.
Which of the following tools should the tester use?
- A . Mimikatz
- B . ZAP
- C . OllyDbg
- D . SonarQube
A penetration tester finished a security scan and uncovered numerous vulnerabilities on several hosts.
Based on the targets’ EPSS and CVSS scores, which of the following targets is the most likely to get attacked?
- A . Target 1: EPSS Score = 0.6 and CVSS Score = 4
- B . Target 2: EPSS Score = 0.3 and CVSS Score = 2
- C . Target 3: EPSS Score = 0.6 and CVSS Score = 1
- D . Target 4: EPSS Score = 0.4 and CVSS Score = 4.5
SIMULATION
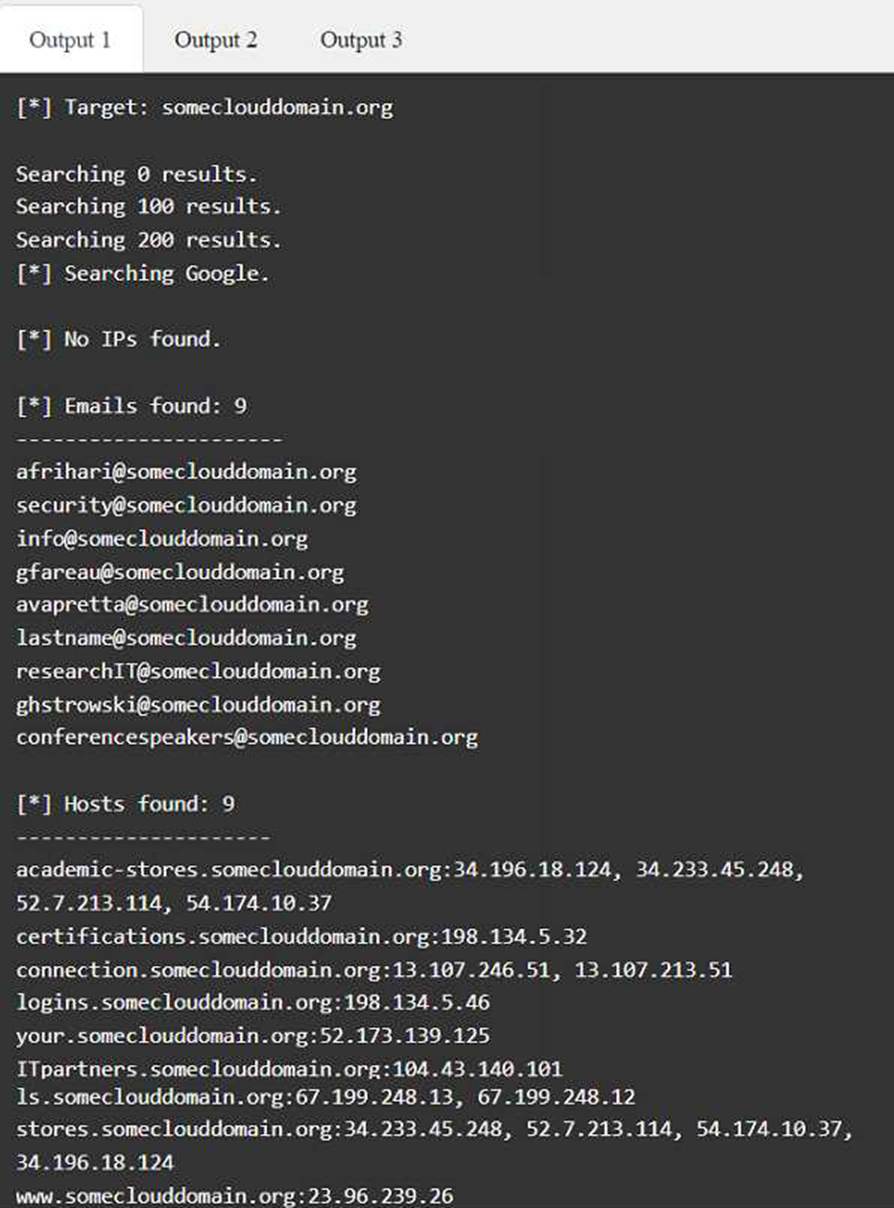
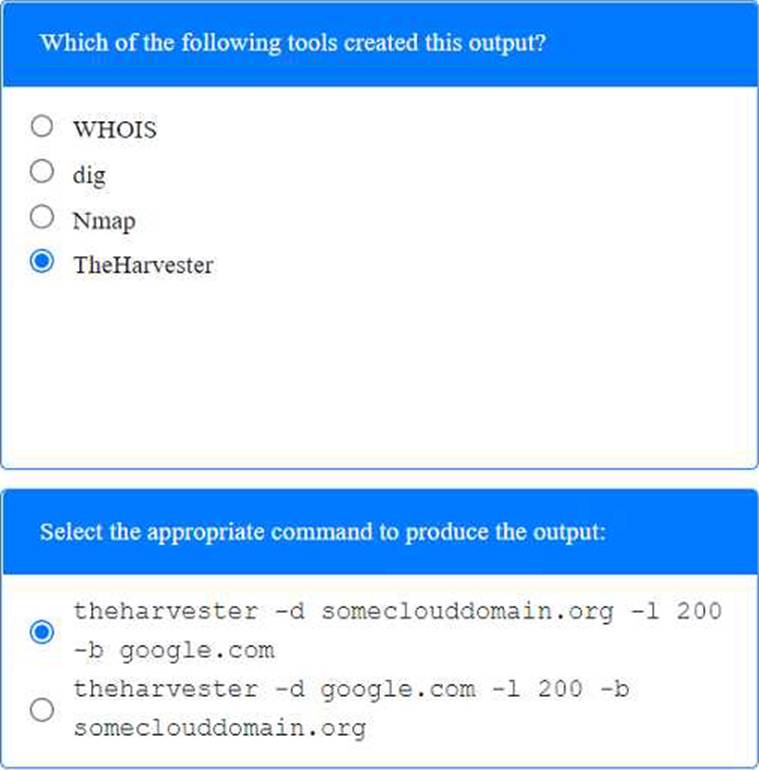
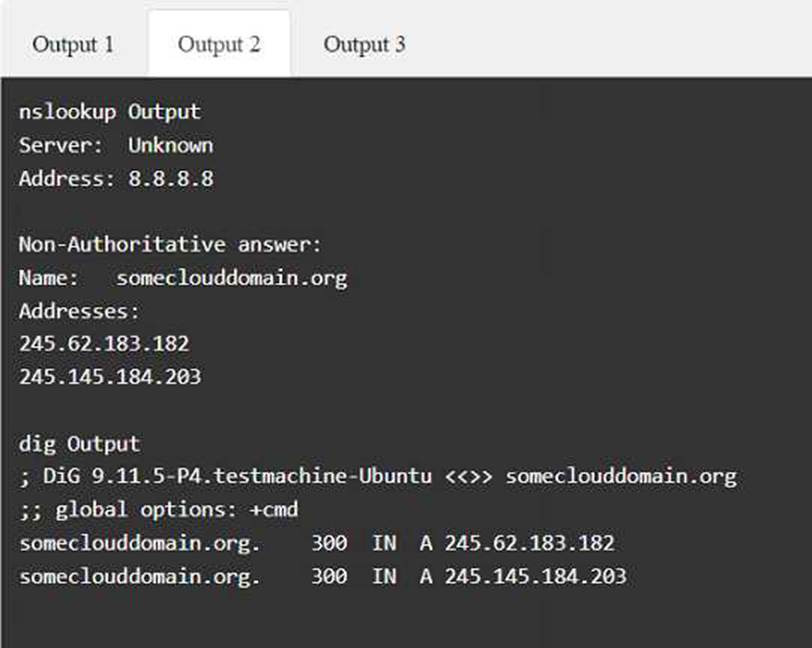
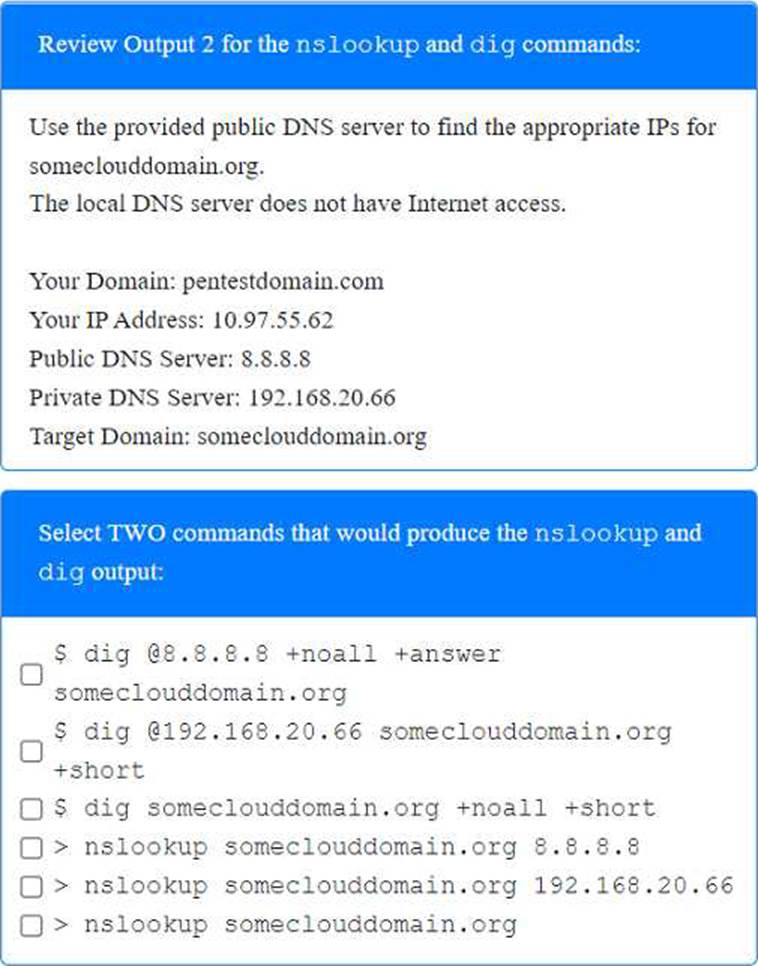
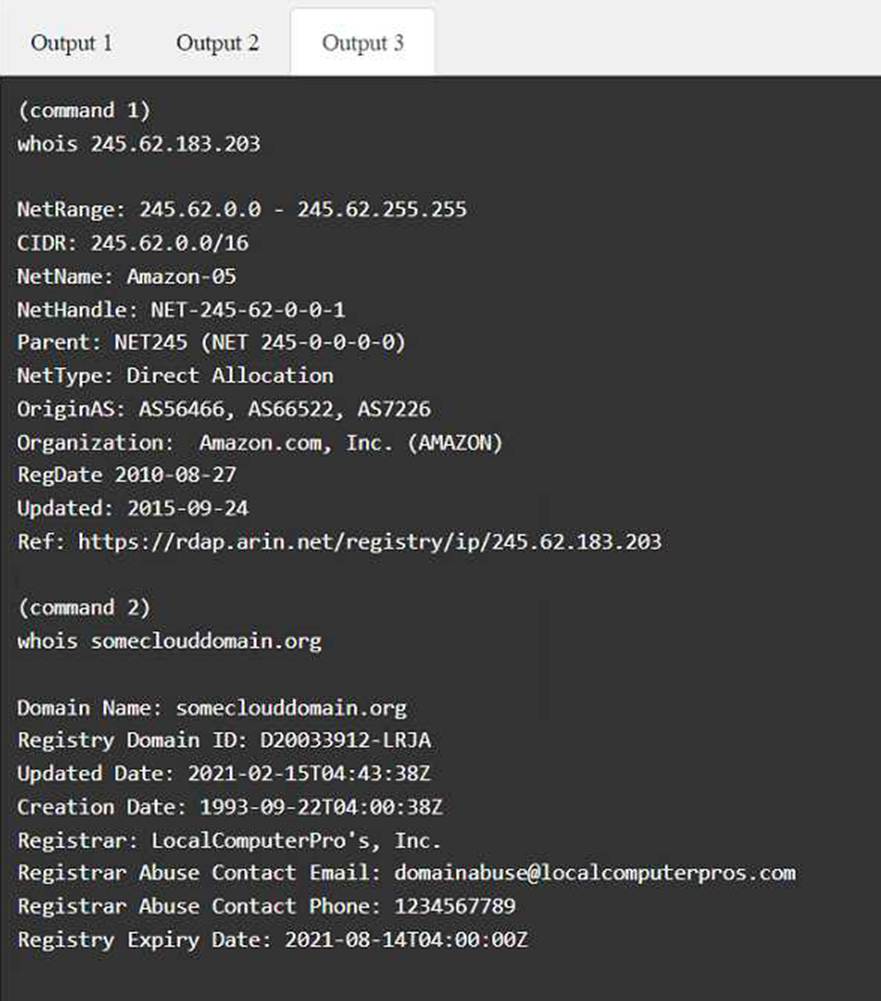
A penetration tester has been provided with only the public domain name and must enumerate additional information for the public-facing assets.
INSTRUCTIONS
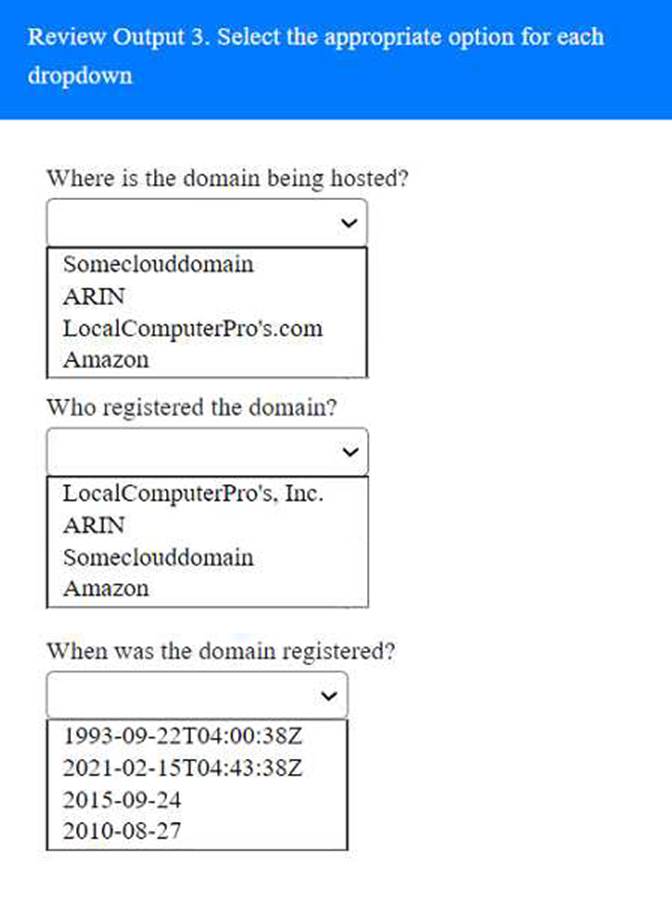
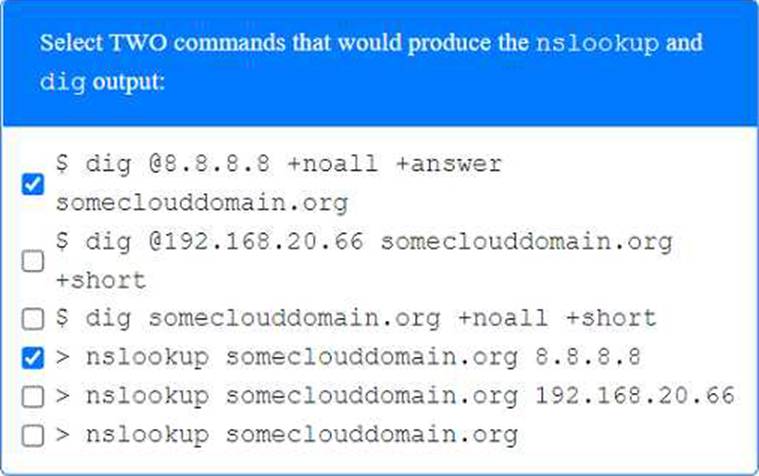
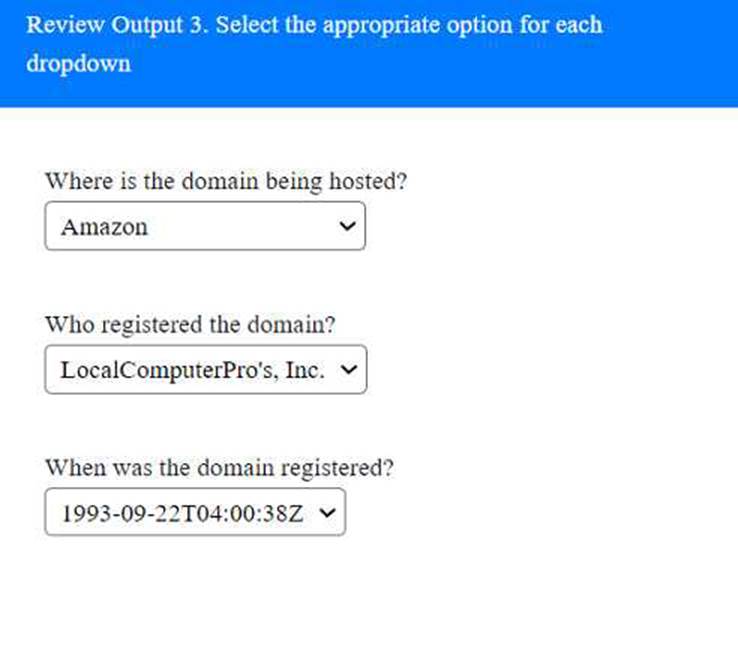
Select the appropriate answer(s), given the output from each section.
Output 1