
Cisco 300-710 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-710
- Exam Name: Securing Networks with Cisco Firepower (SNCF)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
An administrator is attempting to add a Cisco Secure Firewall Threat Defence device to Cisco Secure Firewall Management Center with a password of Cisco0480846211 480846211. The private IP address of the FMC server is 192.168.75.201.
Which command must be used in order to accomplish this task?
- A . configure manager add 192.168.75.201/24 <reg_key>
- B . configure manager add 192.16875.201 <reg_key>
- C . configure manager add 192.168.45.45 <reg_key> <nal-ld>
- D . configure manager add 192.168.75.201 255.255.255.0 <reg_key>
A network administrator is trying to configure Active Directory authentication for VPN authentication to a Cisco Secure Firewall Threat Defence instance that is registered with Cisco Secure Firewall Management Center.
Which system settings must be configured first in Secure Firewall Management Center to accomplish the goal?
- A . Device, Remote Access VPN
- B . System, Realms
- C . Policies, Authentication
- D . Authentication, Device
A security engineer must configure policies tor a recently deployed Cisco FTD. The security policy for the company dictates that when five or more connections from external sources are initiated within 2 minutes, there is cause for concern.
Which type of policy must be configured in Cisco FMC z
generate an alert when this condition is triggered?
- A . application detector
- B . access control
- C . intrusion
- D . correlation
An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero.
What is causing this error?
- A . Logging is not enabled for the rule.
- B . The rule was not enabled after being created.
- C . The wrong source interface for Snort was selected in the rule.
- D . An incorrect application signature was used in the rule.
What is the result when two users modify a VPN policy at the same lime on a Cisco Secure Firewall Management Center managed device?
- A . Both users can edit the policy arid the last saved configuration persists.
- B . The first user locks the configuration when selecting edit on the policy.
- C . The changes from both users will be merged together into the policy.
- D . The system prevents modifications to the policy by multiple users.
An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device.
When the engineer navigates to URL for Secure Firewall Management Center at:
..<FMC IP>/capture/CAP/pcap/sample.pcap
An engineer receives a 403: Forbidden error instead of being provided with the PCAP file.
Which action resolves the issue?
- A . Disable the HTTPS server and use HTTP.
- B . Enable the proxy setting in the device platform policy.
- C . Enable HTTPS in the device platform policy.
- D . Disable the proxy setting on the client browser.
Which firewall design allows a firewall to forward traffic at layer 2 and layer 3 for the same subnet?
- A . Cisco Firepower Threat Defense mode
- B . transparent mode
- C . routed mode
- D . integrated routing and bridging
Which connector is used to integrate Cisco ISE with Cisco FMC for Rapid Threat Containment?
- A . pxGrid
- B . FTD RTC
- C . FMC RTC
- D . ISEGrid
Refer to the exhibit.
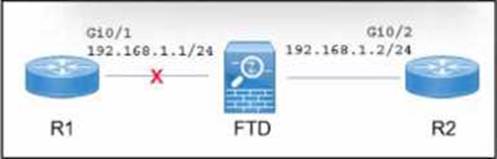
A Cisco Secure Firewall Threat Defense (FTD) device is deployed in inline mode with an inline set. The network engineer wants router R2 to remove the directly connected route M 68.1.0/24 from its routing table when the cable between routed R1 and the Secure FTD device Is disconnected.
Which action must the engineer take?
- A . Implement the Propagate Link Stale option on the Secure FTD device
- B . Establish a routing protocol between R1 and R2.
- C . Disable hardware bypass on the Secure FTD device.
- D . Implement autostate functionality on the Gi0/2 interface of R2
Which policy rule is included in the deployment of a local DMZ during the initial deployment of a Cisco NGFW through the Cisco FMC GUI?
- A . a default DMZ policy for which only a user can change the IP addresses.
- B . deny ip any
- C . no policy rule is included
- D . permit ip any