
Cisco 300-710 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-710
- Exam Name: Securing Networks with Cisco Firepower (SNCF)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
What are the minimum requirements to deploy a managed device inline?
- A . inline interfaces, security zones, MTU, and mode
- B . passive interface, MTU, and mode
- C . inline interfaces, MTU, and mode
- D . passive interface, security zone, MTU, and mode
An engineer must configure the firewall to monitor traffic within a single subnet without increasing the hop count of that traffic.
How would the engineer achieve this?
- A . Configure Cisco Firepower as a transparent firewall
- B . Set up Cisco Firepower as managed by Cisco FDM
- C . Configure Cisco Firepower in FXOS monitor only mode.
- D . Set up Cisco Firepower in intrusion prevention mode
In Cisco FTD, which condition must be met to passively receive traffic that passes through the appliance using a TAP mode?
- A . The interface must be configured as inline tap.
- B . The device must be in routed mode.
- C . The interface must be set to passive mode.
- D . The interface must be set to transparent mode.
An engineer must create an access control policy on a Cisco Secure Firewall Threat Defense device.
The company has a contact center that utilizes VoIP heavily, and it is critical that this traffic is not ….
by performance issues after deploying the access control policy.
Which access control Action rule must be configured to handle the VoIP traffic?
- A . monitor
- B . trust
- C . block
- D . allow
While integrating Cisco Umbrella with Cisco Threat Response, a network security engineer wants to automatically push blocking of domains from the Cisco Threat Response interface to Cisco Umbrell a.
Which API meets this requirement?
- A . investigate
- B . reporting
- C . enforcement
- D . REST
A network administrator reviews me attack risk report and notices several Low-Impact attacks.
What does this type of attack indicate?
- A . All attacks are listed as low until manually categorized.
- B . The host is not vulnerable to those attacks.
- C . The attacks are not dangerous to the network.
- D . The host is not within the administrator’s environment.
An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware.
Which two configuration tasks must be performed to achieve this file lookup? (Choose two).
- A . The Cisco FMC needs to include a SSL decryption policy.
- B . The Cisco FMC needs to connect to the Cisco AMP for Endpoints service.
- C . The Cisco FMC needs to connect to the Cisco ThreatGrid service directly for sandboxing.
- D . The Cisco FMC needs to connect with the FireAMP Cloud.
- E . The Cisco FMC needs to include a file inspection policy for malware lookup.
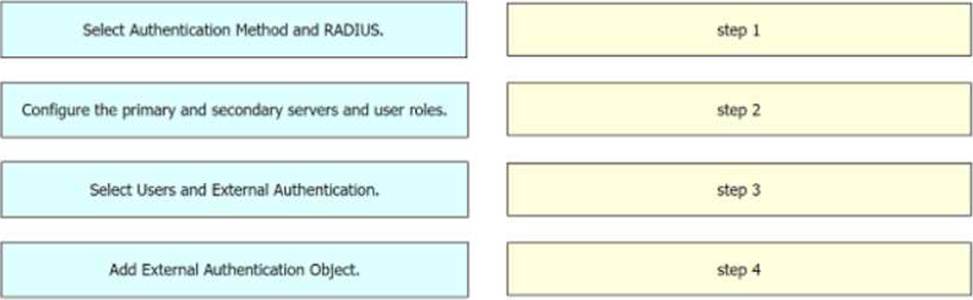
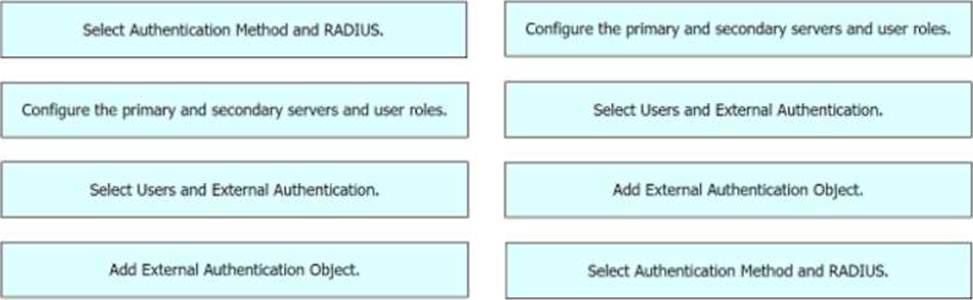
DRAG DROP
Drag and drop the configuration steps from the left into the sequence on the right to enable external authentication on Cisco FMC to a RADIUS server.
Which feature within the Cisco FMC web interface allows for detecting, analyzing and blocking malware in network traffic?
- A . intrusion and file events
- B . Cisco AMP for Endpoints
- C . Cisco AMP for Networks
- D . file policies
Which command is run on an FTD unit to associate the unit to an FMC manager that is at IP address 10.0.0.10, and that has the registration key Cisco123?
- A . configure manager local 10.0.0.10 Cisco123
- B . configure manager add Cisco123 10.0.0.10
- C . configure manager local Cisco123 10.0.0.10
- D . configure manager add 10.0.0.10 Cisco123