
Cisco 300-710 Practice Exams
Last updated on Nov 16,2026- Exam Code: 300-710
- Exam Name: Securing Networks with Cisco Firepower (SNCF)
- Certification Provider: Cisco
- Latest update: Nov 16,2026
Which action must be taken to configure an isolated bridge group for IRB mode on a Cisco Secure Firewall device?
- A . Add the restricted segment to the ACL.
- B . Leave BVI interface name empty.
- C . Define the NAT pool for the blocked traffic.
- D . Remove the route from the routing table.
Refer to the exhibit.
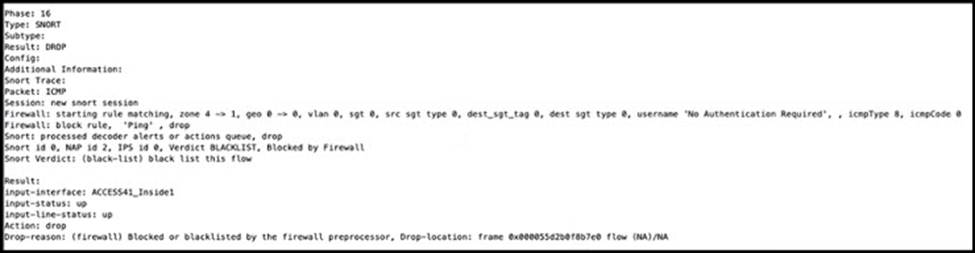
A systems administrator conducts a connectivity test to their SCCM server from a host machine and gets no response from the server.
Which action ensures that the ping packets reach the destination and that the host receives replies?
- A . Create an access control policy rule that allows ICMP traffic.
- B . Configure a custom Snort signature to allow ICMP traffic after Inspection.
- C . Modify the Snort rules to allow ICMP traffic.
- D . Create an ICMP allow list and add the ICMP destination to remove it from the implicit deny list.
A security engineer is configuring an Access Control Policy for multiple branch locations These locations share a common rule set and utilize a network object called INSIDE_NET which contains the locally significant internal network subnets at each location.
What technique will retain the policy consistency at each location but allow only the locally significant network subnet within the applicable rules?
- A . utilizing policy inheritance
- B . utilizing a dynamic ACP that updates from Cisco Talos
- C . creating a unique ACP per device
- D . creating an ACP with an INSIDE_NET network object and object overrides
A network engineer must configure an existing firewall to have a NAT configuration. The now configuration must support more than two interlaces per context. The firewall has previously boon operating transparent mode. The Cisco Secure Firewall Throat Defense (FTD) device has been deregistered from Cisco Secure Firewall Management Center (FMC).
Which set of configuration actions must the network engineer take next to meet the requirements?
- A . Run the configure manager add routed command from the Secure FTD device CL1, and reregister with Secure FMC.
- B . Run the configure firewall routed command from the Secure FTD device CD, and reregister with Secure FMC.
- C . Run the configure manager add routed command from the Secure FMC CLI. and reregister with Secure FMC.
- D . Run the configure firewall routed command from the Secure FMC CLI. and reregister with Secure FMC.
Which two conditions are necessary for high availability to function between two Cisco FTD devices? (Choose two.)
- A . The units must be the same version
- B . Both devices can be part of a different group that must be in the same domain when configured within the FMC.
- C . The units must be different models if they are part of the same series.
- D . The units must be configured only for firewall routed mode.
- E . The units must be the same model.
Which command-line mode is supported from the Cisco Firepower Management Center CLI?
- A . privileged
- B . user
- C . configuration
- D . admin
An organization recently implemented a transparent Cisco FTD in their network.
They must ensure that the device does not respond to insecure SSL/TLS protocols.
Which action accomplishes the task?
- A . Modify the device’s settings using the device management feature within Cisco FMC to force only secure protocols.
- B . Use the Cisco FTD platform policy to change the minimum SSL version on the device to TLS 1.2.
- C . Enable the UCAPL/CC compliance on the device to support only the most secure protocols available.
- D . Configure a FlexConfig object to disable any insecure TLS protocols on the Cisco FTD device.
A network administrator is reviewing a weekly scheduled attacks risk report and notices a host that is flagged for an impact 2 attack.
Where should the administrator look within Cisco FMC to find out more relevant information about this host and attack?
- A . Analysis > Lookup > Whols
- B . Analysis > Correlation > Correlation Events
- C . Analysis > Hosts > Vulnerabilities
- D . Analysis > Hosts > Host Attributes
IT management is asking the network engineer to provide high-level summary statistics of the Cisco FTD appliance in the network. The business is approaching a peak season so the need to maintain business uptime is high.
Which report type should be used to gather this information?
- A . Malware Report
- B . Standard Report
- C . SNMP Report
- D . Risk Report
An engineer is setting up a remote access VPN on a Cisco FTD device and wants to define which traffic gets sent over the VPN tunnel.
Which named object type in Cisco FMC must be used to accomplish this task?
- A . split tunnel
- B . crypto map
- C . access list
- D . route map