
Check Point 156-315.81.20 Practice Exams
Last updated on Oct 24,2026- Exam Code: 156-315.81.20
- Exam Name: Check Point Certified Security Expert - R81.20
- Certification Provider: Check Point
- Latest update: Oct 24,2026
Fill in the blank: Permanent VPN tunnels can be set on all tunnels in the community, on all tunnels for specific gateways, or ______ .
- A . On all satellite gateway to satellite gateway tunnels
- B . On specific tunnels for specific gateways
- C . On specific tunnels in the community
- D . On specific satellite gateway to central gateway tunnels
C
Explanation:
Permanent VPN tunnels can be set on all tunnels in the community, on all tunnels for specific gateways, or on specific tunnels in the community. Permanent VPN tunnels are always active and prevent VPN tunnel negotiation failures due to idle time or traffic volume. You can configure permanent VPN tunnels in SmartConsole by selecting the Permanent Tunnel option in the VPN Community Properties window.
Packet acceleration (SecureXL) identifies connections by several attributes.
Which of the attributes is NOT used for identifying connection?
- A . Source Address
- B . Destination Address
- C . TCP Acknowledgment Number
- D . Source Port
C
Explanation:
The attribute that is not used for identifying a connection by packet acceleration (SecureXL) is TCP Acknowledgment Number. SecureXL identifies connections by using a hash function that takes into account the following attributes: source address, destination address, source port, destination port, protocol, and VPN ID. The TCP Acknowledgment Number is not part of the hash function and does not affect the connection identification.
Reference: [SecureXL Mechanism]
https //sc1.checkpoint.com/documents/R77/CP R77_Firewall_WebAdmm/92711.htm
Identity Awareness allows the Security Administrator to configure network access based on which of the following?
- A . Name of the application, identity of the user, and identity of the machine
- B . Identity of the machine, username, and certificate
- C . Browser-Based Authentication, identity of a user, and network location
- D . Network location, identity of a user, and identity of a machine
D
Explanation:
Implied rules are predefined rules that are automatically added to the Access Control rulebase by the Security Management Server. Implied rules allow the control connections that are essential for the functionality and security of the Check Point products, such as communication between the Security Gateway and the Security Management Server, synchronization between cluster members, logging, VPN, and ICMP. Implied rules are not visible in the SmartConsole, but they can be viewed and modified using the Global Properties window.
The references are:
Check Point Certified Security Expert R81.20 (CCSE) Core Training, slide 12
Check Point R81 Quantum Security Gateway Guide, page 141
Check Point R81 Firewall Administration Guide, page 21
When SecureXL is enabled, all packets should be accelerated, except packets that match the following conditions:
- A . All UDP packets
- B . All IPv6 Traffic
- C . All packets that match a rule whose source or destination is the Outside Corporate Network
- D . CIFS packets
D
Explanation:
When SecureXL is enabled, all packets should be accelerated, except packets that match the following conditions: CIFS packets. SecureXL is a technology that accelerates network traffic processing by offloading intensive operations from the Firewall kernel to a dedicated SecureXL device. However, some packets cannot be accelerated by SecureXL due to various reasons, such as unsupported features, security policy settings, or protocol limitations. One example of packets that cannot be accelerated by SecureXL are CIFS packets, which are used for file sharing and access over SMB protocol. CIFS packets are not accelerated by SecureXL because they require stateful inspection by the Firewall kernel.
Capsule Connect and Capsule Workspace both offer secured connection for remote users who are using their mobile devices. However, there are differences between the two.
Which of the following statements correctly identify each product’s capabilities?
- A . Workspace supports ios operating system, Android, and WP8, whereas Connect supports ios operating system and Android only
- B . For compliance/host checking, Workspace offers the MDM cooperative enforcement, whereas Connect offers both jailbreak/root detection and MDM cooperative enforcement.
- C . For credential protection, Connect uses One-time Password login support and has no SSO support, whereas Workspace offers both One-Time Password and certain SSO login support.
- D . Workspace can support any application, whereas Connect has a limited number of application types which it will support.
C
Explanation:
According to the Check Point website, Capsule Connect and Capsule Workspace both offer secured connection for remote users who are using their mobile devices. However, there are differences between the two. For credential protection, Connect uses One-time Password login support and has no SSO support, whereas Workspace offers both One-Time Password and certain SSO login support. The other statements are either false or partially true.
Reference: Capsule Connect and Capsule Workspace
Which command will reset the kernel debug options to default settings?
- A . fw ctl dbg -a 0
- B . fw ctl dbg resetall
- C . fw ctl debug 0
- D . fw ctl debug set 0
C
Explanation:
The command fw ctl debug 0 will reset the kernel debug options to default settings. This command will disable all the debug flags and clear the debug buffer. It is recommended to use this command before and after performing a kernel debug, to avoid any interference or confusion with other debug outputs. The command fw ctl debug 0 is also equivalent to fw ctl debug -buf 0.
Reference: Best Practices – HTTPS Inspection – Check Point Software, section “How to perform a Kernel Debug” LOGGINGAND MONITORING R81 – Check Point Software, page 104
What is the purpose of Captive Portal?
- A . It authenticates users, allowing them access to the Gaia OS
- B . It authenticates users, allowing them access to the Internet and corporate resources
- C . It provides remote access to SmartConsole
- D . It manages user permission in SmartConsole
B
Explanation:
Captive Portal is a feature of Identity Awareness Software Blade that enables you to identify users who are not authenticated by other methods, such as Active Directory or VPN. Captive Portal redirects users to a web page where they can enter their credentials and be authenticated by an external server, such as LDAP or RADIUS. After authentication, users can access the Internet and corporate resources according to the security policy rules that apply to their identity.
The references are:
Check Point R81 Identity Awareness Administration Guide, page 9 Configuring Browser-Based Authentication in SmartConsole
What API command below creates a new host with the name “New Host” and IP address of “192.168.0.10”?
- A . new host name “New Host” ip-address “192.168.0.10”
- B . set host name “New Host” ip-address “192.168.0.10”
- C . create host name “New Host” ip-address “192.168.0.10”
- D . add host name “New Host” ip-address “192.168.0.10”
D
Explanation:
The API command to create a new host with the name "New Host" and IP address "192.168.0.10" is:
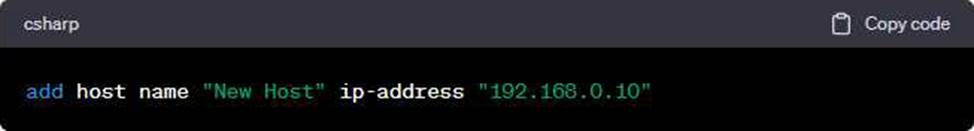
This command adds a host object with the specified name and IP address to the Check Point configuration.
Reference: Check Point documentation or training materials related to API commands.
What processes does CPM control?
- A . Object-Store, Database changes, CPM Process and web-services
- B . web-services, CPMI process, DLEserver, CPM process
- C . DLEServer, Object-Store, CP Process and database changes
- D . web_services, dle_server and object_Store
D
Explanation:
CPM stands for Check Point Management, which is a process that runs on the Security Management server and controls the management operations, such as policy installation, object creation, configuration backup, etc. CPM also controls other processes that are related to the management functions, such as:
web_services: This process is responsible for providing web services for the communication between SmartConsole and the Security Management server. It handles requests from SmartConsole clients and forwards them to CPM or other processes.
dle_server: This process is responsible for managing the log files and indexes. It handles queries from SmartLog and SmartEvent and provides log data to CPM or other processes.
object_Store: This process is responsible for storing and retrieving objects from the database. It handles requests from CPM or other processes and provides object data. Therefore, the correct answer is D)
The other options are incorrect because:
A) Object-Store, Database changes, CPM Process and web-services: This option includes some processes that are controlled by CPM, such as Object-Store, CPM Process, and web-services, but it also includes Database changes, which is not a process but an action performed by CPM or other processes.
B) web-services, CPMI process, DLEserver, CPM process: This option includes some processes that are controlled by CPM, such as web-services, DLEserver, and CPM process, but it also includes CPMI process, which is not a process but a protocol used by CPM or other processes to communicate with each other.
C) DLEServer, Object-Store, CP Process and database changes: This option includes some processes that are controlled by CPM, such as DLEServer and Object-Store, but it also includes CP Process and database changes, which are not processes but a generic term for any Check Point process and an action performed by CPM or other processes respectively.
Reference: Check Point Processes and Daemons, Check Point Processes Cheat Sheet, Check Point Firewall Security Solution
Which is the lowest gateway version supported by R81.20 management server?
- A . R77.30
- B . R80.20
- C . R77
- D . R65
A
Explanation:
The lowest gateway version supported by R81.20 management server is R77.30. According to the Check Point Release Map1, you can upgrade to R81.20 from R77.30, R80, R80.10, R80.20.M1, R80.20, R80.20SP, R80.20.M2, R80.20 3.10, R80.30, R80.30 3.10, R80.30SP, R80.40, R81 and R81.20. However, to upgrade from R77.30, R80 and R80.10, you first need to upgrade to R80.40. For more information, you can refer to the Check Point R81.20 (Titan) Release Home page2 or the Certified Security Expert (CCSE) R81.20 Course Overview3.