
Amazon DVA-C02 Practice Exams
Last updated on Oct 23,2026- Exam Code: DVA-C02
- Exam Name: AWS Certified Developer - Associate
- Certification Provider: Amazon
- Latest update: Oct 23,2026
A company is working on a new serverless application. A developer needs to find an automated way to deploy AWS Lambda functions and the dependent Infrastructure with minimum coding effort. The application also needs to be reliable.
Which method will meet these requirements with the LEAST operational overhead?
- A . Build the application by using shell scripts to create .zip files for each Lambda function. Manually upload the .zip files to the AWS Management Console.
- B . Build the application by using the AWS Serverless Application Model (AWS SAM). Use a continuous integration and continuous delivery (CI/CD) pipeline and the SAM CLI to deploy the Lambda functions.
- C . Build the application by using shell scripts to create .zip files for each Lambda function. Upload the .zip files. Deploy the .zip files as Lambda functions by using the AWS CLI in a continuous integration and continuous delivery (CI/CD) pipeline.
- D . Build a container for each Lambda function. Store the container images in AWS CodeArtifact. Deploy the containers as Lambda functions by using the AWS CLI in a continuous integration and continuous delivery (CI/CD) pipeline.
A developer compiles an AWS Lambda function and packages the result as a .zip file. The developer uses the Functions page on the Lambda console to attempt to upload the local packaged .zip file.
When pushing the package to Lambda, the console returns the following error:
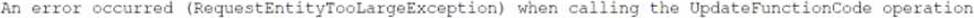
Which solutions can the developer use to publish the code? (Select TWO.)
- A . Upload the package to Amazon S3. Use the Functions page on the Lambda console to upload the package from the S3 location.
- B . Create an AWS Support ticket to increase the maximum package size.
- C . Use the update-function-code AWS CLI command. Pass the -publish parameter.
- D . Repackage the Lambda function as a Docker container image. Upload the image to Amazon Elastic Container Registry {Amazon ECR). Create a new Lambda function by using the Lambda console. Reference the image that is deployed to Amazon ECR.
- E . Sign the .zip file digitally. Create a new Lambda function by using the Lambda console. Update the configuration of the new Lambda function to include the Amazon Resource Name (ARN) of the code signing configuration.
A developer has written a distributed application that uses micro services. The microservices are running on Amazon EC2 instances. Because of message volume, the developer is unable to match log output from each microservice to a specific transaction. The developer needs to analyze the message flow to debug the application.
Which combination of steps should the developer take to meet this requirement? (Select TWO.)
- A . Download the AWS X-Ray daemon. Install the daemon on an EC2 instance. Ensure that the EC2 instance allows UDP traffic on port 2000.
- B . Configure an interface VPC endpoint to allow traffic to reach the global AWS X-Ray daemon on TCP port 2000.
- C . Enable AWS X-Ray. Configure Amazon CloudWatch to push logs to X-Ray.
- D . Add the AWS X-Ray software development kit (SDK) to the microservices. Use X-Ray to trace requests that each microservice makes.
- E . Set up Amazon CloudWatch metric streams to collect streaming data from the microservices.
A company runs continuous integration/continuous delivery (CI/CD) pipelines for its application on AWS CodePipeline. A developer must write unit tests and run them as part of the pipelines before staging the artifacts for testing.
How should the developer incorporate unit tests as part of CI/CD pipelines?
- A . Create a separate CodePipeline pipeline to run unit tests.
- B . Update the AWS CodeBuild build specification to include a phase for running unit tests.
- C . Install the AWS CodeDeploy agent on an Amazon EC2 instance to run unit tests.
- D . Create a testing branch in a git repository for the pipelines to run unit tests.
A developer warns to add request validation to a production environment Amazon API Gateway API.
The developer needs to test the changes before the API is deployed to the production environment.
For the lest the developer will send test requests to the API through a testing tool.
Which solution will meet these requirements with the LEAST operational overhead?
- A . Export the existing API to an OpenAPI file. Create a new API Import the OpenAPI file Modify the new API to add request validation. Perform the tests Modify the existing API to add request validation. Deploy the existing API to production.
- B . Modify the existing API to add request validation. Deploy the updated API to a new API Gateway stage Perform the tests Deploy the updated API to the API Gateway production stage.
- C . Create a new API Add the necessary resources and methods including new request validation. Perform the tests Modify the existing API to add request validation. Deploy the existing API to production.
- D . Clone the exiting API Modify the new API lo add request validation. Perform the tests Modify the existing API to add request validation Deploy the existing API to production.
D
Explanation:
This solution allows the developer to test the changes without affecting the production environment. Cloning an API creates a copy of the API definition that can be modified independently. The developer can then add request validation to the new API and test it using a testing tool. After verifying that the changes work as expected, the developer can apply the same changes to the existing API and deploy it to production.
Reference: Clone an API, [Enable Request Validation for an API in API Gateway]
A company regularly receives route status updates from its delivery trucks as events in Amazon EventBridge. The company is building an API-based application in a VPC that will consume and process the events to create a delivery status dashboard. The API application must not be available by using public IP addresses because of security and compliance requirements.
How should the company send events from EventBridge to the API application?
- A . Create an AWS Lambda function that runs in the same VPC as the API application. Configure the function as an EventBridge target. Use the function to send events to the API.
- B . Create an internet-facing Application Load Balancer (ALB) in front of the API application. Associate a security group with rules that block access from all external sources except for EventBridge. Configure the ALB as an EventBridge target.
- C . Create an internet-facing Network Load Balancer (NLB) in front of the API application. Associate a security group with rules that block access from all external sources except for EventBridge. Configure the NLB as an EventBridge target.
- D . Use the application API endpoint in the VPC as a target for EventBridge. Send events directly to the application API endpoint from EventBridge.
A
Explanation:
Why Option A is Correct:
Running an AWS Lambda function within the same VPC ensures secure communication without exposing the API application to public IP addresses. The Lambda function can serve as a secure EventBridge target to send events to the API.
Why Other Options are Incorrect:
Option B & C: Internet-facing load balancers expose public IP addresses, which violates compliance requirements.
Option D: EventBridge cannot directly target an endpoint within a private VPC without intermediary services like Lambda.
AWS Documentation
Reference: EventBridge Targets
A company has an analytics application that uses an AWS Lambda function to process transaction data asynchronously A developer notices that asynchronous invocations of the Lambda function sometimes fail When failed Lambda function invocations occur, the developer wants to invoke a second Lambda function to handle errors and log details.
Which solution will meet these requirements?
- A . Configure a Lambda function destination with a failure condition Specify Lambda function as the destination type Specify the error-handling Lambda function’s Amazon Resource Name (ARN) as the resource
- B . Enable AWS X-Ray active tracing on the initial Lambda function. Configure X-Ray to capture stack traces of the failed invocations. Invoke the error-handling Lambda function by including the stack traces in the event object.
- C . Configure a Lambda function trigger with a failure condition Specify Lambda function as the destination type Specify the error-handling Lambda function’s Amazon Resource Name (ARN) as the resource
- D . Create a status check alarm on the initial Lambda function. Configure the alarm to invoke the error-handling Lambda function when the alarm is initiated. Ensure that the alarm passes the stack trace in the event object.
A
Explanation:
Lambda Destinations on Failure: Allow routing asynchronous function invocations to specified resources (like another Lambda function) upon failure.
Error Handling: The error-handling Lambda receives details about the failure, enabling logging and custom actions.
Direct Integration: This solution leverages native Lambda functionality for a simpler implementation.
A developer is preparing to deploy an AWS CloudFormation stack for an application from a template that includes an IAM user.
The developer needs to configure the application’s resources to retain the IAM user after successful creation. However, the developer also needs to configure the application to delete the IAM user if the stack rolls back.
- A . Update CloudFormation template with the following deletion policy:
AWSTemplateFormatVersion: ‘2010-05-09’
Resources:
appUser:
Type: AWS::IAM::User
DeletionPolicy: Retain - B . Update CloudFormation template with the following deletion policy:
AWSTemplateFormatVersion: ‘2010-09-09’
Resources:
appUser:
Type: AWS::IAM::User
DeletionPolicy: RetainExceptOnCreate - C . Update the CloudFormation service role to include the following policy:
{
"Version": "2012-10-17",
"Statement": [{
"Effect": "Allow",
"Action": ["cloudformation:UpdateTerminationProtection"],
"Resource": "*"
}]
} - D . Update the stack policy to include the following statements:
{
"Statement": [{
"Effect": "Deny",
"Action": "Update:*",
"Principal": "*",
"Resource": "*",
"Condition": {
"StringEquals": {
"ResourceType": "AWS::IAM::User"
}
}
}]
}
B
Explanation:
Why Option B is Correct:
The RetainExceptOnCreate deletion policy ensures that the IAM user is retained after successful stack creation but is deleted if the stack creation fails or rolls back. This meets both requirements.
Why Other Options are Incorrect:
Option A: The Retain policy retains the resource regardless of stack status and does not delete the IAM user upon rollback.
Option C: Updating the service role for termination protection does not address the specific deletion behavior for the IAM user.
Option D: Stack policy controls updates, not resource deletion behavior during rollbacks.
AWS Documentation
Reference: CloudFormation DeletionPolicy Attribute
A developer is making changes to a custom application that uses AWS Elastic Beanstalk.
Which solutions will update the Elastic Beanstalk environment with the new application version after the developer completes the changes? (Select TWO.)
- A . Package the application code into a .zip file. Use the AWS Management Console to upload the .zip file and deploy the packaged application.
- B . Package the application code into a .tar file. Use the AWS Management Console to create a new application version from the .tar file. Update the environment by using the AWS CLI.
- C . Package the application code into a .tar file. Use the AWS Management Console to upload the .tar file and deploy the packaged application.
- D . Package the application code into a .zip file. Use the AWS CLI to create a new application version from the .zip file and to update the environment.
- E . Package the application code into a .zip file. Use the AWS Management Console to create a new application version from the .zip file. Rebuild the environment by using the AWS CLI.
A company has an Amazon S3 bucket containing premier content that it intends to make available to only paid subscribers of its website. The S3 bucket currently has default permissions of all objects being private to prevent inadvertent exposure of the premier content to non-paying website visitors.
How can the company Limit the ability to download a premier content file in the S3 Bucket to paid subscribers only?
- A . Apply a bucket policy that allows anonymous users to download the content from the S3 bucket.
- B . Generate a pre-signed object URL for the premier content file when a pad subscriber requests a download.
- C . Add a Docket policy that requires multi-factor authentication for request to access the S3 bucket objects.
- D . Enable server-side encryption on the S3 bucket for data protection against the non-paying website visitors.
B
Explanation:
This solution will limit the ability to download a premier content file in the S3 bucket to paid subscribers only because it uses a pre-signed object URL that grants temporary access to an S3 object
for a specified duration. The pre-signed object URL can be generated by the company’s website when a paid subscriber requests a download, and can be verified by Amazon S3 using the signature in the URL.
Option A is not optimal because it will allow anyone to download the content from the S3 bucket without verifying their subscription status.
Option C is not optimal because it will require additional steps and costs to configure multi-factor authentication for accessing the S3 bucket objects, which may not be feasible or user-friendly for paid subscribers.
Option D is not optimal because it will not prevent non-paying website visitors from accessing the S3 bucket objects, but only encrypt them at rest.
Reference: Share an Object with Others, [Using Amazon S3 Pre-Signed URLs]